You can install pfSense on Proxmox in two ways. Pass a physical network card’s ports through to the virtual machine, or give the VM VirtIO network cards on Linux bridges, which works without a spare NIC. Either way, pfSense CE 2.8 and newer install through the Netgate Installer, which downloads pfSense from Netgate during the install, so the VM’s WAN needs Internet before its first boot.
That is the biggest change since 2022, when you could download an ISO and install offline. The Proxmox steps and the pfSense GUI were checked in November 2026 on Proxmox VE 9.2.2 and pfSense CE 2.9.0, the current release. The guide to install OPNsense on Proxmox uses the same Proxmox setup.
Proxmox Requirements for a pfSense VM
You need a working Proxmox host (here’s how to install Proxmox VE) with room for a small VM. Netgate’s minimum requirements are a 64-bit CPU, 1 GB of RAM, an 8 GB disk and a compatible network card. Its Proxmox VE recipe adds the key settings for a Proxmox pfSense VM: OS type Other, a VirtIO Block disk, CPU type host and VirtIO (paravirtualized) network cards.
Decide how the VM reaches your network before you create it:
- Pass through a physical NIC if pfSense is going to be the router for your whole house. The VM gets two of the card’s ports for WAN and LAN, Proxmox keeps its own port, and the host needs IOMMU support (VT-d on Intel, AMD-Vi on AMD).
- Use virtual bridges if you don’t have a spare NIC, or you’d like to test pfSense first. The VM gets VirtIO network cards, and with a spare port it routes your home; on a one-port host, this guide builds a test network.
Disclosure: Some links below are Amazon affiliate links, which means that I earn a percentage of each sale at no cost to you. Thank you for your support.
The pfSense VM I built for tutorials (it’s in my May 2025 video on Proxmox changes) had a multi-port card’s ports passed through to it, one for WAN and one for LAN, and if pfSense will be your main router, that’s the path I’d pick, since the firewall owns its ports outright. If you’re buying a card for it, a dual-port card like the H!Fiber dual-port gigabit NIC built on the Intel I350 chip covers WAN and LAN in one slot.
Get the pfSense ISO for Proxmox
There’s no public ISO for current pfSense CE anymore. Netgate’s mirror stops at CE 2.7.2, and the pfSense download page now sends you to the Netgate Store. Netgate calls the Netgate Installer “the only available method for installing pfSense® software on all devices.” It is free, but it’s delivered through a checkout, so you’ll need a Netgate Store account.
1. Log in to the Netgate Store, open the Netgate Installer page and select the AMD64 ISO image, which Netgate’s download guide says “works well for installing via IPMI and for virtual machines.”
2. Select Add To Cart, then Enter Cart, and complete the checkout to download the image.
3. The download is gzip-compressed and Netgate’s SHA-256 is computed on the compressed file, so check the hash first, then decompress it with 7-Zip or gunzip. Safari decompresses downloads on its own, which makes the hash impossible to check, so turn that off or use another browser.
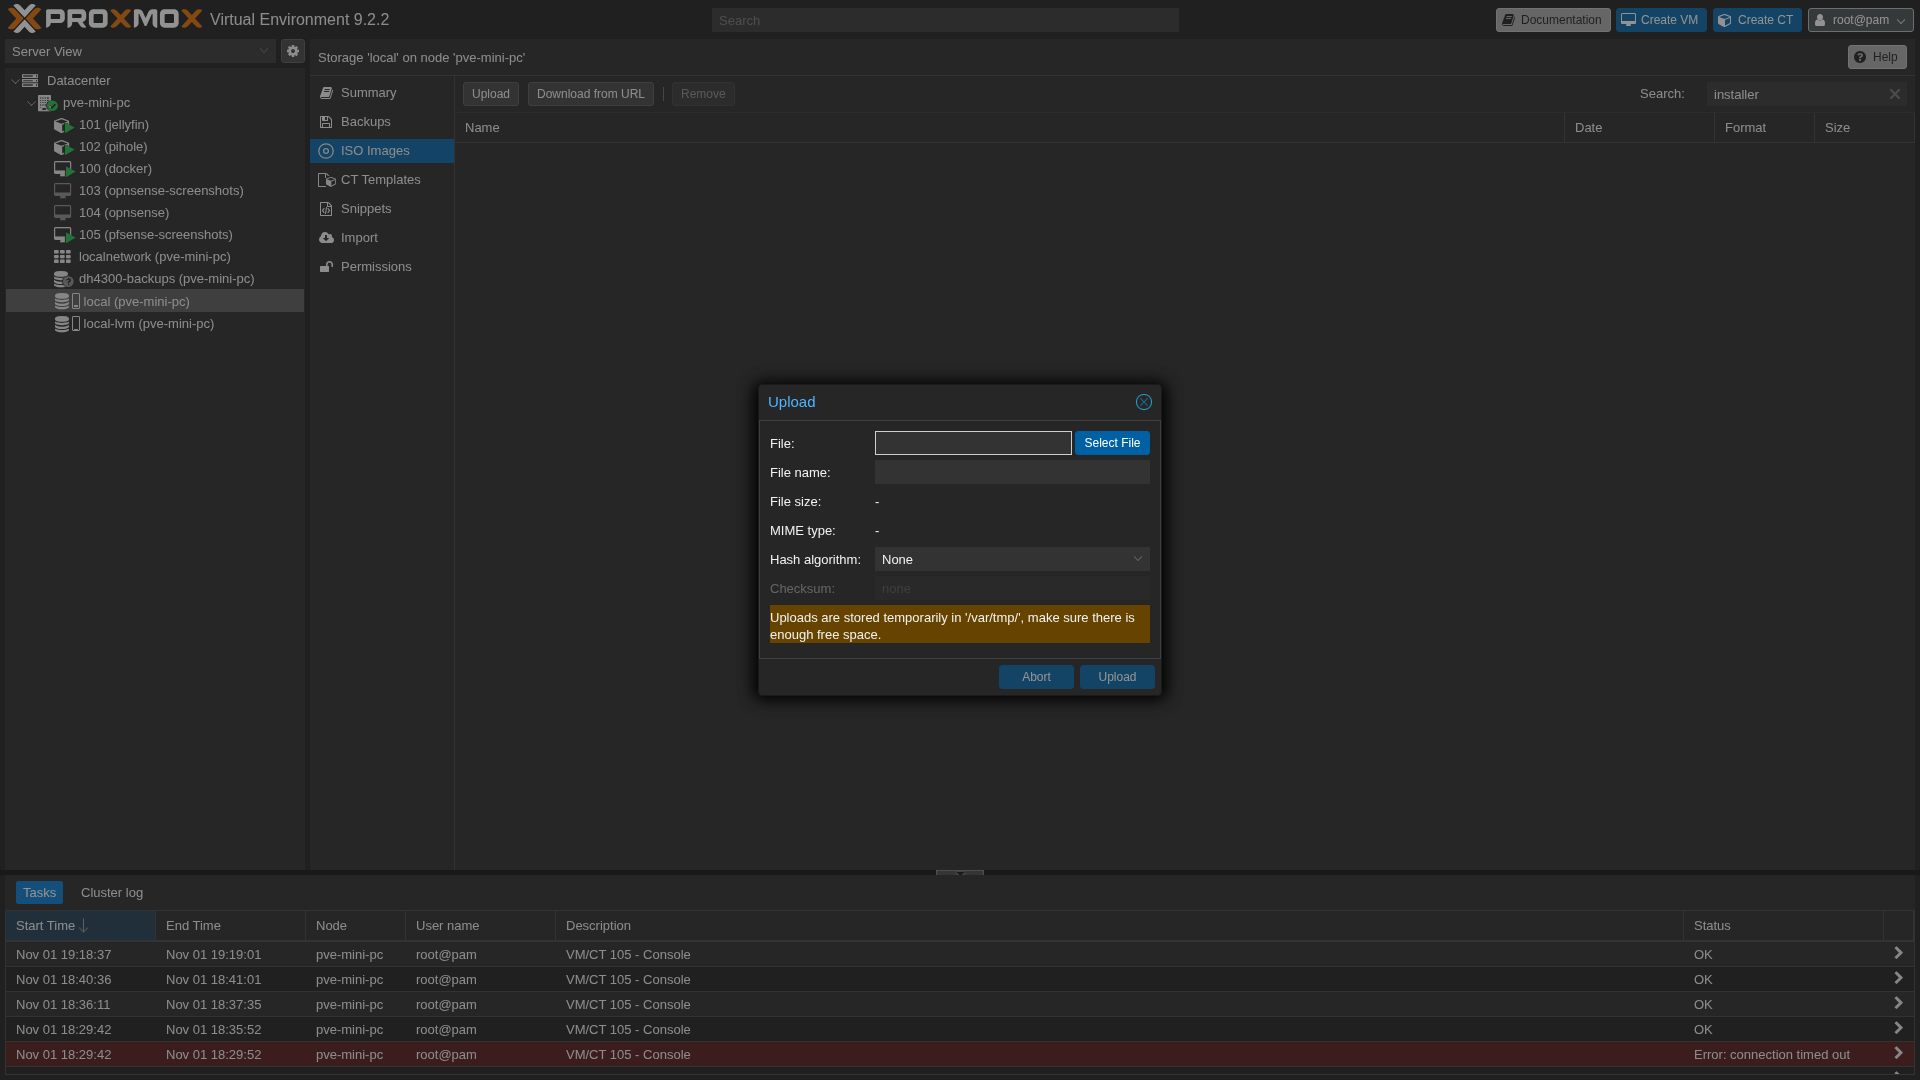
4. In Proxmox, select your node, then the local storage, and finally, ISO Images. Select Upload, choose the decompressed ISO, leave Hash algorithm on None, and select Upload again.
Create the pfSense VM in Proxmox
The wizard is the same for both paths until the Network tab.
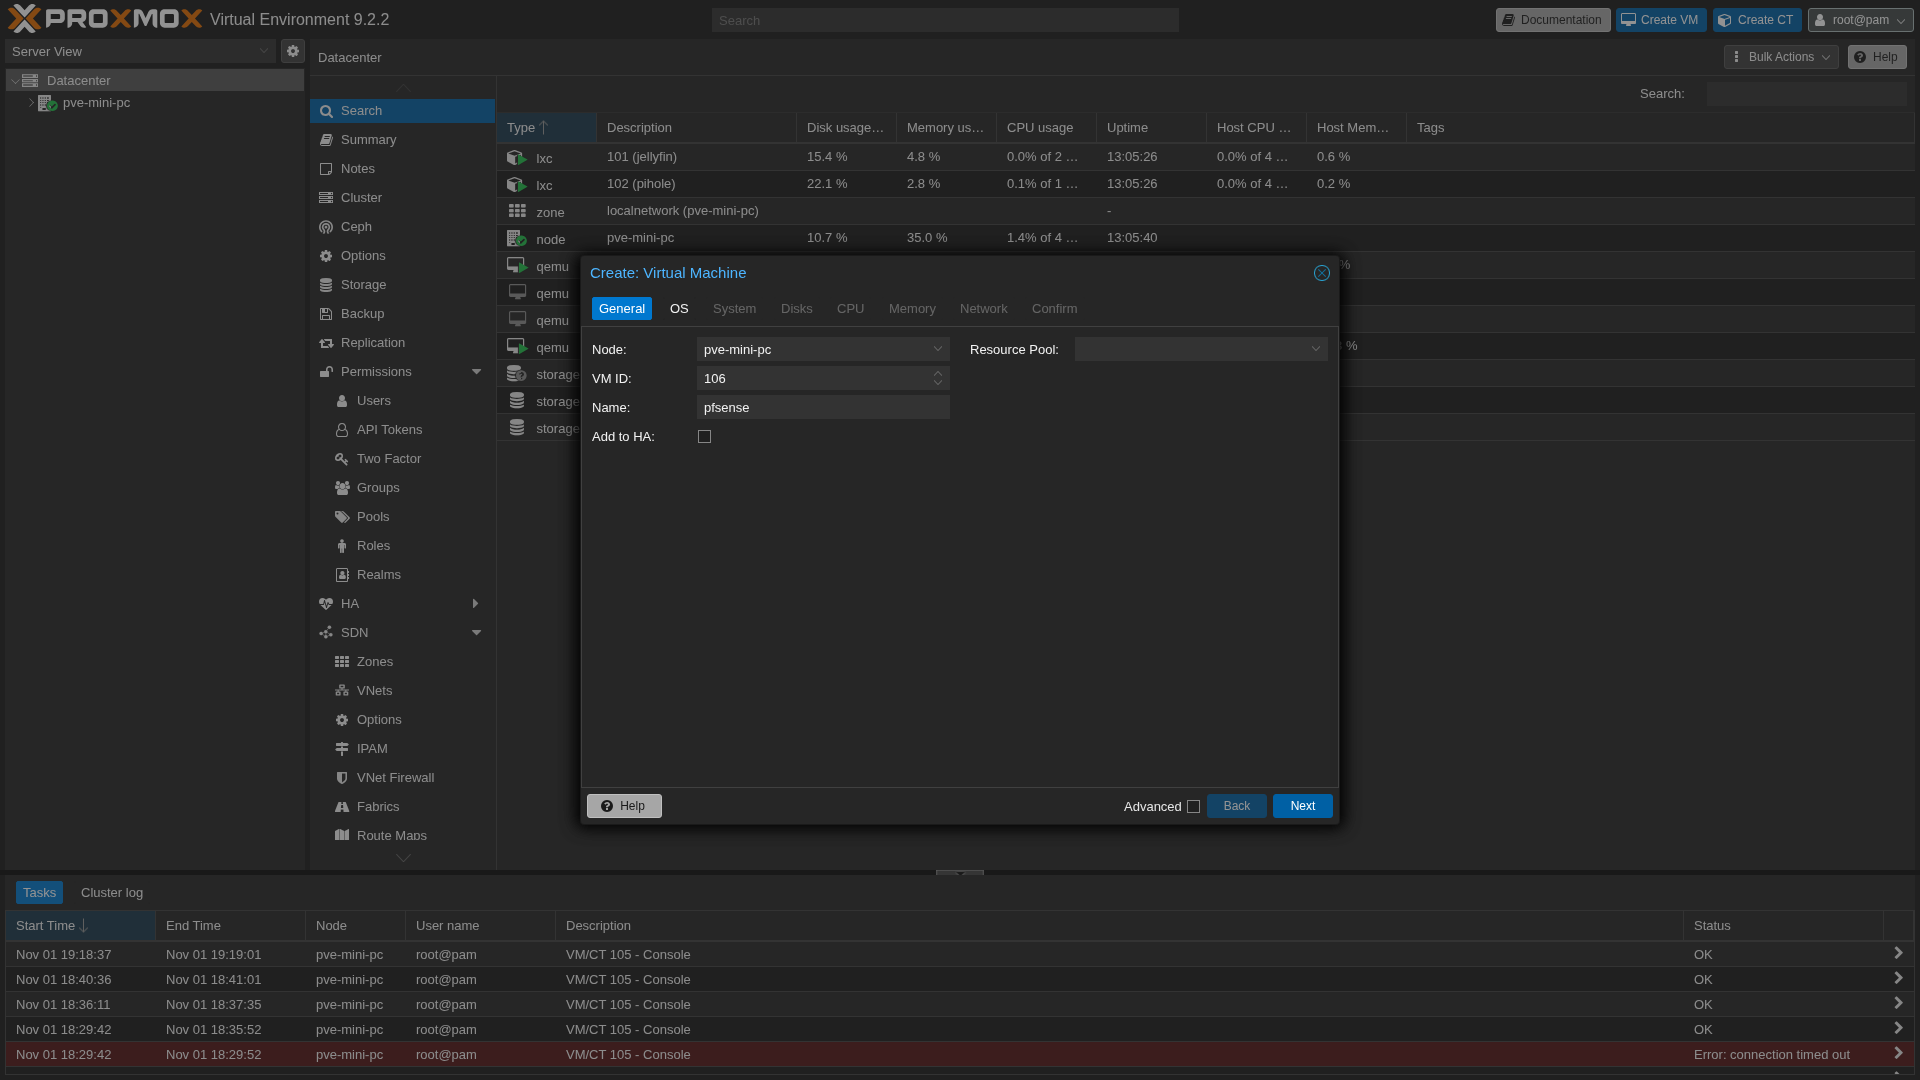
1. Select Create VM in the top right corner. On General, give the VM a Name like pfsense.
2. On OS, keep Use CD/DVD disc image file (iso), choose the local storage and the Netgate Installer ISO you uploaded, then set the Guest OS Type to Other.
3. On System, keep the defaults (i440fx and SeaBIOS).
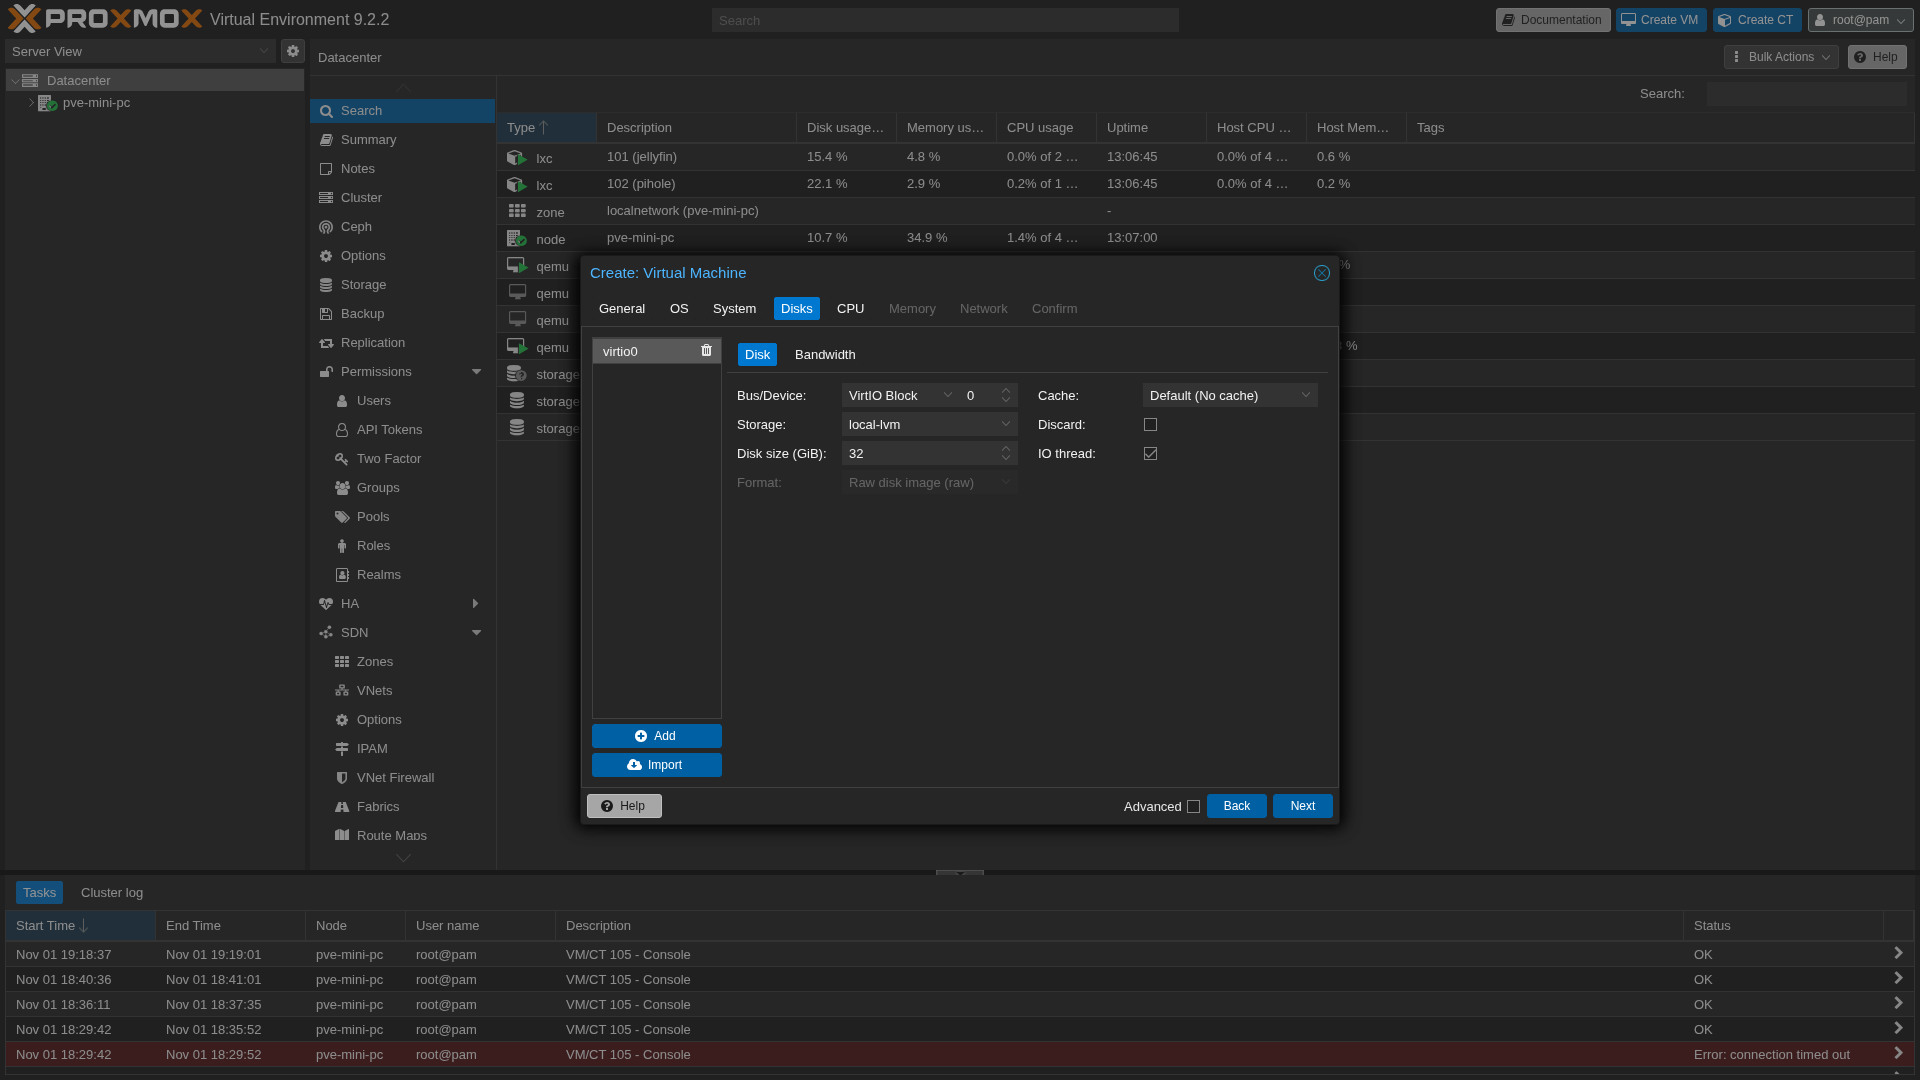
4. On Disks, change Bus/Device from IDE to VirtIO Block, as Netgate’s recipe does, and keep the 32 GiB default (Netgate’s floor is 8 GB).
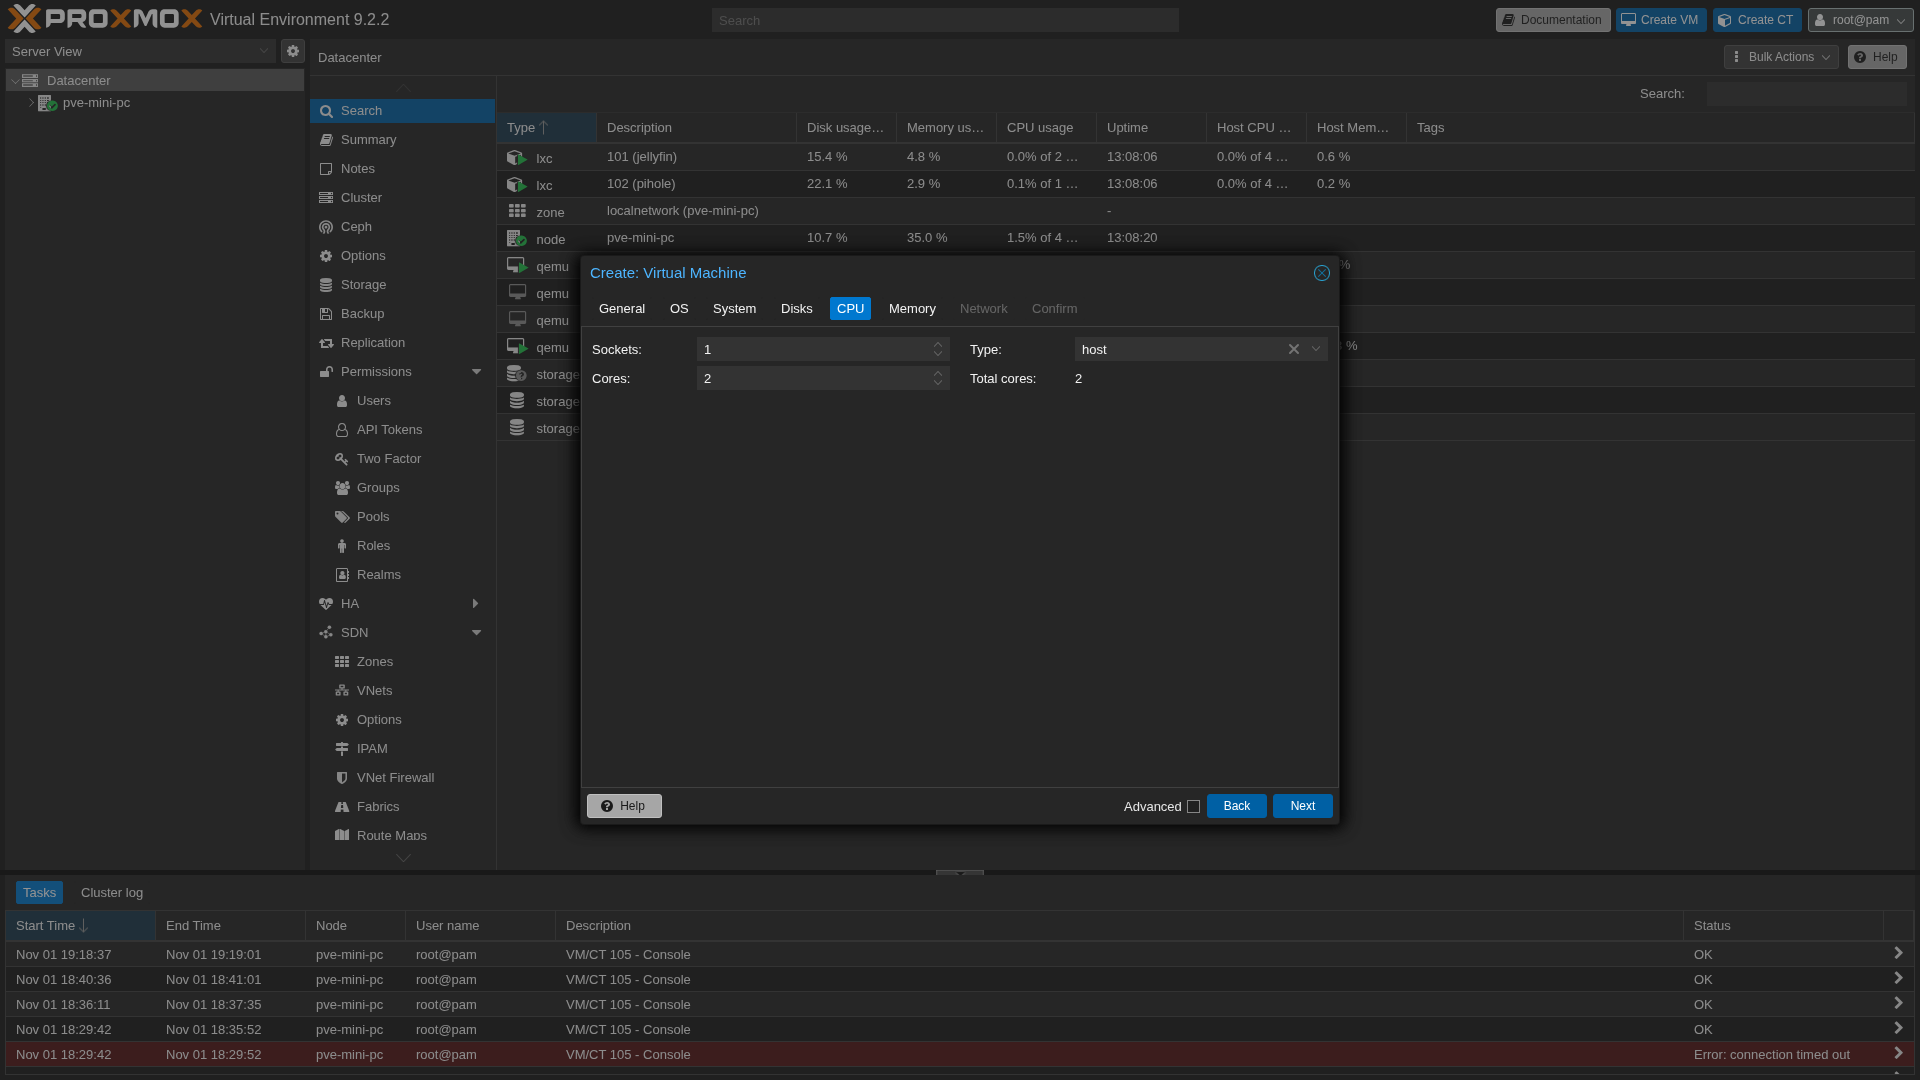
5. On CPU, set Cores to 2 (Netgate asks for one or more) and Type to host (type host to filter the list).
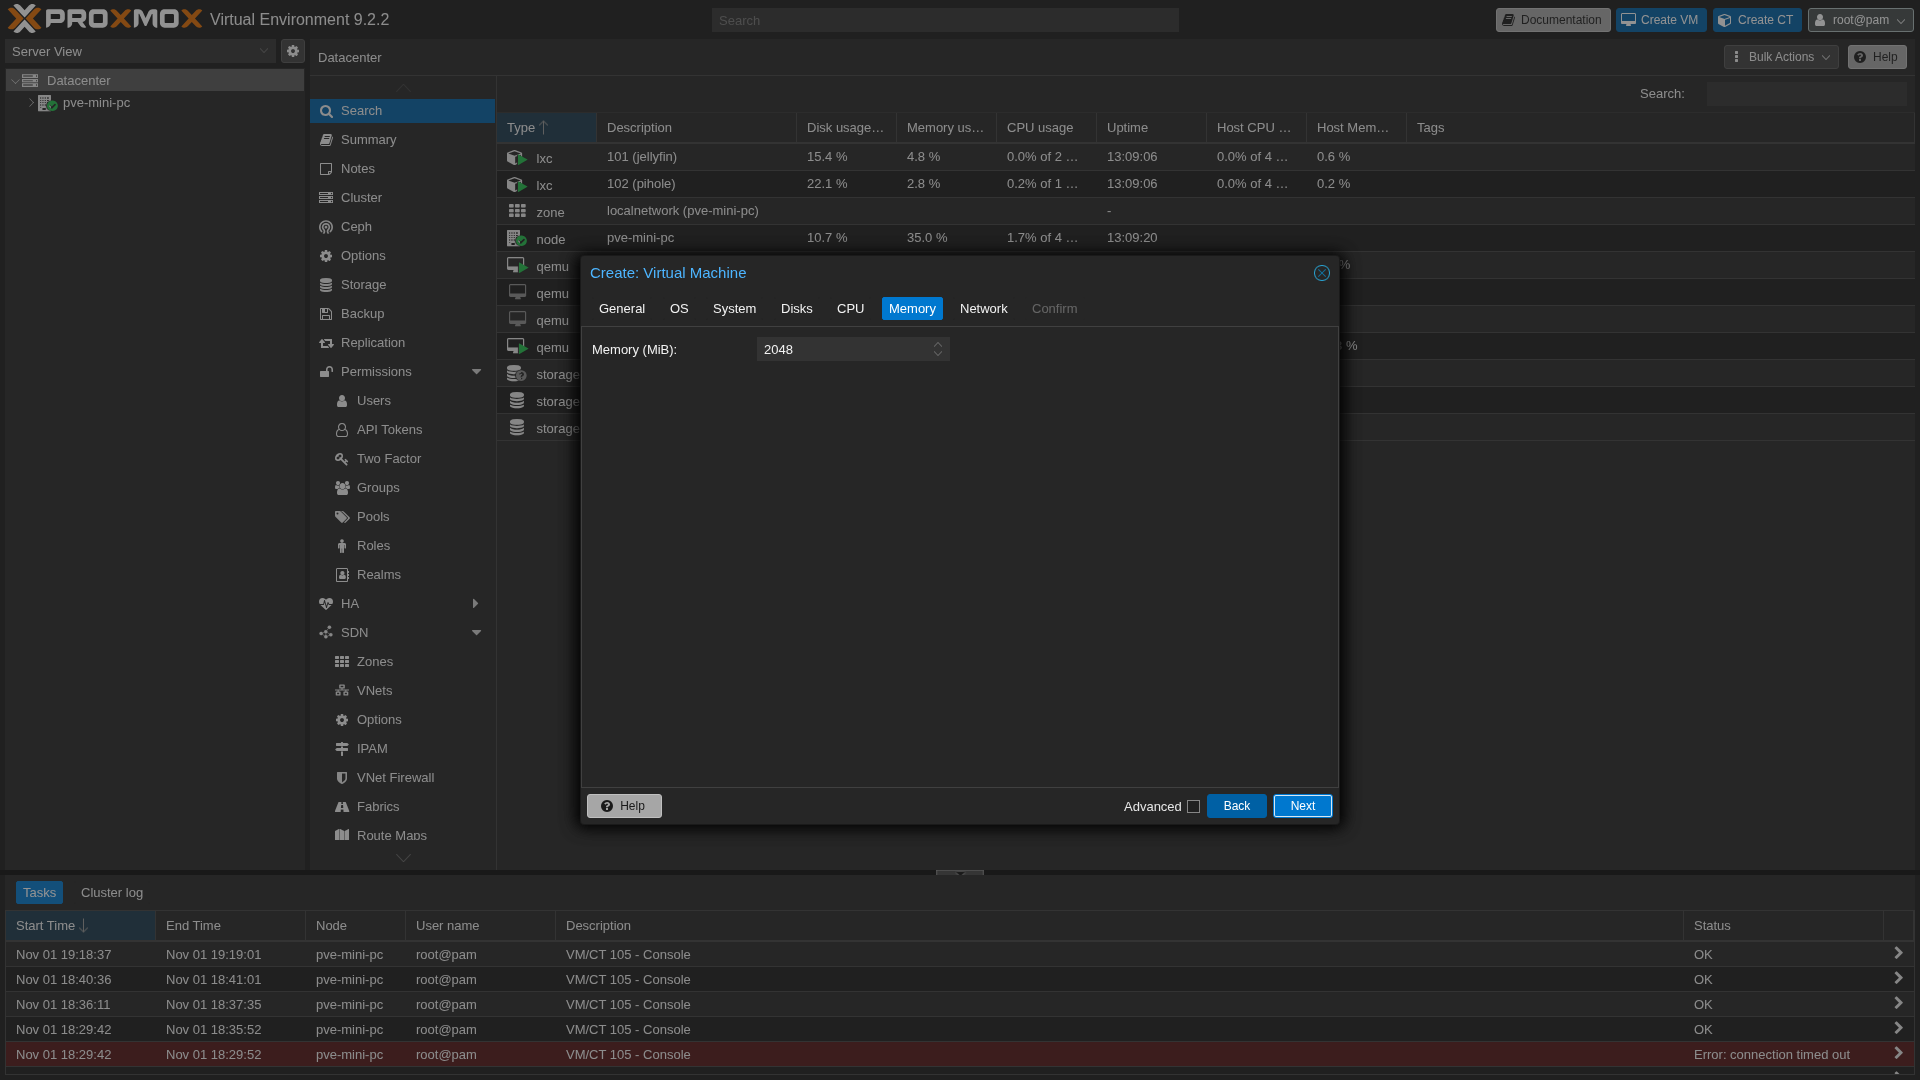
6. On Memory, keep the default 2048 MiB (Netgate’s minimum is 1024 MB).
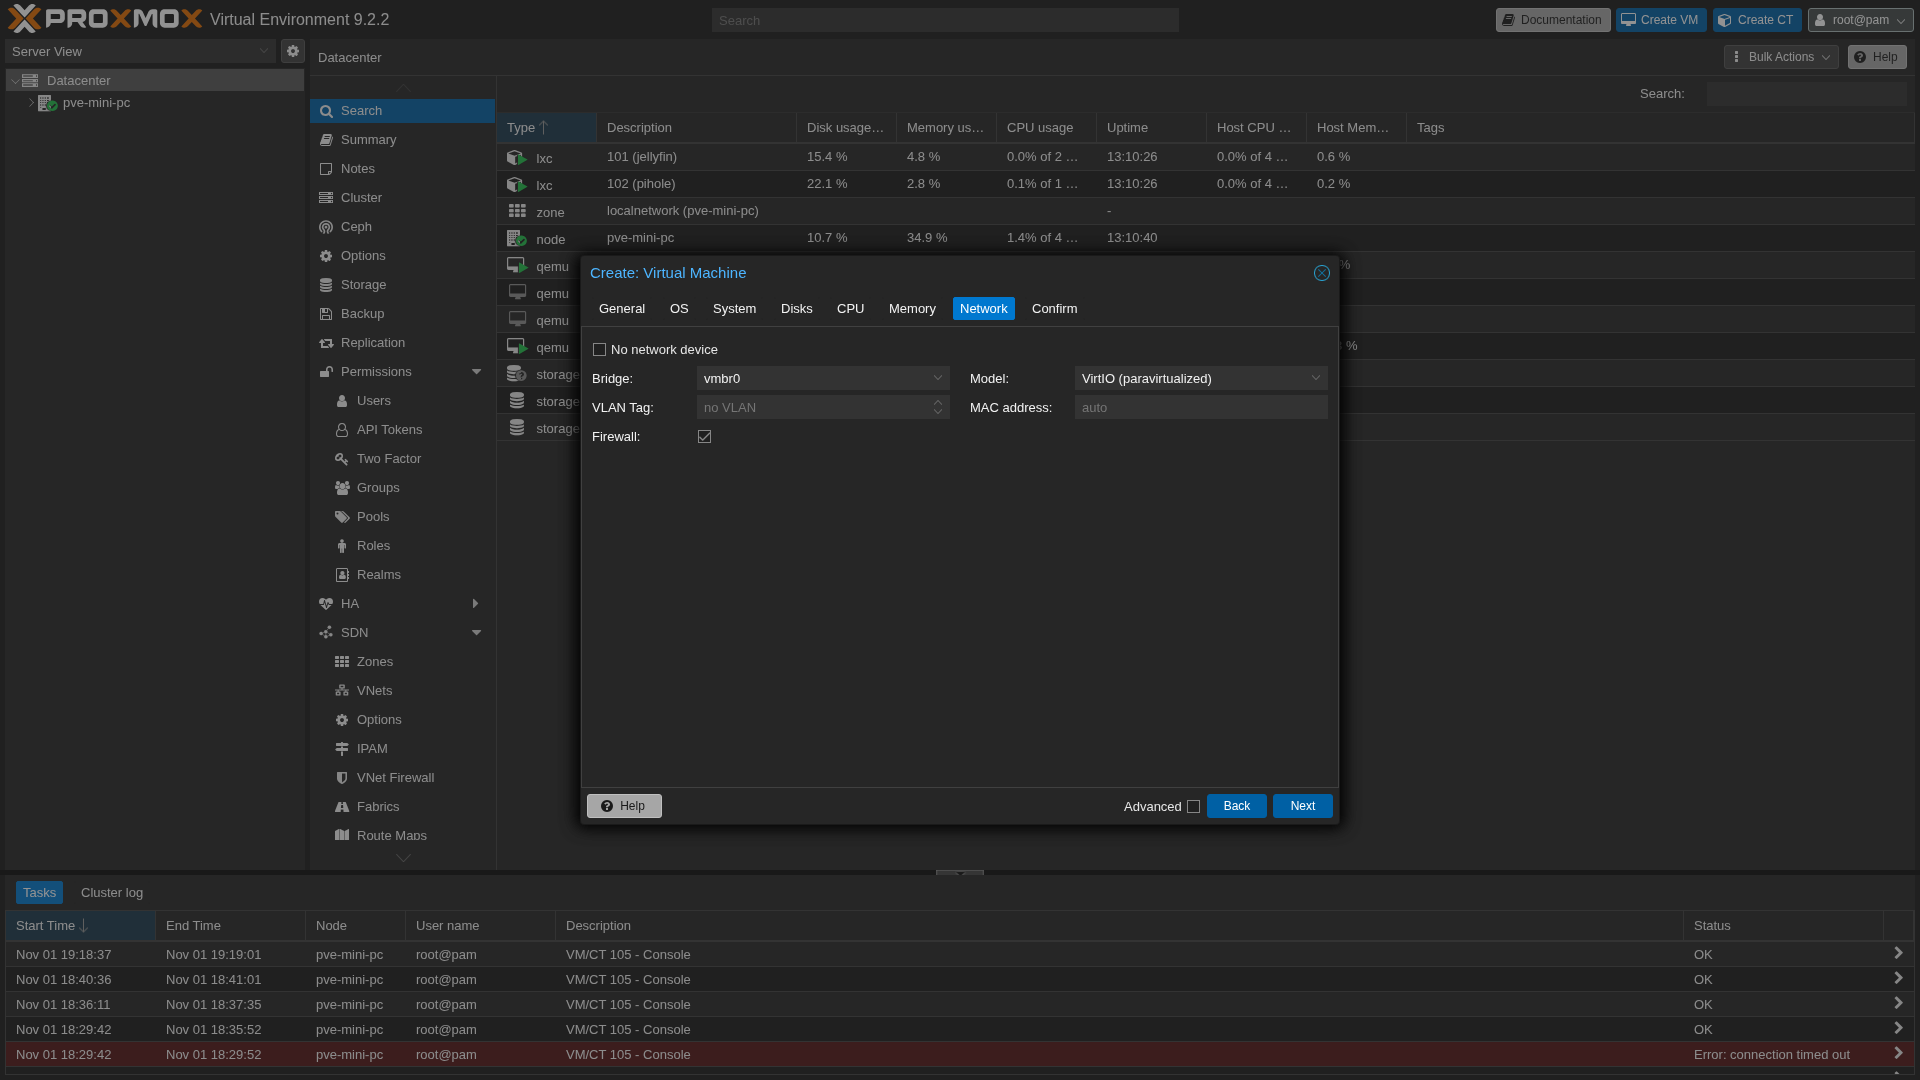
7. On Network, the choice depends on the path. For virtual bridges, keep Bridge on vmbr0 and change Model from Intel E1000 to VirtIO (paravirtualized). For passthrough, tick No network device, since you’ll add the card’s ports before the first boot.
8. On Confirm, check the summary, leave Start after created unticked (there is still hardware to add), and select Finish.
Option 1: Pass Through a Physical NIC to pfSense
With passthrough, pfSense talks to the card directly and the host stops using it, so never pass through the port vmbr0 uses, or you’ll lose the Proxmox web UI.
Turn On IOMMU and Load the VFIO Modules
Enable IOMMU in the host’s BIOS or UEFI first (usually called IOMMU or VT-d). The kernel turns it on by default for AMD CPUs, and for Intel CPUs from kernel 6.8. Proxmox VE 9.2 ships kernel 7.0, so the old intel_iommu=on GRUB edit is not needed.
1. Open the node’s Shell and add the three VFIO modules to a file under /etc/modules-load.d/.
cat <<'EOF' > /etc/modules-load.d/vfio.conf
vfio
vfio_iommu_type1
vfio_pci
EOF
2. Update the initramfs, then reboot the host.
update-initramfs -u -k all3. After the reboot, check that the vfio modules are loaded and IOMMU is on, then check the card’s IOMMU group (replace <node> with your node’s name). Each port should sit in its own group, or share one only with the card’s other functions, its root port or a PCIe bridge.
lsmod | grep vfio
dmesg | grep -e DMAR -e IOMMU -e AMD-Vi
pvesh get /nodes/<node>/hardware/pci --pci-class-blacklist ""
Add the NIC Ports to the VM
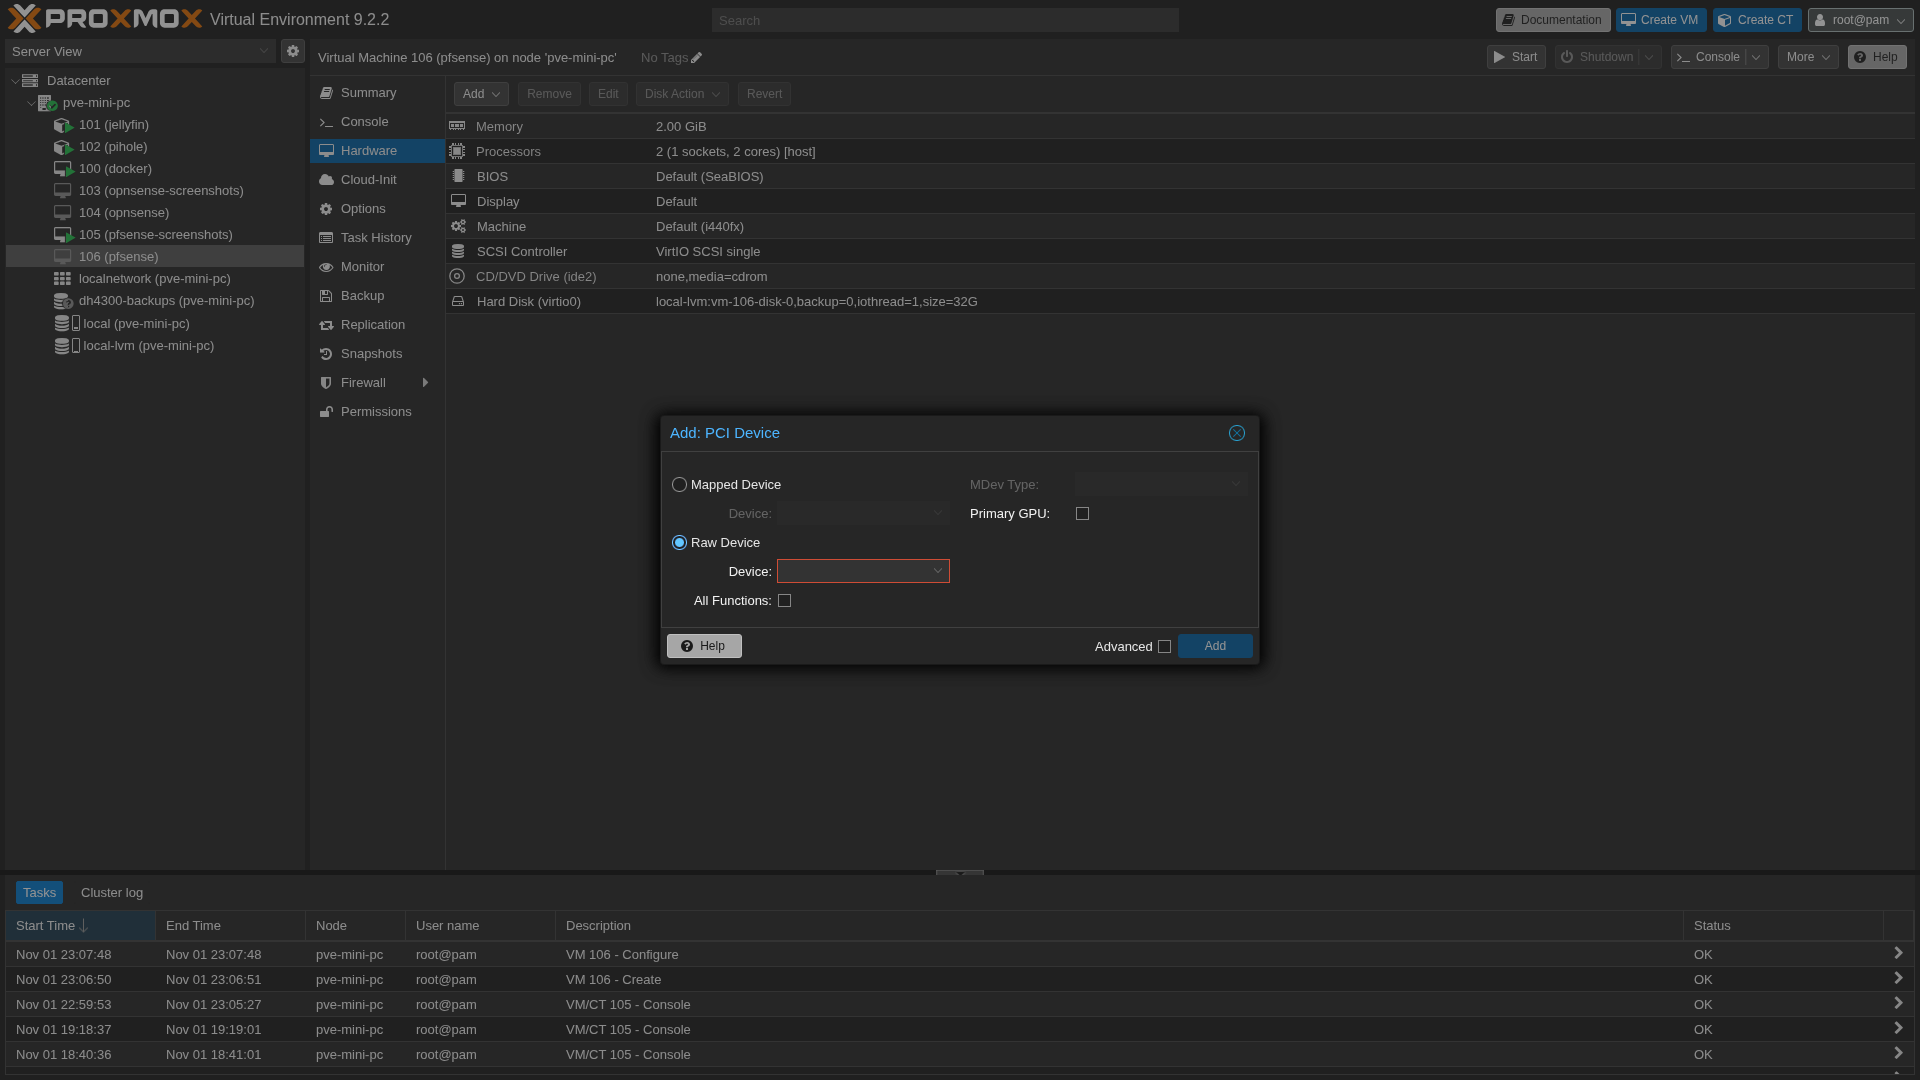
1. Select the pfSense VM, then Hardware, then Add, and finally, PCI Device.
2. In Add: PCI Device, choose Raw Device and pick one port from the Device list. A multi-port card usually lists each port as its own function (0000:03:00.0 and 0000:03:00.1), so add one, repeat for the second, or tick All Functions to pass the whole card, unless one of its ports is vmbr0’s.
Before you start the VM, plug only your modem into the WAN port, because the installer needs that connection. Plug your switch into LAN after the install, when you unplug your current router. Passed-through ports show up in pfSense under the card’s own driver name rather than vtnet.
Option 2: Use Virtual Bridges Without a Spare NIC
Proxmox already created one bridge, vmbr0, on the port you picked when you installed it, and the VM’s first network device sits on it. A router needs a second network for its other side, so you’ll add a second bridge and a second network device.
If the host has a spare physical port, make it vmbr1’s bridge port and cable it to your modem, so vmbr1 is WAN and vmbr0 is LAN. With only one port, leave Bridge ports empty, so vmbr0 is WAN behind your current router and vmbr1 is a test LAN only VMs on this host can join, and you’ll need a VM with a browser to reach the web GUI.
Create a Second Linux Bridge
1. Select your node, then System, then Network, and finally, Create and Linux Bridge.
2. In Create: Linux Bridge, keep the Name it fills in (vmbr1) and leave IPv4/CIDR and Gateway (IPv4) empty. Set Bridge ports to the spare port or leave it empty, tick VLAN aware if you plan to configure VLANs in Proxmox later, then select Create.
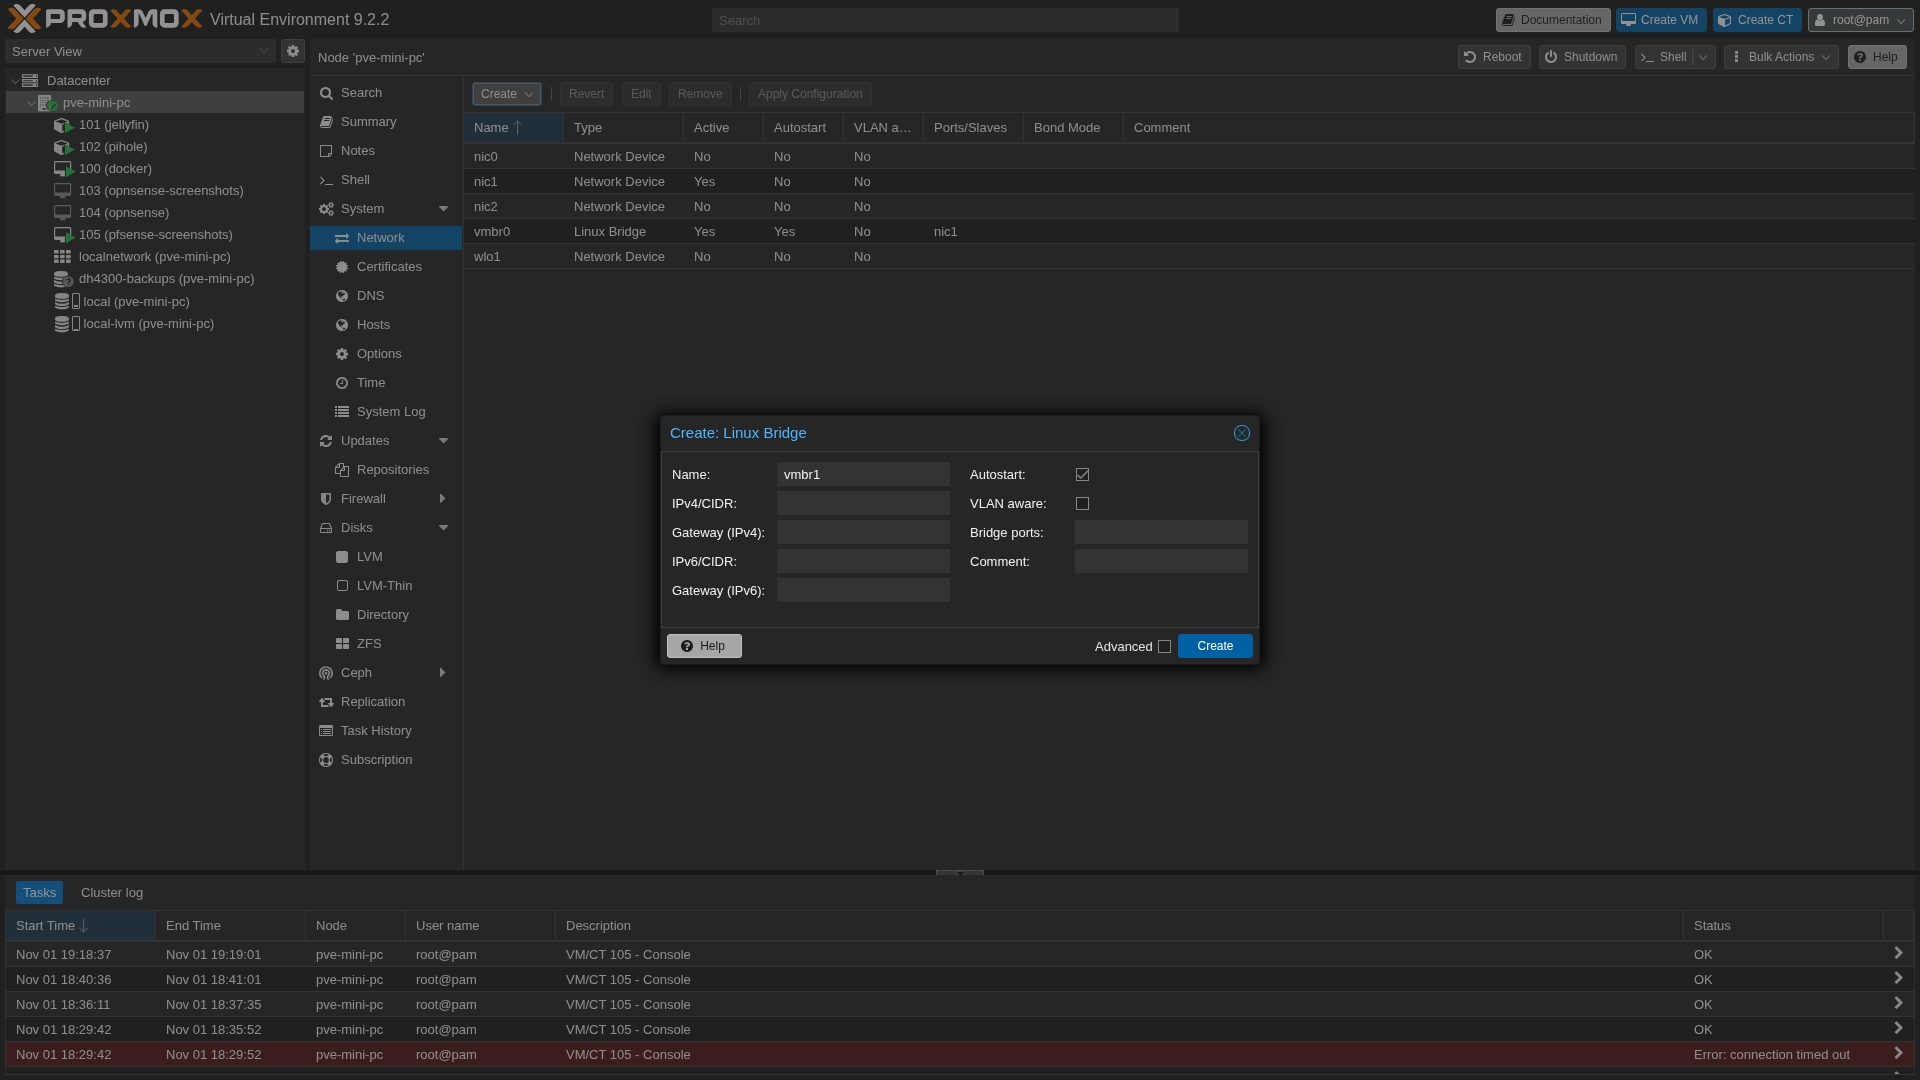
3. Select Apply Configuration and Yes, which applies the change without a reboot (Netgate says to reboot the host if the bridge doesn’t show as active).
Add the Second Network Device
Use VirtIO for both network devices, the model Netgate’s recipe names. Proxmox’s VM docs measured it at up to three times the throughput of an emulated E1000 card.
1. Select the pfSense VM, then Hardware, then Add, and finally, Network Device.
2. Set Bridge to vmbr1 and Model to VirtIO (paravirtualized), then select Add.
With a spare port, your current router still serves vmbr0, pfSense’s LAN, so edit Network Device (net0), tick Advanced and then Disconnect. Untick it when it’s time to swap, so two DHCP servers aren’t fighting over one network.
Run the Netgate Installer
Start the VM and open its Console, and it boots straight into the Netgate Installer. These steps follow Netgate’s install walkthrough. The installer screenshots are from my July 2026 router video, where I ran it on a bare-metal mini PC (CE 2.8.1) rather than Proxmox, so your interface names will differ.
1. Press Enter to accept the license, then choose Install on the welcome menu.
2. Pick the WAN interface. The list shows each interface with its MAC address and link state, so match it to the WAN network device’s MAC on the VM’s Hardware tab (for passthrough, pick the port that reads active). DHCP suits most connections, and static or PPPoE work too, but not other PPP types like L2TP or PPTP.
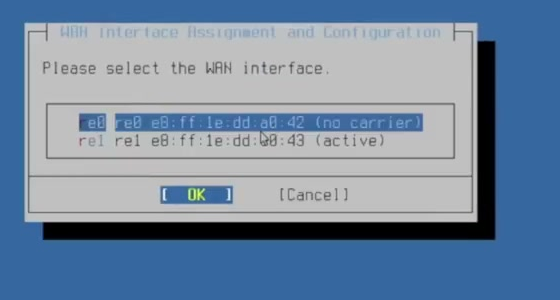
3. Pick the LAN interface the same way. If pfSense replaces your router, give LAN that router’s address and subnet, with the DHCP range inside it, so the Proxmox host stays reachable. Otherwise keep the defaults (192.168.1.1/24, DHCP from 192.168.1.100) unless they clash with yours. Then select Continue.
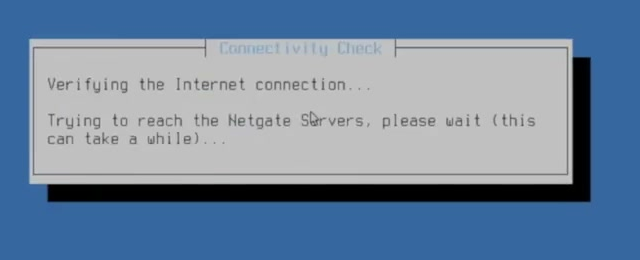
4. The installer checks that it can reach Netgate’s servers. If it says “Cannot verify the eligibility of this system, please try again.”, go back and fix the WAN.
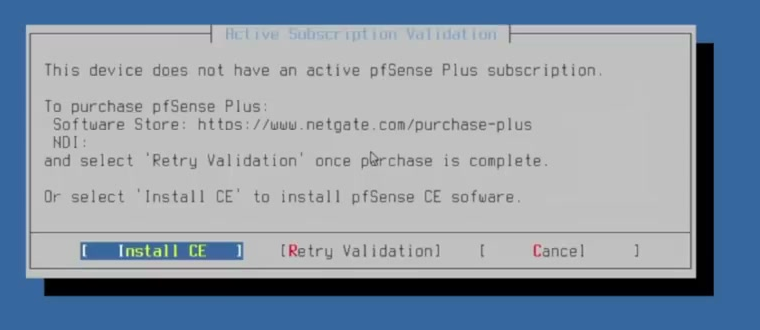
5. On Active Subscription Validation, select Install CE. pfSense Plus needs a paid subscription on hardware that isn’t Netgate’s, which is what this screen checks (here’s how pfSense Plus vs. CE compare).
6. On Installation Options, keep the defaults, ZFS and GPT (I picked ZFS on that mini PC for its data integrity and snapshot support), and choose Continue. For a single virtual disk, keep the stripe pool type and tick the disk with Space, even though it’s the only one listed.
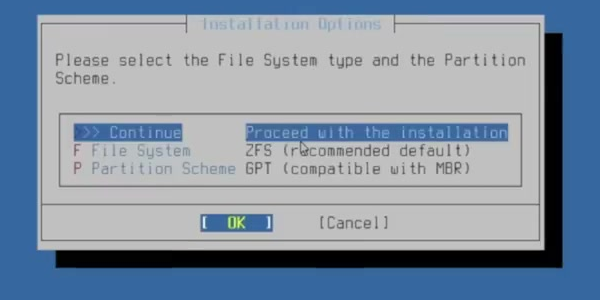
7. Confirm that the disk can be erased, choose the Current Stable Version, and wait while it downloads and installs pfSense.
8. When it finishes, choose to halt, and if Proxmox still shows the VM running, open the Shutdown menu and select Stop.
Eject the ISO and Boot From the Disk
1. Select the VM, then Hardware, select the CD/DVD Drive, and finally, Edit. Choose Do not use any media and select OK.
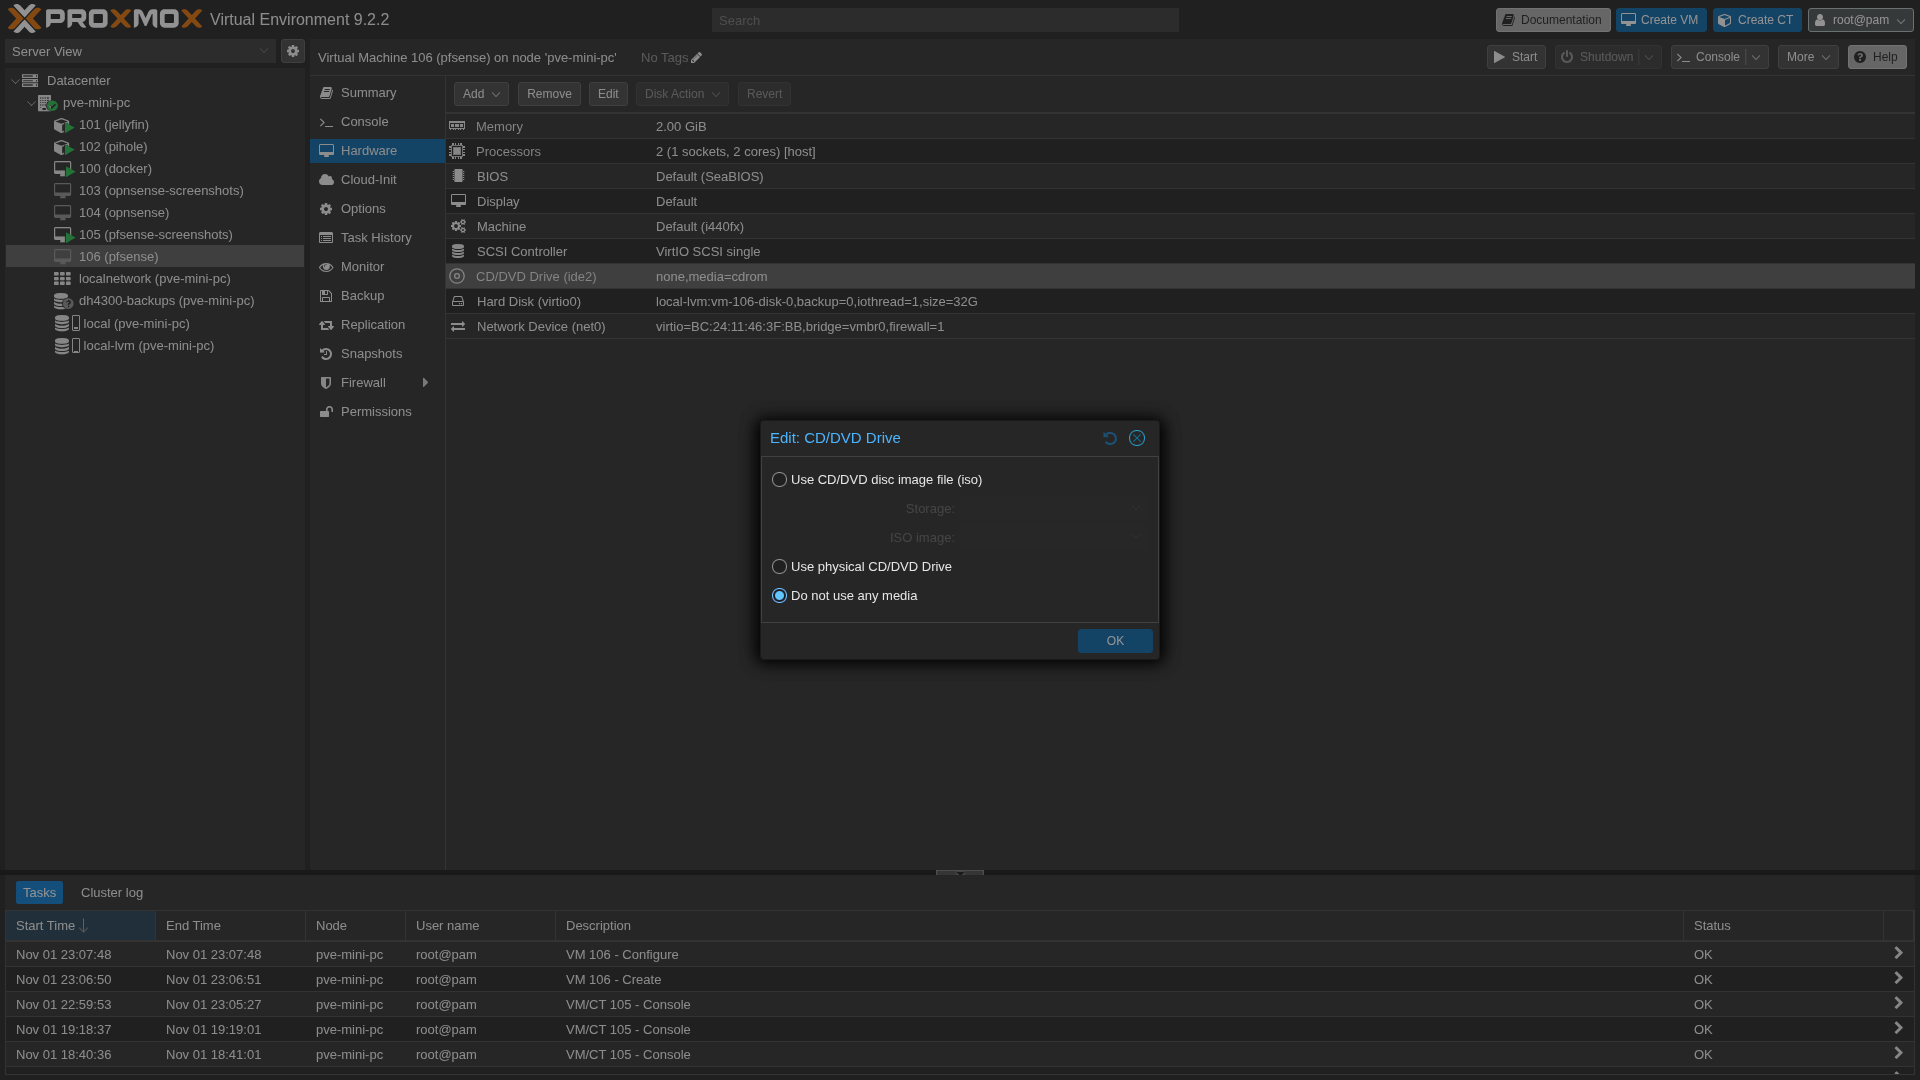
2. Start the VM again, and it boots pfSense from the virtual disk.
Assign Interfaces and Log In to pfSense
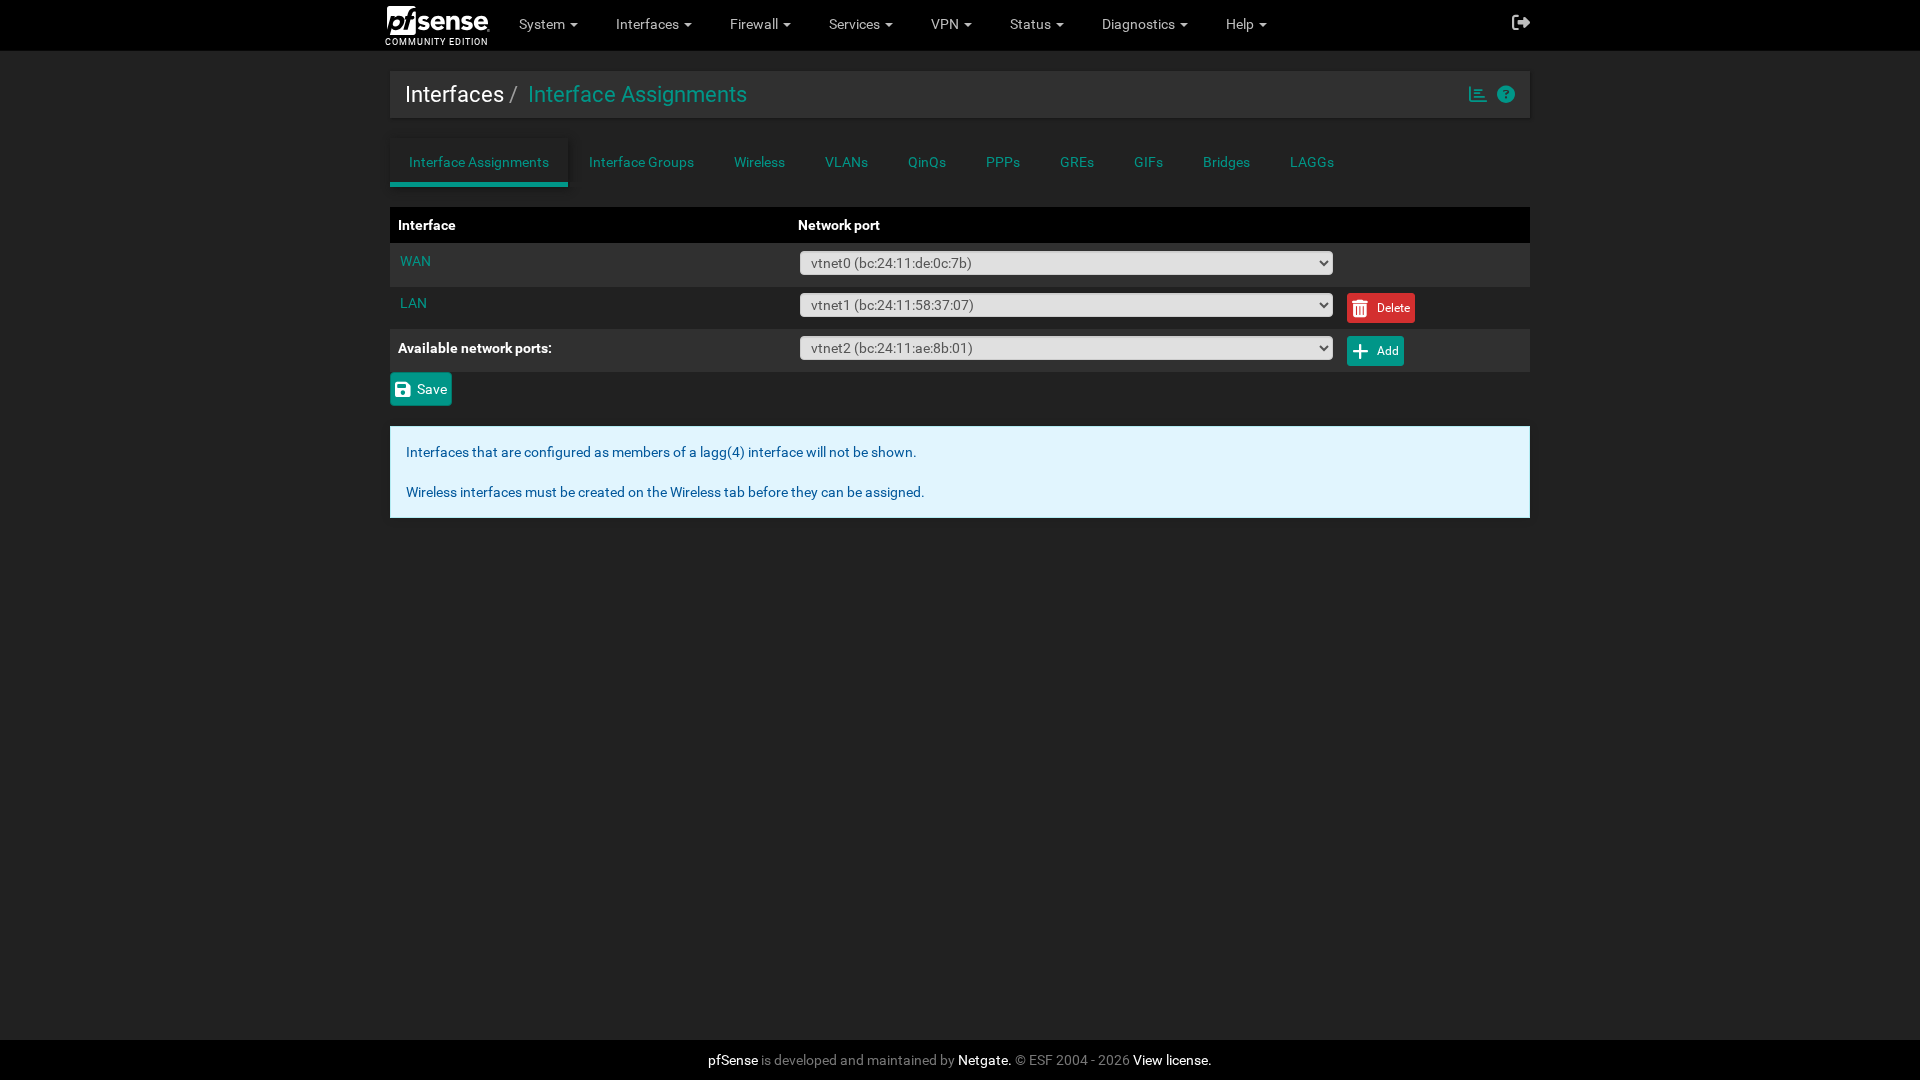
The installer copies the WAN and LAN you picked to the installed system, so the console menu lists both, with VirtIO devices named vtnet0, vtnet1 and so on in the order of Proxmox’s net0 and net1.
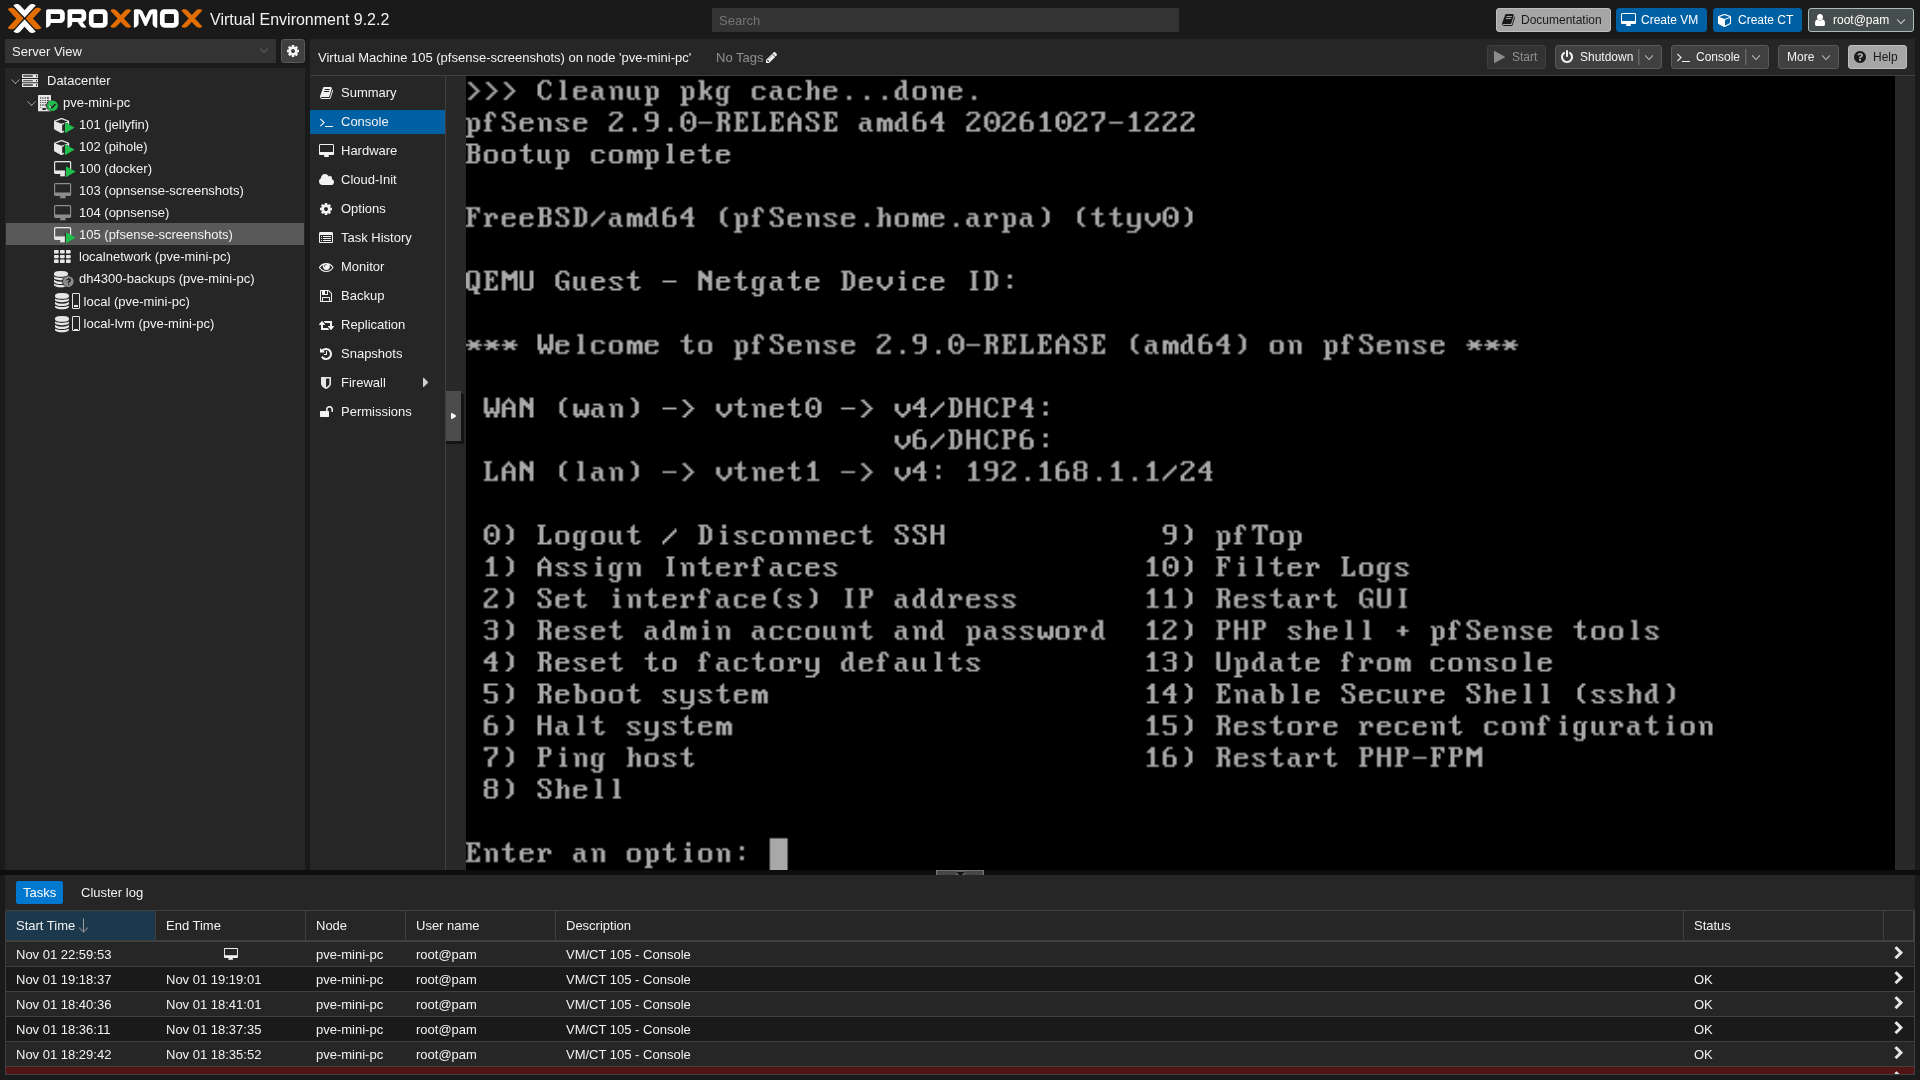
1. If prompted to assign interfaces, answer n to VLANs, type the WAN interface (vtnet0 on a one-port host, vtnet1 if the spare port is WAN), then the LAN one, press Enter if it asks for an optional one, and answer y.
2. To change the LAN address from the console, choose 2) Set interface(s) IP address and pick LAN. Answer n to DHCP and DHCP6, enter the address and 24, press Enter to skip the gateway and IPv6 address, and answer y to the DHCP server to set a range. When it asks about reverting the web GUI to HTTP, answer n to keep HTTPS.
3. From a computer on the LAN side (a VM on vmbr1 on a one-port host, or on vmbr0 once your old router is off it and Disconnect is unticked), open the LAN address (https://192.168.1.1 by default), accept the certificate warning, and log in as admin with the password pfsense.
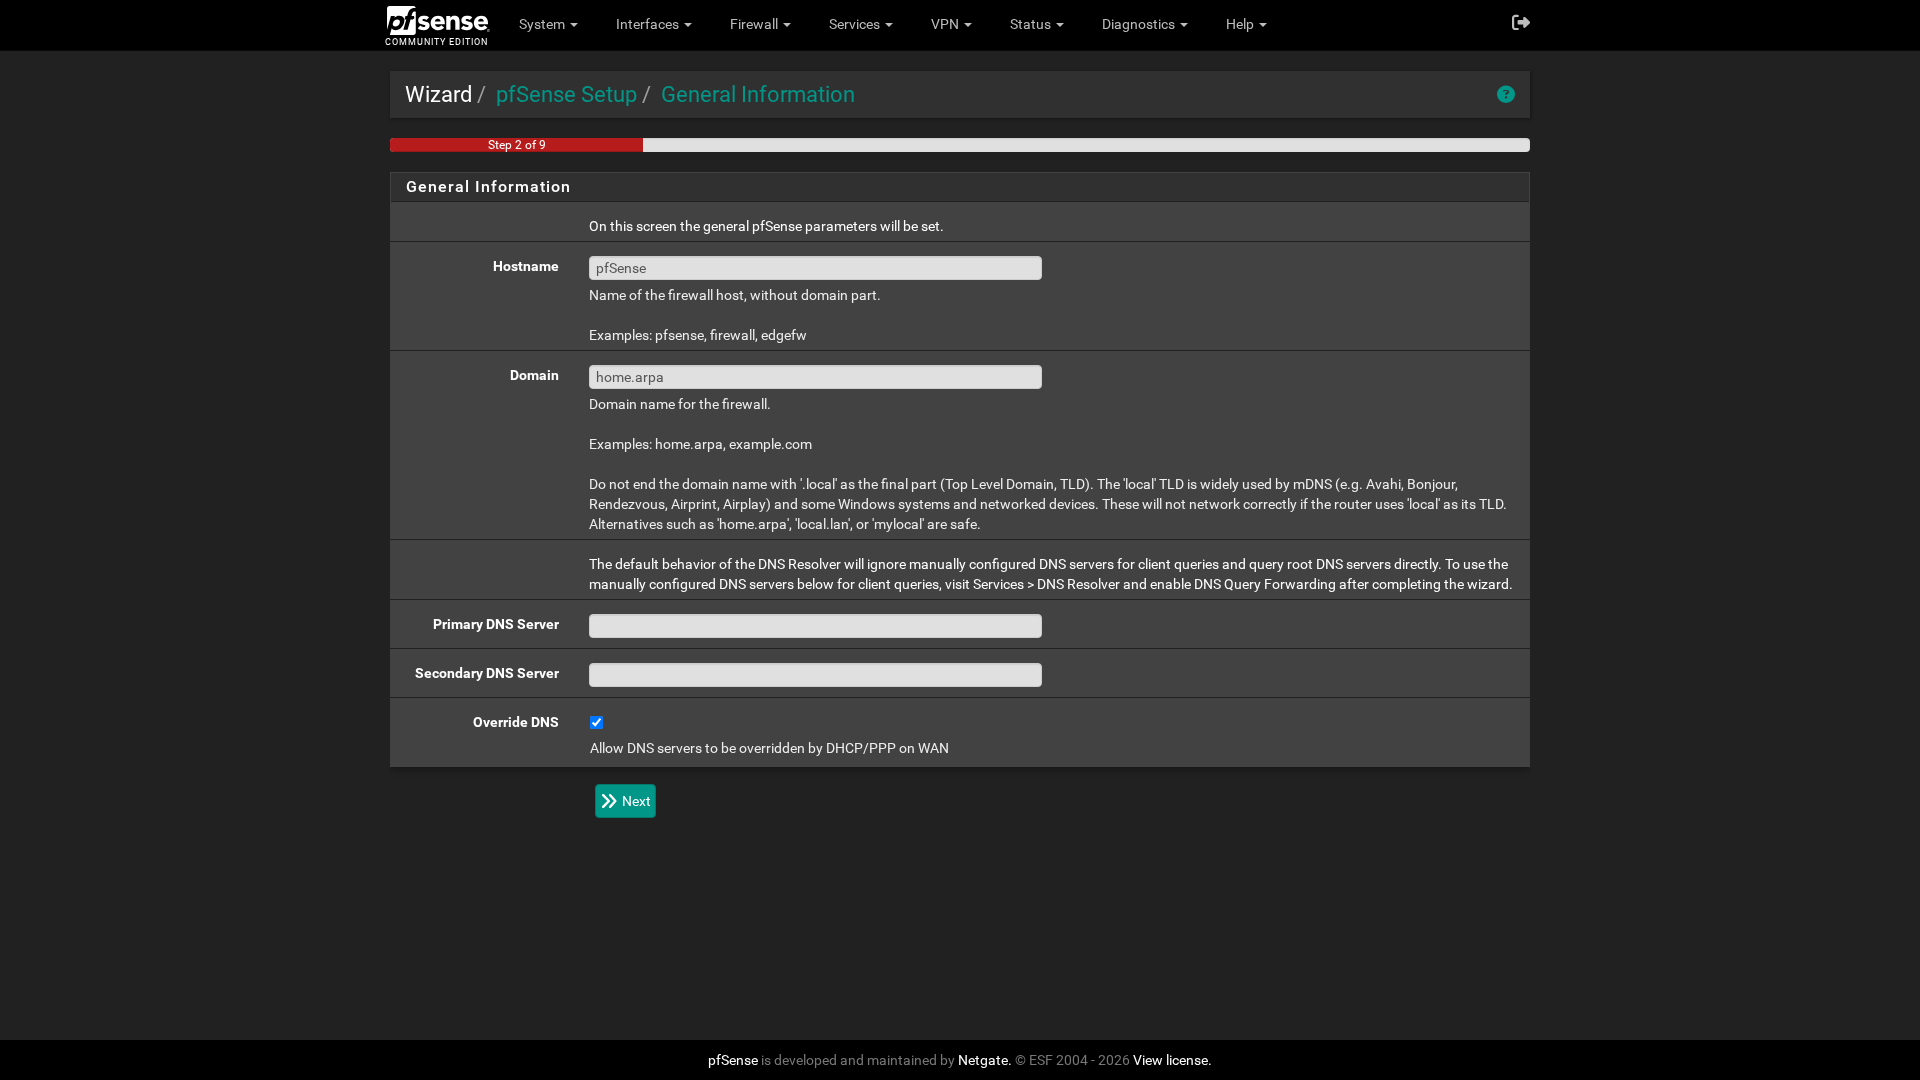
4. The setup wizard opens. Select Next until General Information, then set the Hostname and Domain. The DNS servers can stay empty.
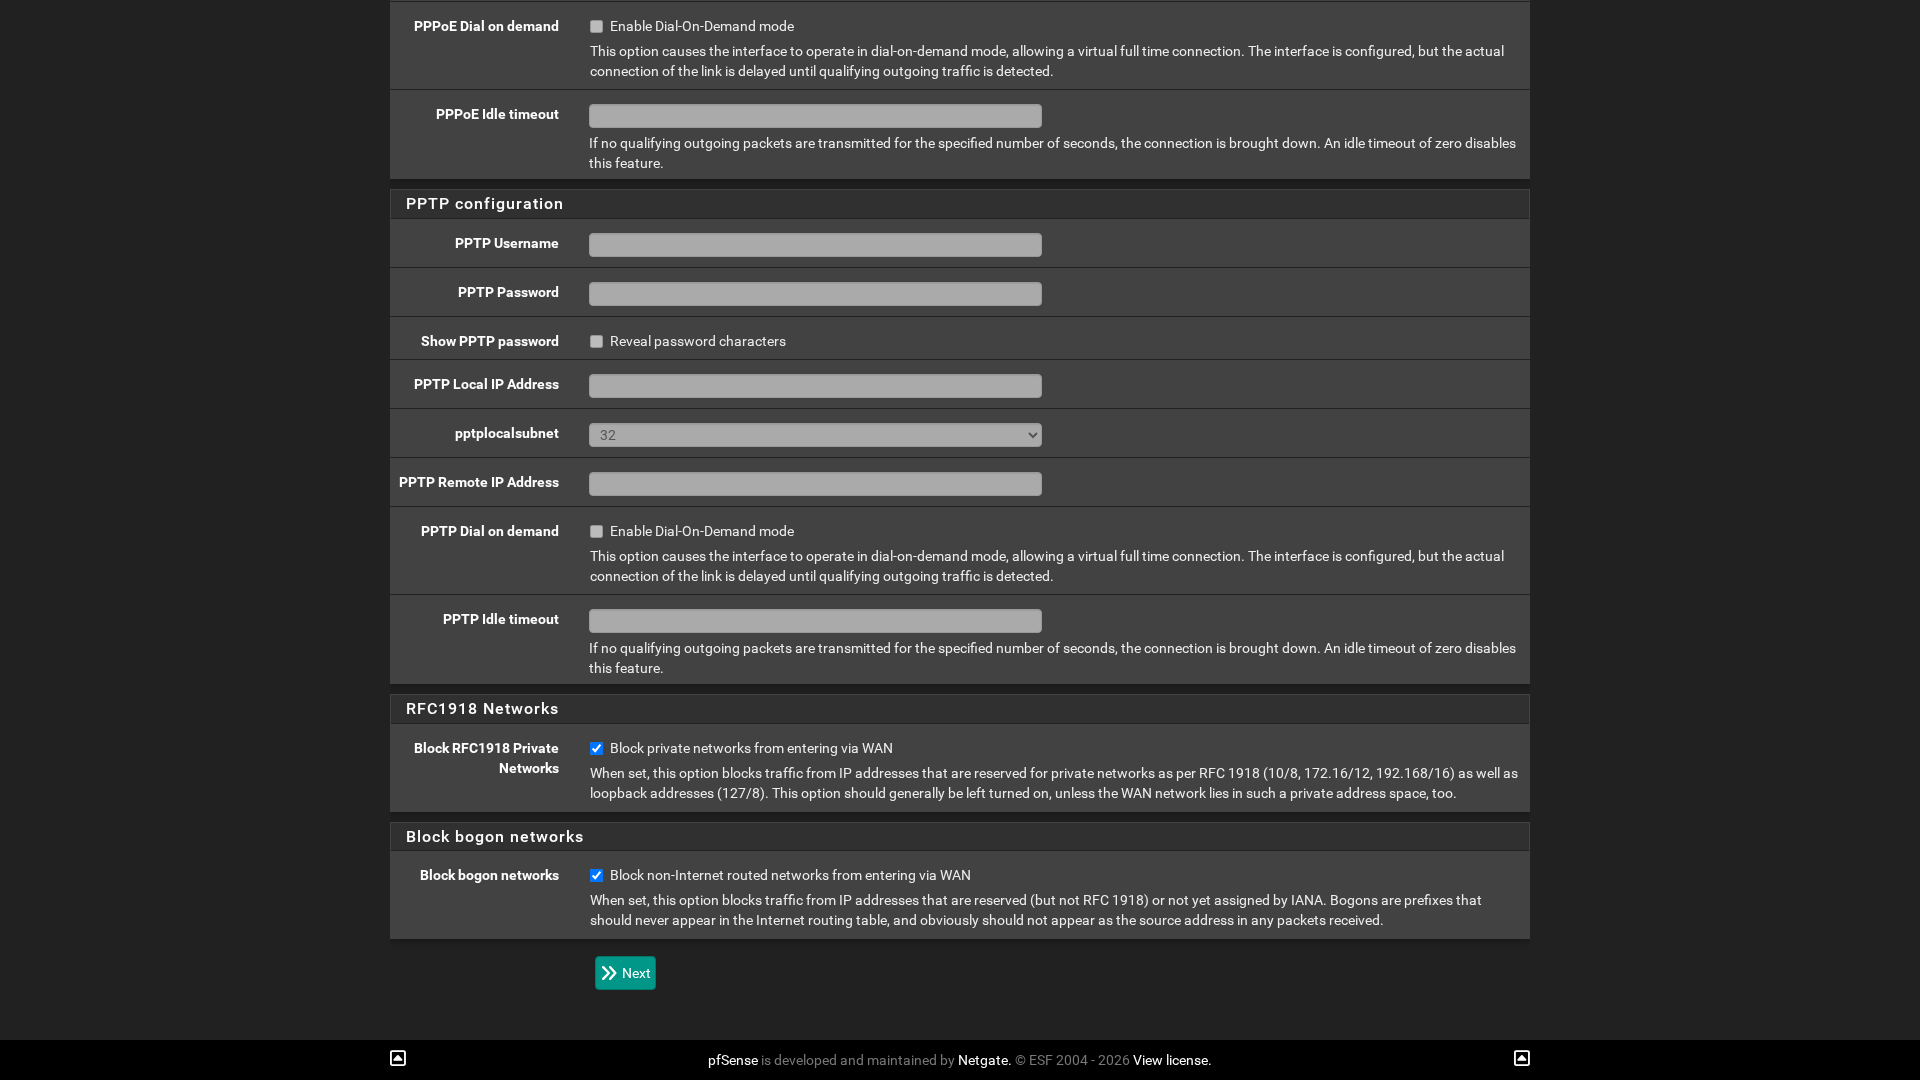
5. Keep the default time server, pick your time zone, then keep the WAN on DHCP unless your ISP needs PPPoE. Leave Block RFC1918 Private Networks ticked when WAN plugs into your modem, and untick it when WAN gets a private address from your current router, as its help text says.
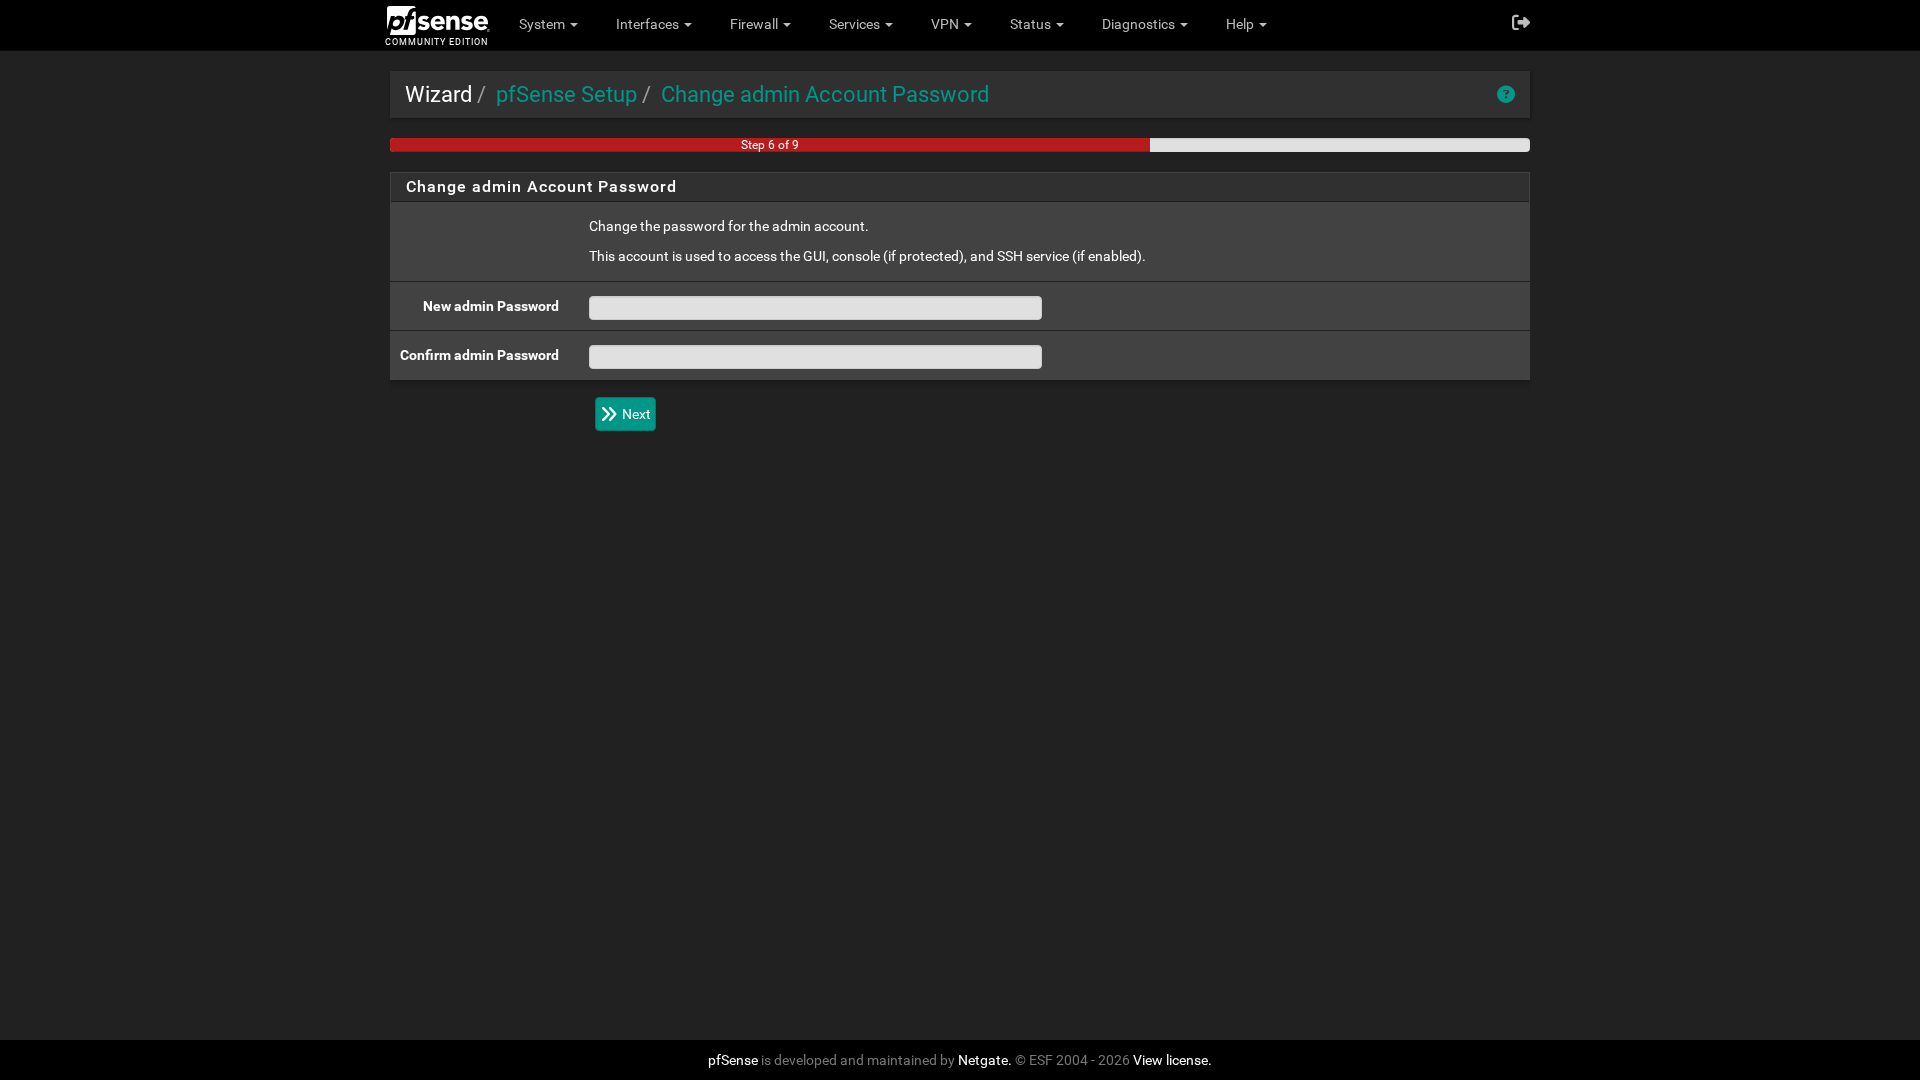
6. Keep the LAN address, then on Change admin Account Password, type a replacement for pfsense in New admin Password and Confirm admin Password and select Next and Reload, log back in with the new password if asked, and select Finish.
Once it reloads, Interfaces > Interface Assignments confirms which network device landed on WAN and which on LAN.
Disable Hardware Checksum Offload for VirtIO
Netgate’s recipe says that with VirtIO interfaces in Proxmox, “network interface hardware checksum offloading must be disabled.” pfSense tries to turn it off for vtnet interfaces on its own, but Netgate says to double-check. On a VM upgraded to CE 2.9.0 and checked in November 2026, the box was unticked, so you’ll likely tick it yourself.
1. Select System, then Advanced, and finally, the Networking tab.
2. In the Network Interfaces section, tick Disable hardware checksum offload. Leave the other boxes as they are (the lab VM in the screenshot also has Virtual NIC ALTQ support ticked, which this fix doesn’t need).
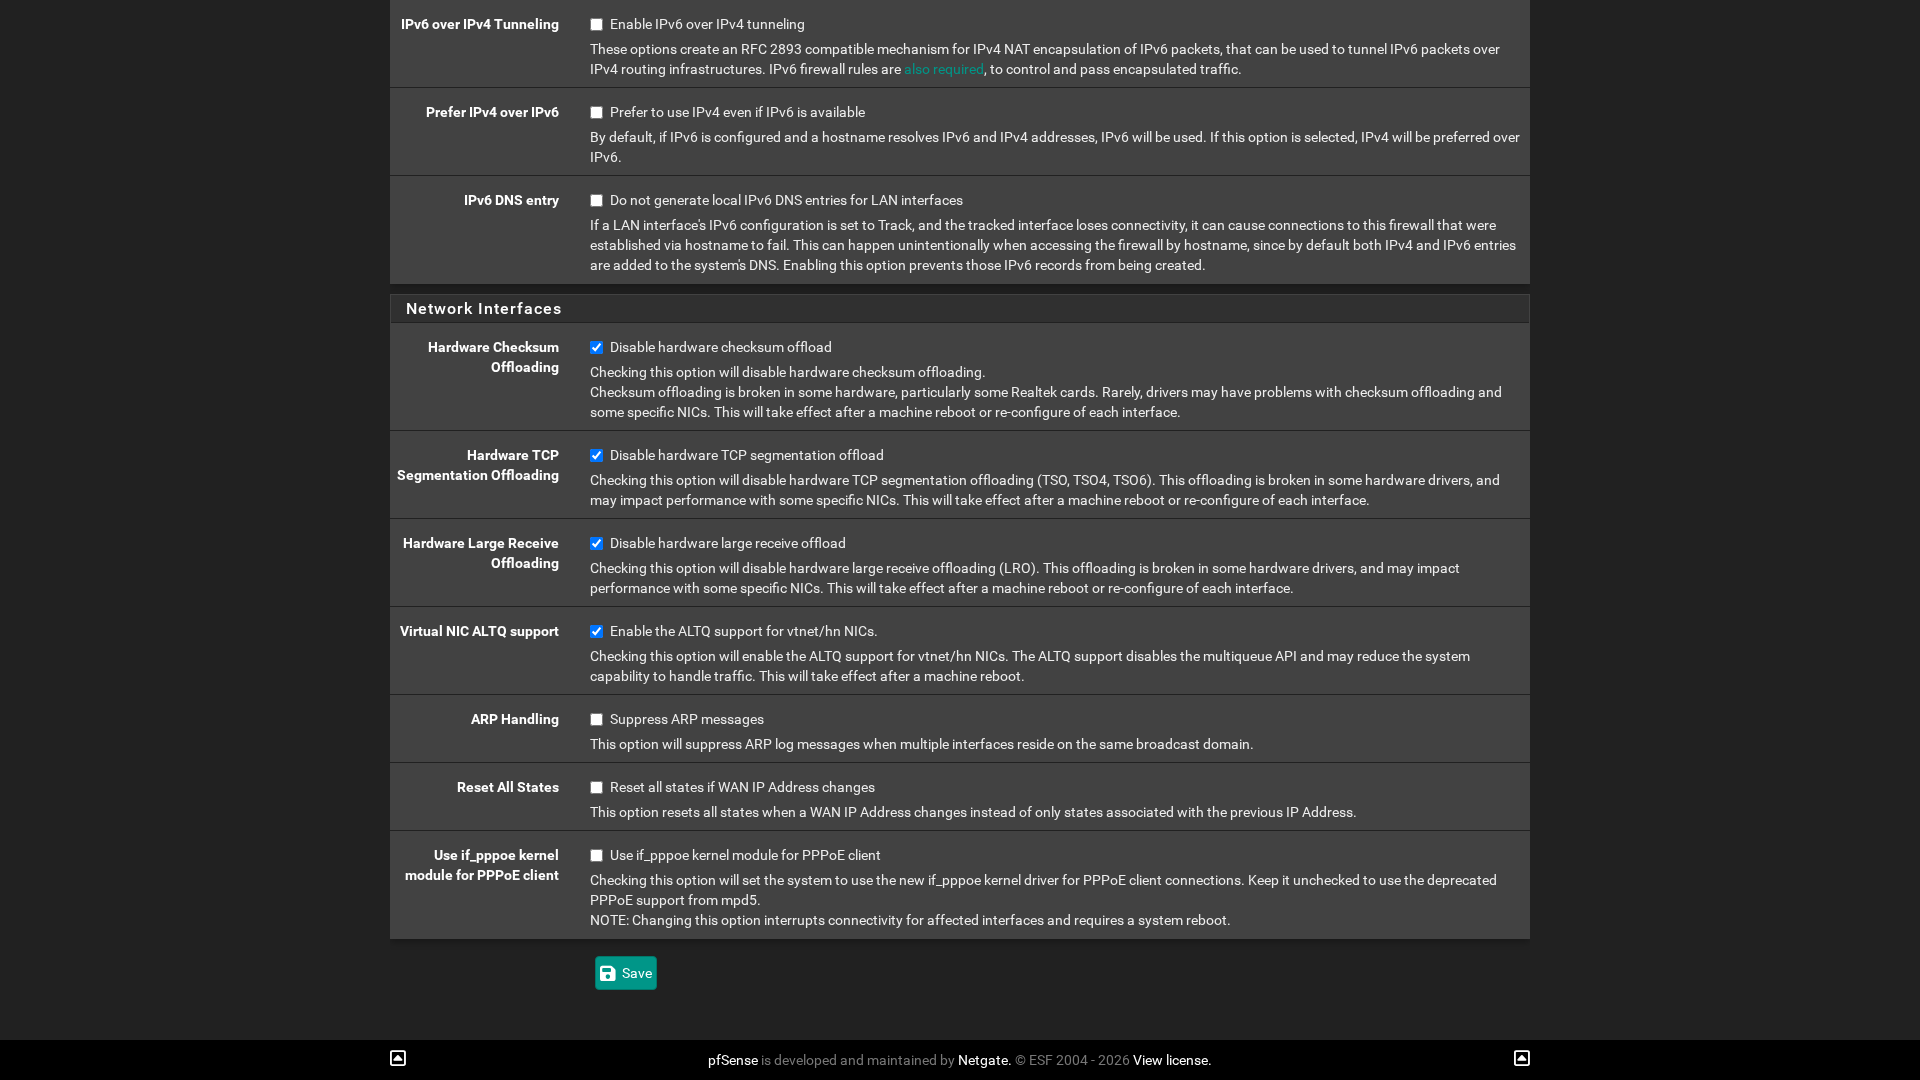
3. Select Save at the bottom of the page, then reboot pfSense from Diagnostics > Reboot or the console menu.
Netgate’s warning is blunt: skip this and the VM “will not properly pass traffic.” pfSense’s help text says checksum offloading is also broken on some hardware, particularly some Realtek cards, so tick it on a passed-through card like that too.
Snapshot pfSense in Proxmox Before Every Update
Running pfSense in Proxmox has one big advantage over a separate box, and it’s the rollback plan. Select Take Snapshot on the VM’s Snapshots tab (untick Include RAM if you passed a card through) or one of your backups right before upgrades, run the update from System > Update in pfSense, and use Rollback or restore the backup if something breaks.
From there, the rest of the pfSense Proxmox setup is regular pfSense work:
- Configure port forwarding and separate traffic with VLANs or a DMZ.
- Set up a VPN with WireGuard, OpenVPN or Tailscale.
- Configure firewall rules and access pfSense over SSH.
- Set up DDNS with DuckDNS or Cloudflare if your public IP changes.
If you decide the firewall belongs on its own box after all, you can run pfSense on dedicated hardware or purchase hardware from Netgate. Firewall software and its defaults change between releases, and nothing here is a guarantee that your network is secure.