pfSense multi WAN comes down to one gateway group. Put your main connection on Tier 1 and the second on Tier 2, set that failover group as the default gateway, point the LAN rule at it (or at a second group with both on Tier 1 to load balance), and give each WAN its own DNS server. Every screen and label below is from pfSense CE 2.9.0, as of November 2026.
I ran pfSense as my router for a few years before moving to UniFi in late 2024, and when I had two ISP connections back then, I kept the second one as an isolated test network. So this follows Netgate’s documentation, not a setup of mine. Two things decide whether failover works: a group on the default gateway must be a failover group, and DNS takes everything down if only one WAN can reach it.
pfSense Multi-WAN: Failover or Load Balancing
Both modes use a gateway group, and the only difference is the tier each gateway sits on. Gateways on different tiers fail over, so Tier 2 is only used when every Tier 1 gateway is down. Gateways on the same tier load balance per connection, round-robin, and because a failed gateway drops out of the pool, they fail over too. There are up to five tiers, so a pfSense multiple WAN setup with three lines works the same way.
Load balancing is not one faster pipe, since a single download still runs over one WAN, so for most people with a main line and a backup, failover is the right choice. In January 2025, my UDM Pro Max with two ISPs was just doing basic failover. Netgate’s page on load balancing and failover calls setting a failover group as the default gateway best practice either way.
Add WAN2 for a pfSense Dual WAN Setup
Plug the second modem or ONT into a free firewall port, then add it as an interface.
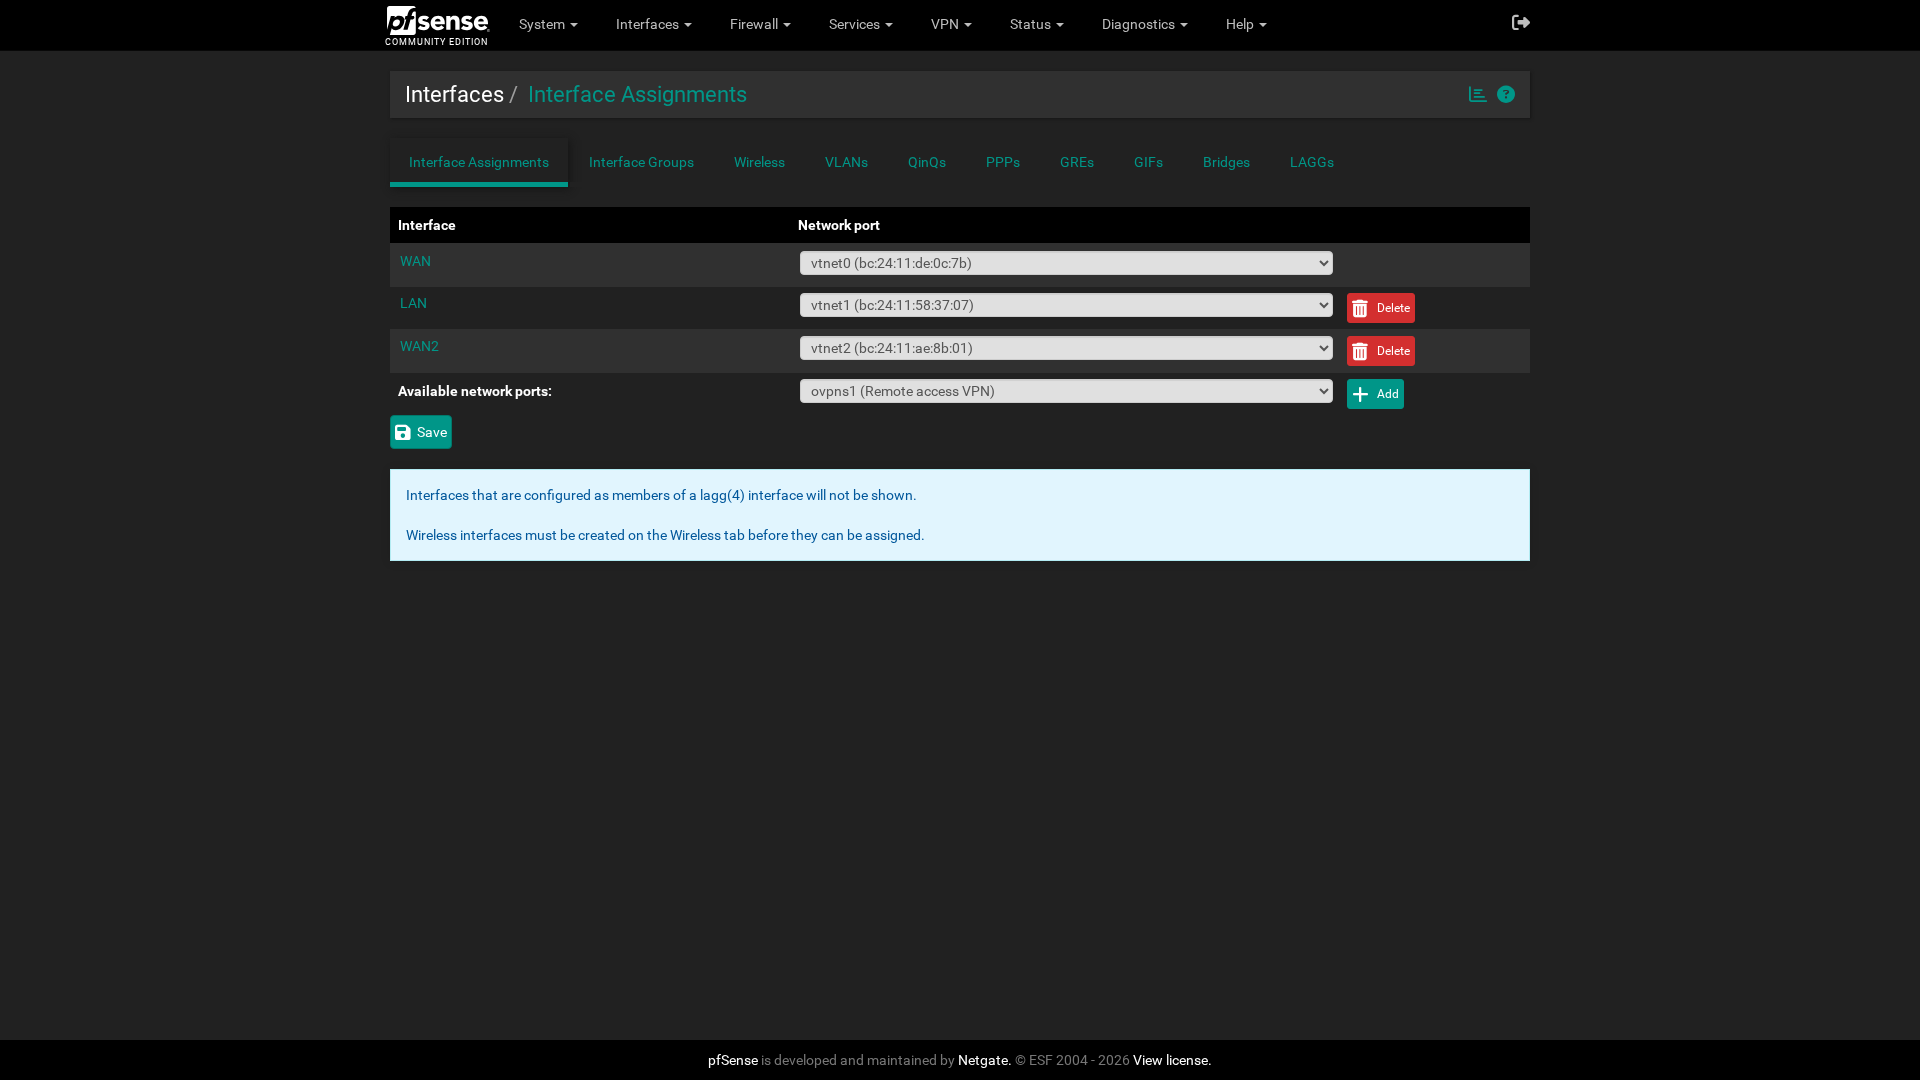
1. Open Interfaces, then Assignments, select the new port under Available network ports, and select Add. pfSense names it OPT1 (or the next free OPTx).
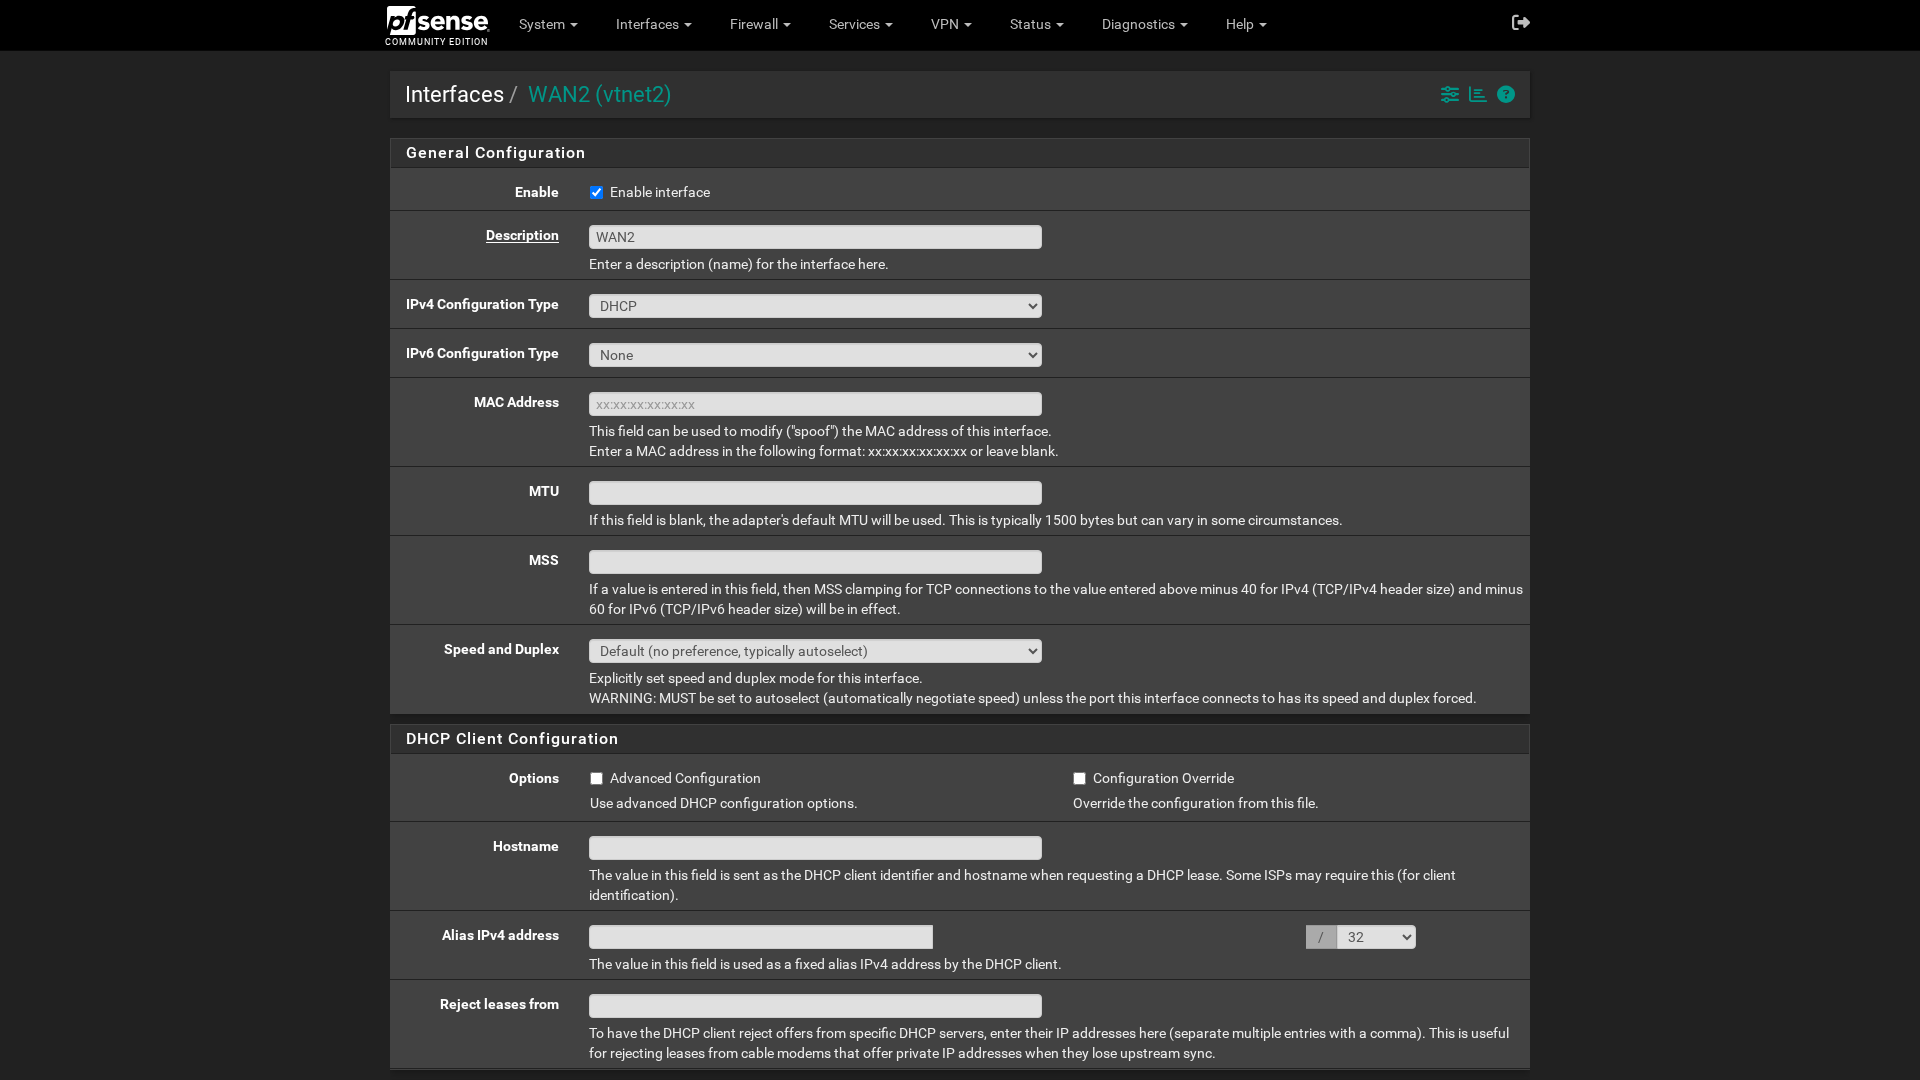
2. Select the new interface, tick Enable interface, set the Description to WAN2, and set IPv4 Configuration Type to what the ISP uses (DHCP for most; PPPoE needs the ISP’s login, and Static IPv4 an address and an IPv4 Upstream gateway). Under Reserved Networks, tick Block private networks and loopback addresses unless WAN2 sits behind another router.
3. Select Save, then Apply Changes. WAN2 now has its port on Interfaces > Assignments.
With DHCP, pfSense creates a gateway called WAN2_DHCP. On PPPoE or static, use your gateway’s name wherever this guide says WAN2_DHCP.
pfSense steers multi-WAN traffic by each circuit’s gateway IP, so if both connections share a subnet and gateway (common with two cable modems from one ISP), Netgate says all but one need an intermediate NAT device.
Set a Monitor IP for Each Gateway
pfSense decides a WAN is down by pinging its monitor IP, which defaults to the gateway. That’s often your own modem, which still answers when the ISP is down. Point each gateway at something upstream, like a public DNS server you don’t bind to another WAN under DNS (pfSense routes each monitor IP out its own gateway), and give every gateway a unique address.
1. Open System, then Routing, and on the Gateways tab, select the pencil next to WAN_DHCP.
2. Enter an upstream address in Monitor IP (1.1.1.1 here), then select Save.
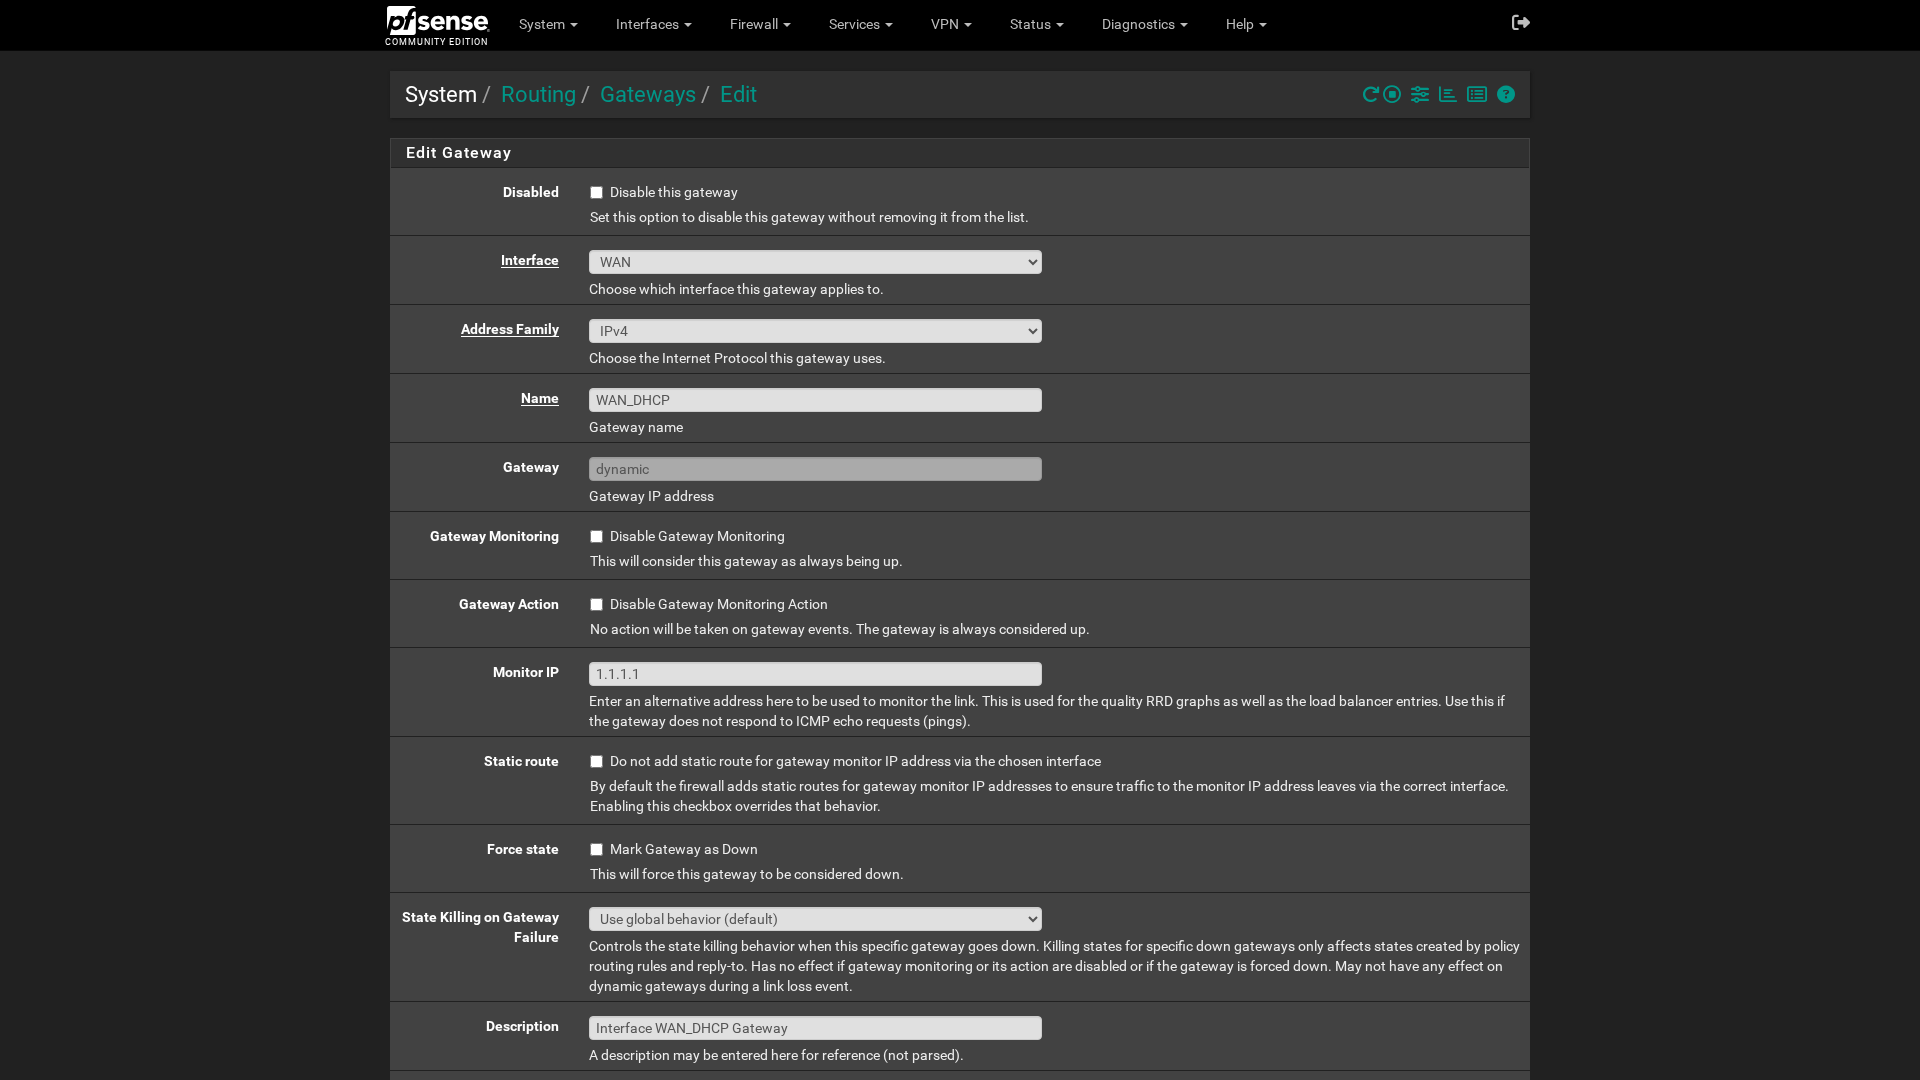
3. Repeat for WAN2_DHCP with a different address (8.8.4.4 here), then select Apply Changes.
pfSense won’t save a monitor IP another gateway already uses, and the latency and loss thresholds sit under Display Advanced on the Edit Gateway page.
Create the Dual WAN Failover Gateway Group
pfSense dual WAN failover needs one gateway group with each WAN on its own tier.
1. Open System, then Routing, select the Gateway Groups tab, and select Add.
2. Enter a Group Name such as WAN_Failover.
3. Under Gateway Priority, set WAN_DHCP to Tier 1 and WAN2_DHCP to Tier 2, and leave Virtual IP at Interface Address.
4. Choose a Trigger Level. Member Down fails over only when a gateway is completely down, while Packet Loss, High Latency and Packet Loss or High Latency also act once a line crosses the lower alert threshold.
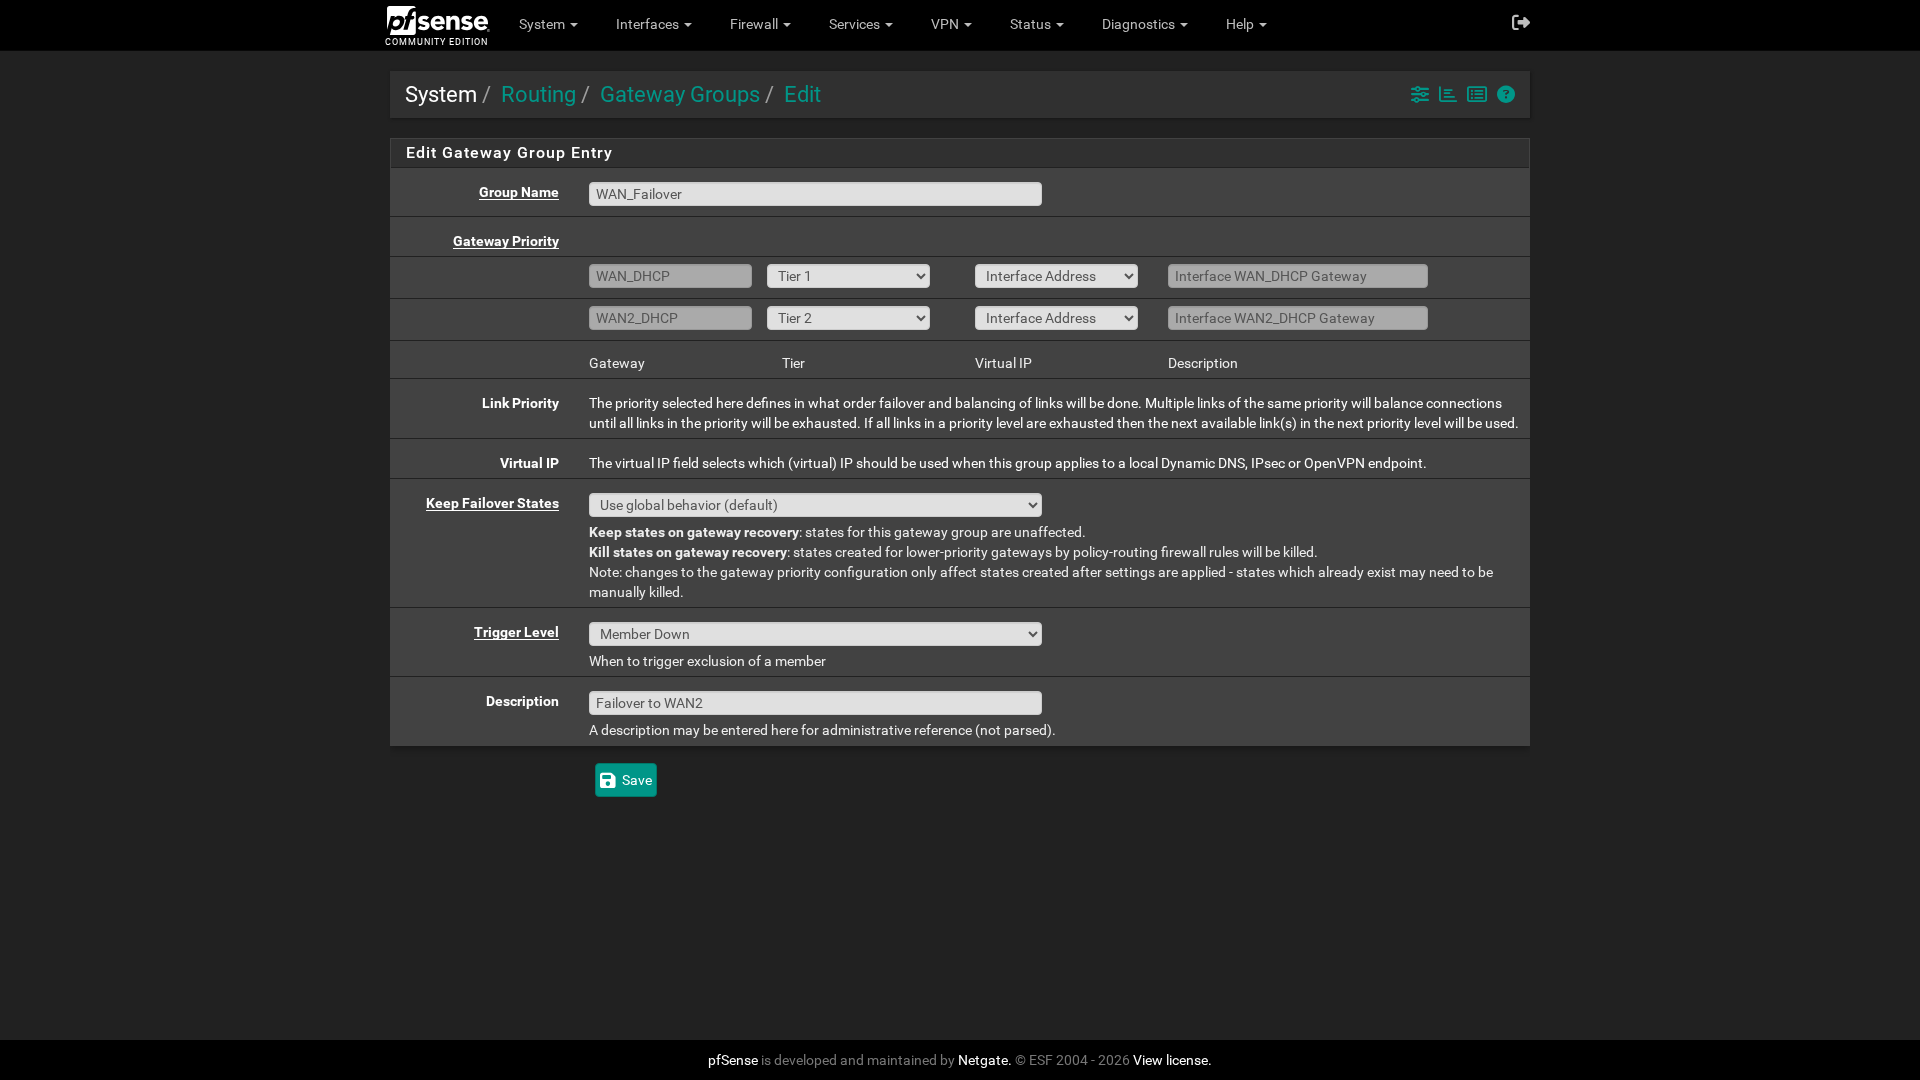
5. Leave Keep Failover States on Use global behavior (by default, LAN connections opened on WAN2 are killed when WAN recovers, so they reconnect on WAN), add a Description, select Save, then Apply Changes.
Set the Default Gateway to the Failover Group
Netgate’s default gateway documentation says a group there only works for failover, so the group must have one gateway per tier. The drop-down lists every group, but the CE 2.9.0 help text is the hint: “Select a gateway or failover gateway group to use as the default gateway.”
1. On System > Routing > Gateways, set Default gateway IPv4 to WAN_Failover.
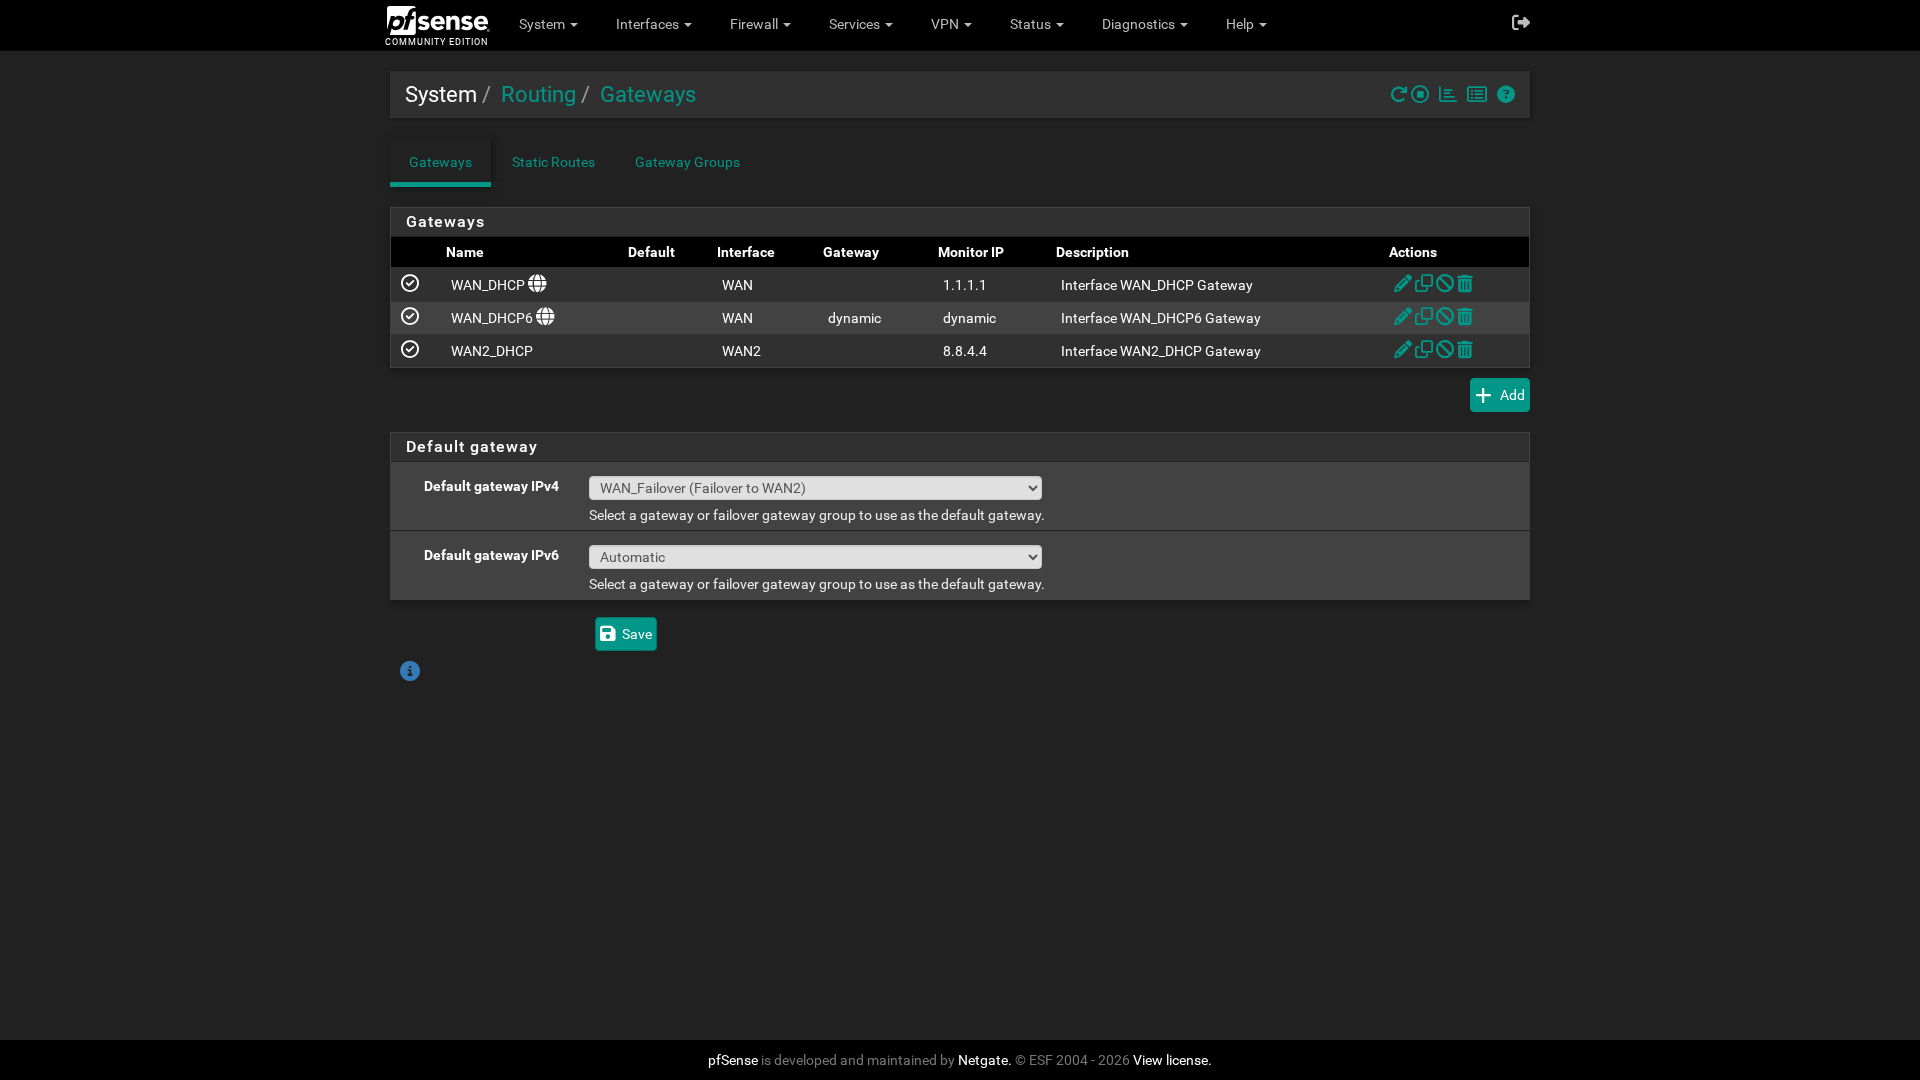
2. Select Save, then Apply Changes.
The default gateway carries the firewall’s own traffic, DNS lookups included, plus anything that doesn’t match a policy-routing rule.
Send LAN Traffic Through the Gateway Group
Setting the group on the LAN pass rule (policy routing) lets pfSense track which WAN each connection used, so it can kill those states when a gateway fails.
Rules match top-down, so traffic to other local networks, VLANs or WireGuard needs a pass rule above this one (Netgate suggests an alias of the private ranges). My guide to creating firewall rules in pfSense covers that screen.
1. Open Firewall, then Rules, select the LAN tab, and edit the Default allow LAN to any rule.
2. Under Extra Options, select Display Advanced, then set Gateway to WAN_Failover.
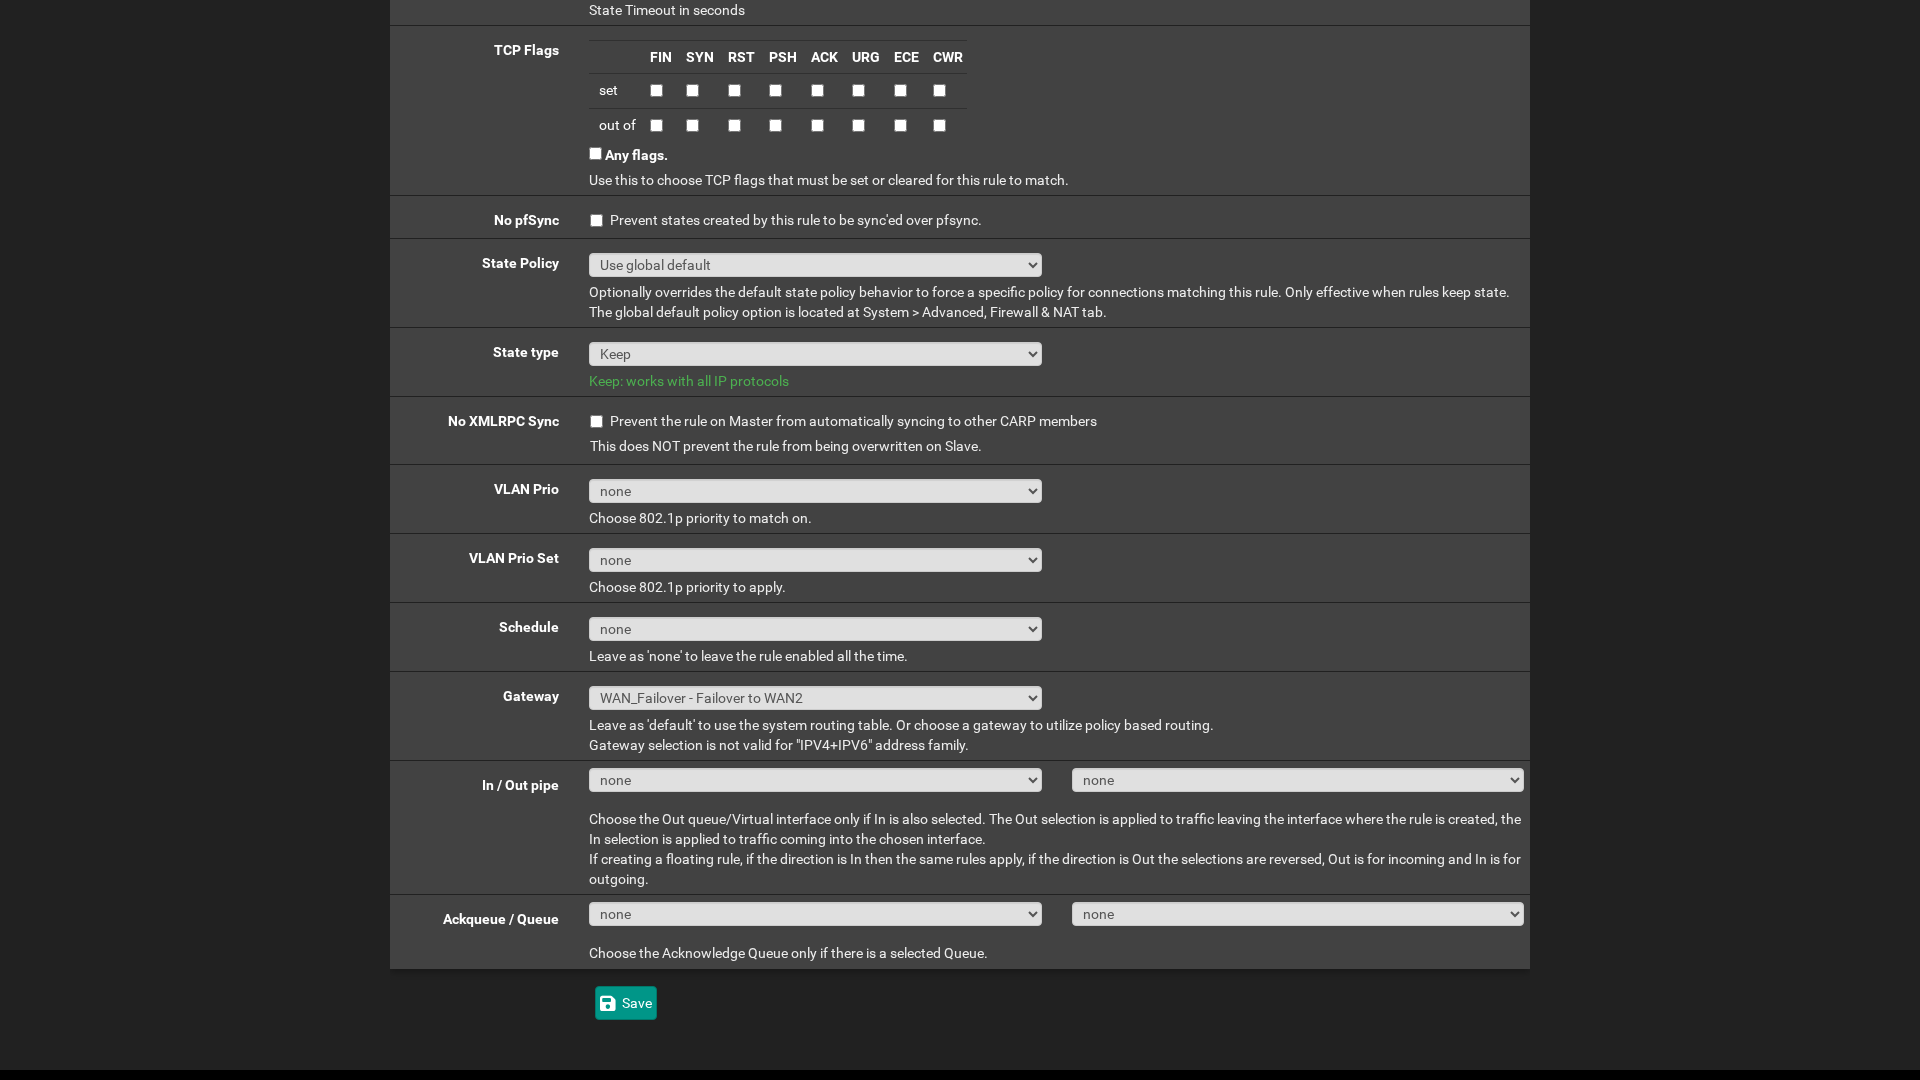
3. Select Save, then Apply Changes.
CE 2.9.0 ships separate IPv4 and IPv6 default LAN rules, so the IPv4 rule takes the group (IPv6 failover needs its own IPv6 group). On a rule with Address Family set to IPv4+IPv6, the Gateway field is greyed out, so split that rule in two.
CE 2.8.0 changed the default State Policy to Interface Bound States, which Netgate says may cause issues with multi-WAN policy routing in some cases. If WAN2 traffic fails, set Firewall State Policy under System > Advanced > Firewall & NAT to Floating States, which pfSense calls less secure, then Save.
Give Each WAN Its Own DNS Server
If DNS only works through one WAN, losing that WAN takes everything down. The DNS Resolver’s default resolver mode (which keeps DNSSEC) needs the failover default gateway you’ve set, and pfSense falls back to the servers below. Forwarding mode reaches the servers in General Setup through the routing table, so each WAN needs its own server bound to it.
1. Open System, then General Setup, and add one DNS server per WAN with its Gateway set (for example 1.0.0.1 on WAN_DHCP and 8.8.8.8 on WAN2_DHCP), with Add DNS Server.
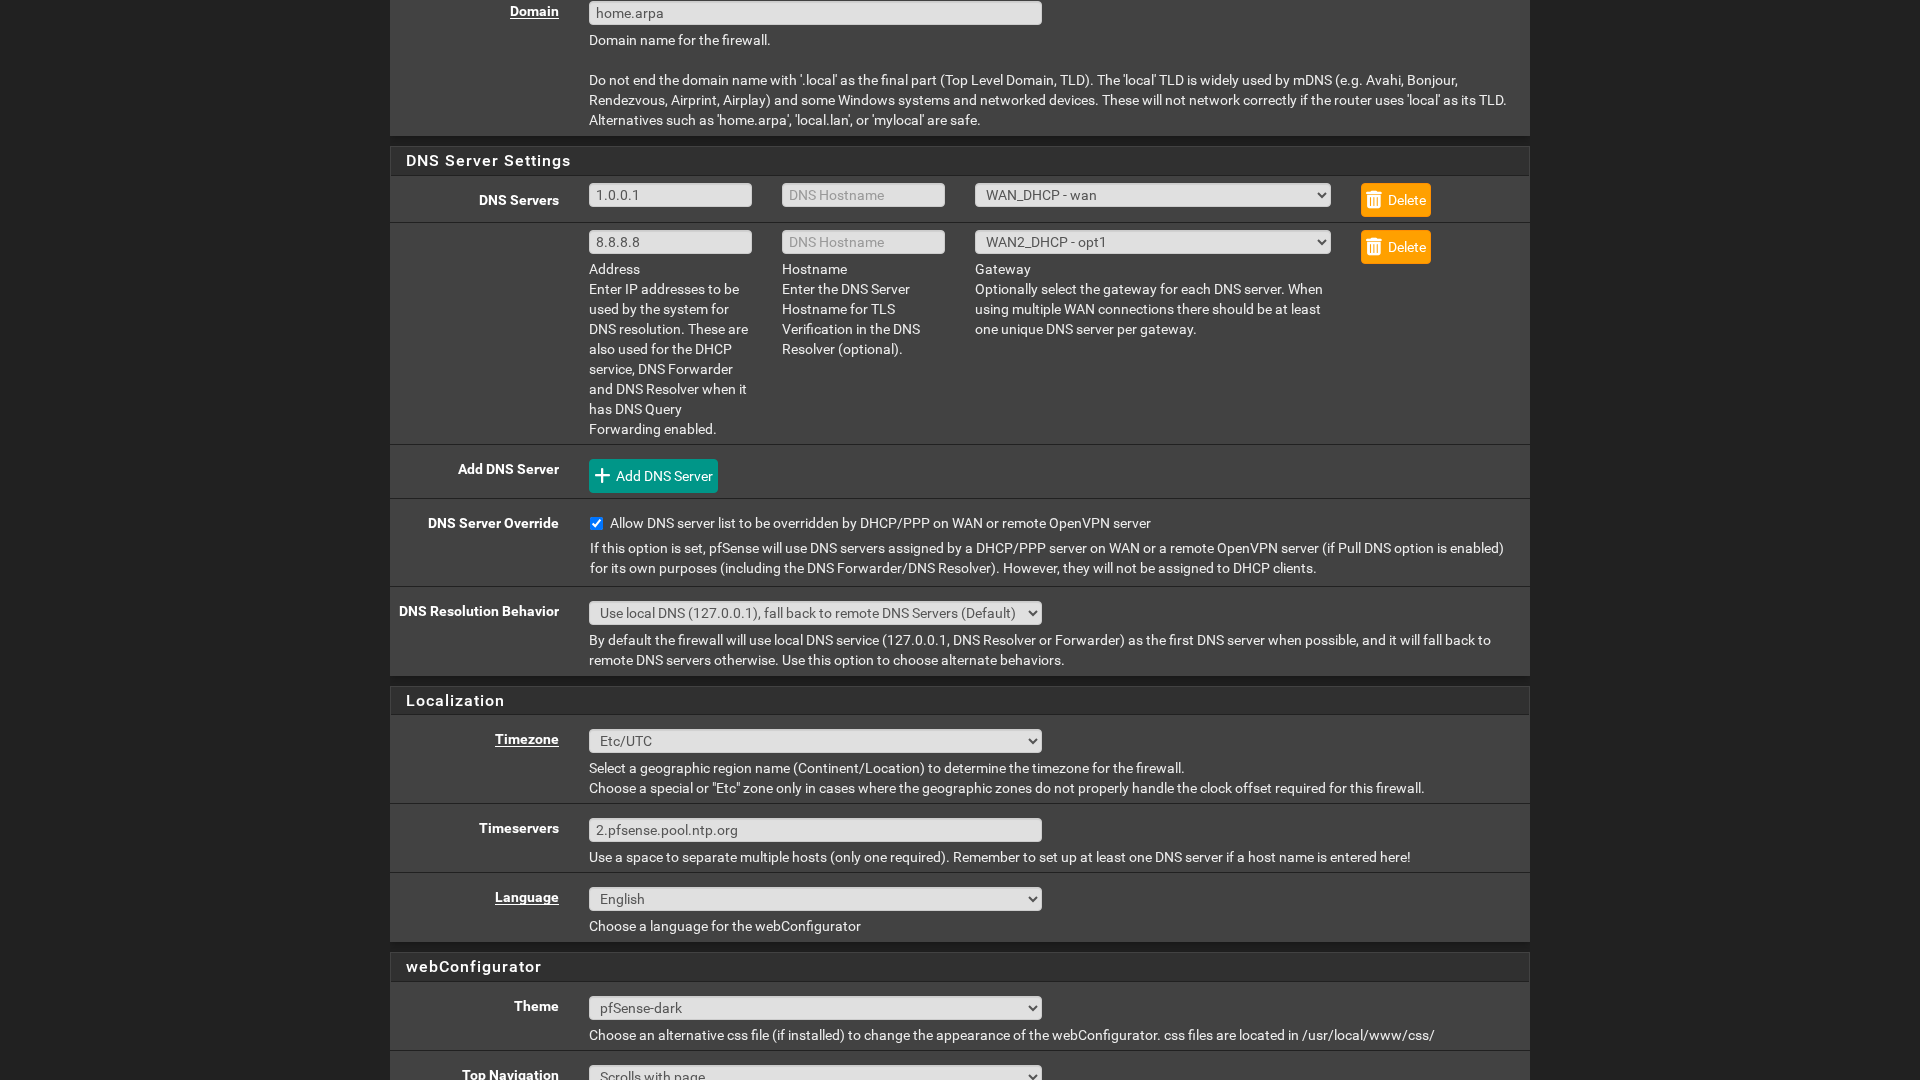
2. Select Save.
3. For forwarding mode only, open Services, then DNS Resolver, tick Enable Forwarding Mode, untick Enable DNSSEC Support, then select Save and Apply Changes.
Netgate’s multi-WAN DNS guidance covers the rest.
Dual WAN Load Balancing in pfSense
To load balance, build a second group with both gateways on Tier 1 and set it on the LAN rule’s Gateway field, never on the default gateway. My pfSense load balancing guide has more background.
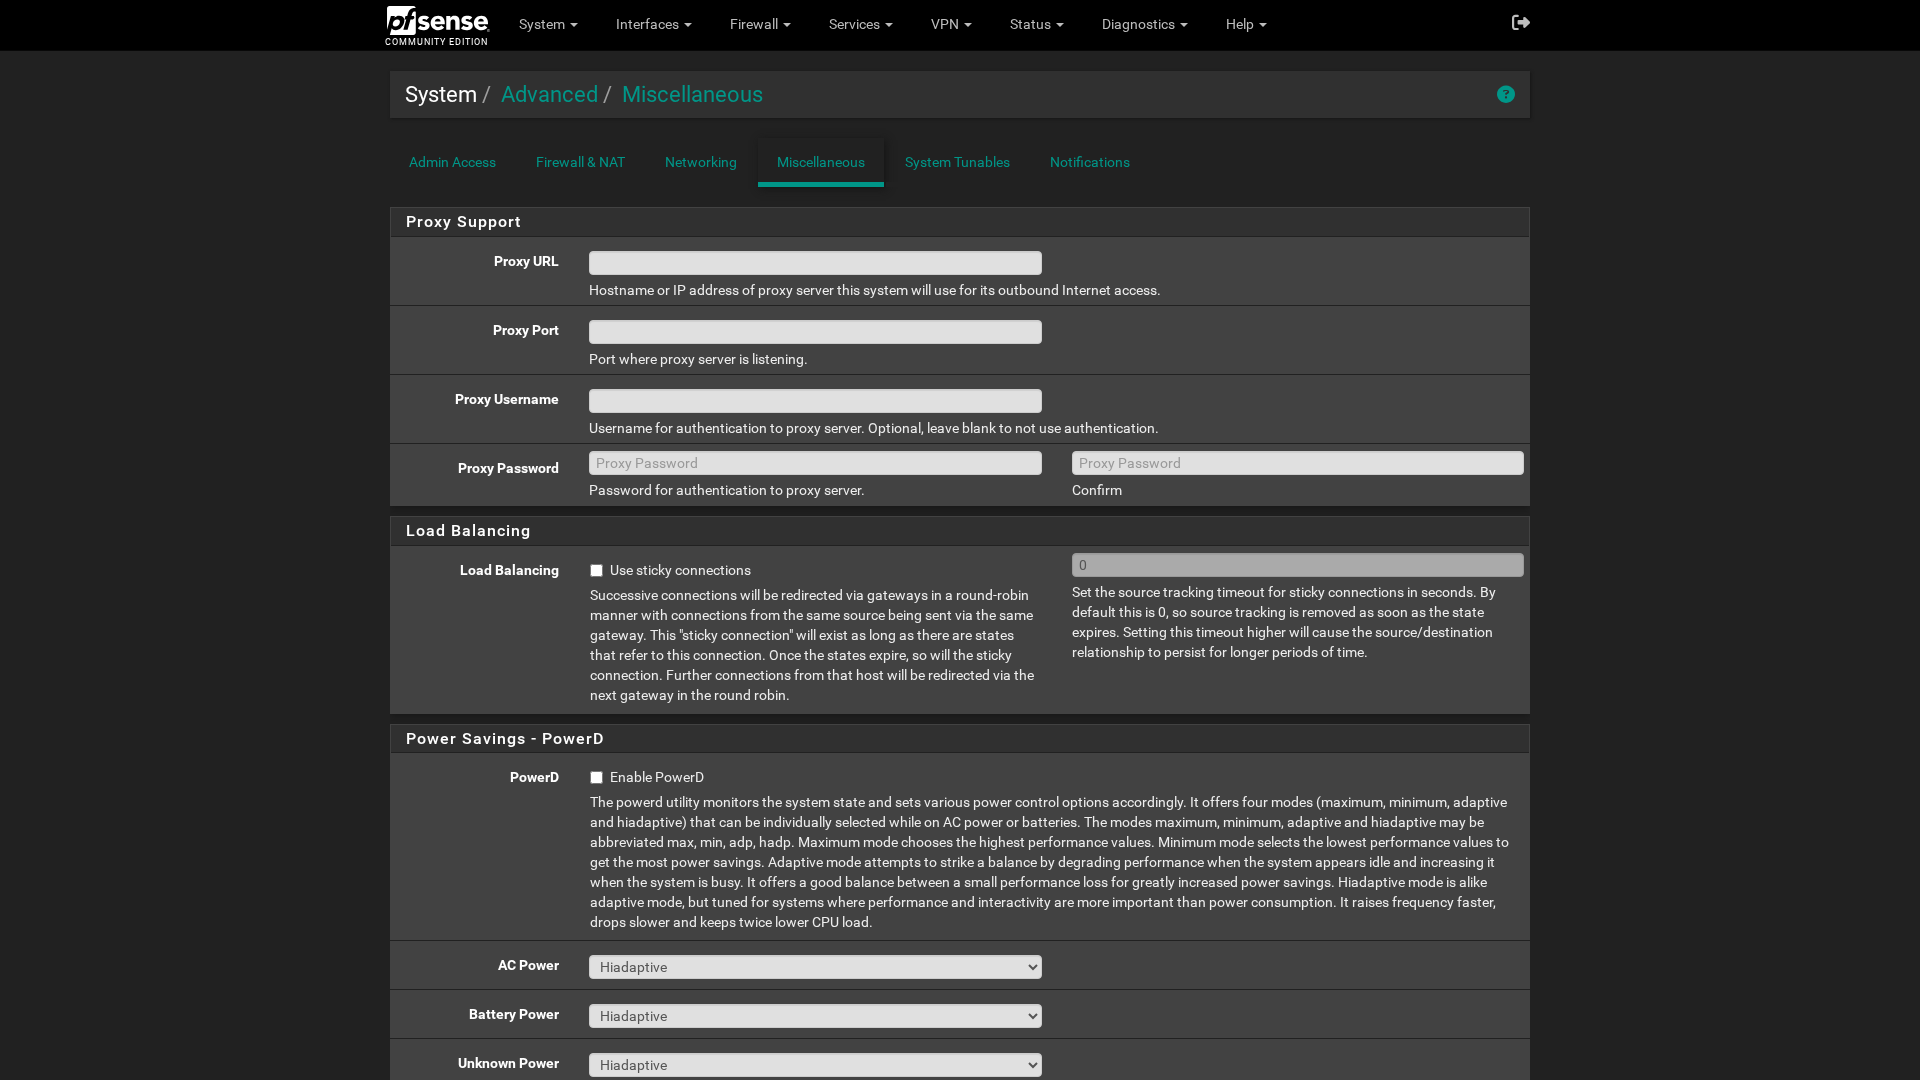
Round-robin can put one client on two public IPs at once, which breaks banks and similar sites. Ticking Use sticky connections, under Load Balancing on System > Advanced > Miscellaneous, then Save, keeps a source on one gateway while it has open states. It was broken in 2.8.0 and fixed in 2.8.1 (September 2025).
How to Test pfSense WAN Failover
If you’re on anything older than CE 2.9.0 (August 2026), update first, since it made gateway recovery work for a default failover group whose gateways had all gone offline. These follow Netgate’s multi-WAN testing steps.
1. Open Status, then Gateways, and check that both WAN gateways read Online (an unused IPv6 gateway can sit at Pending), then do the same on the Gateway Groups tab. If a WAN gateway doesn’t, check its monitor IP.
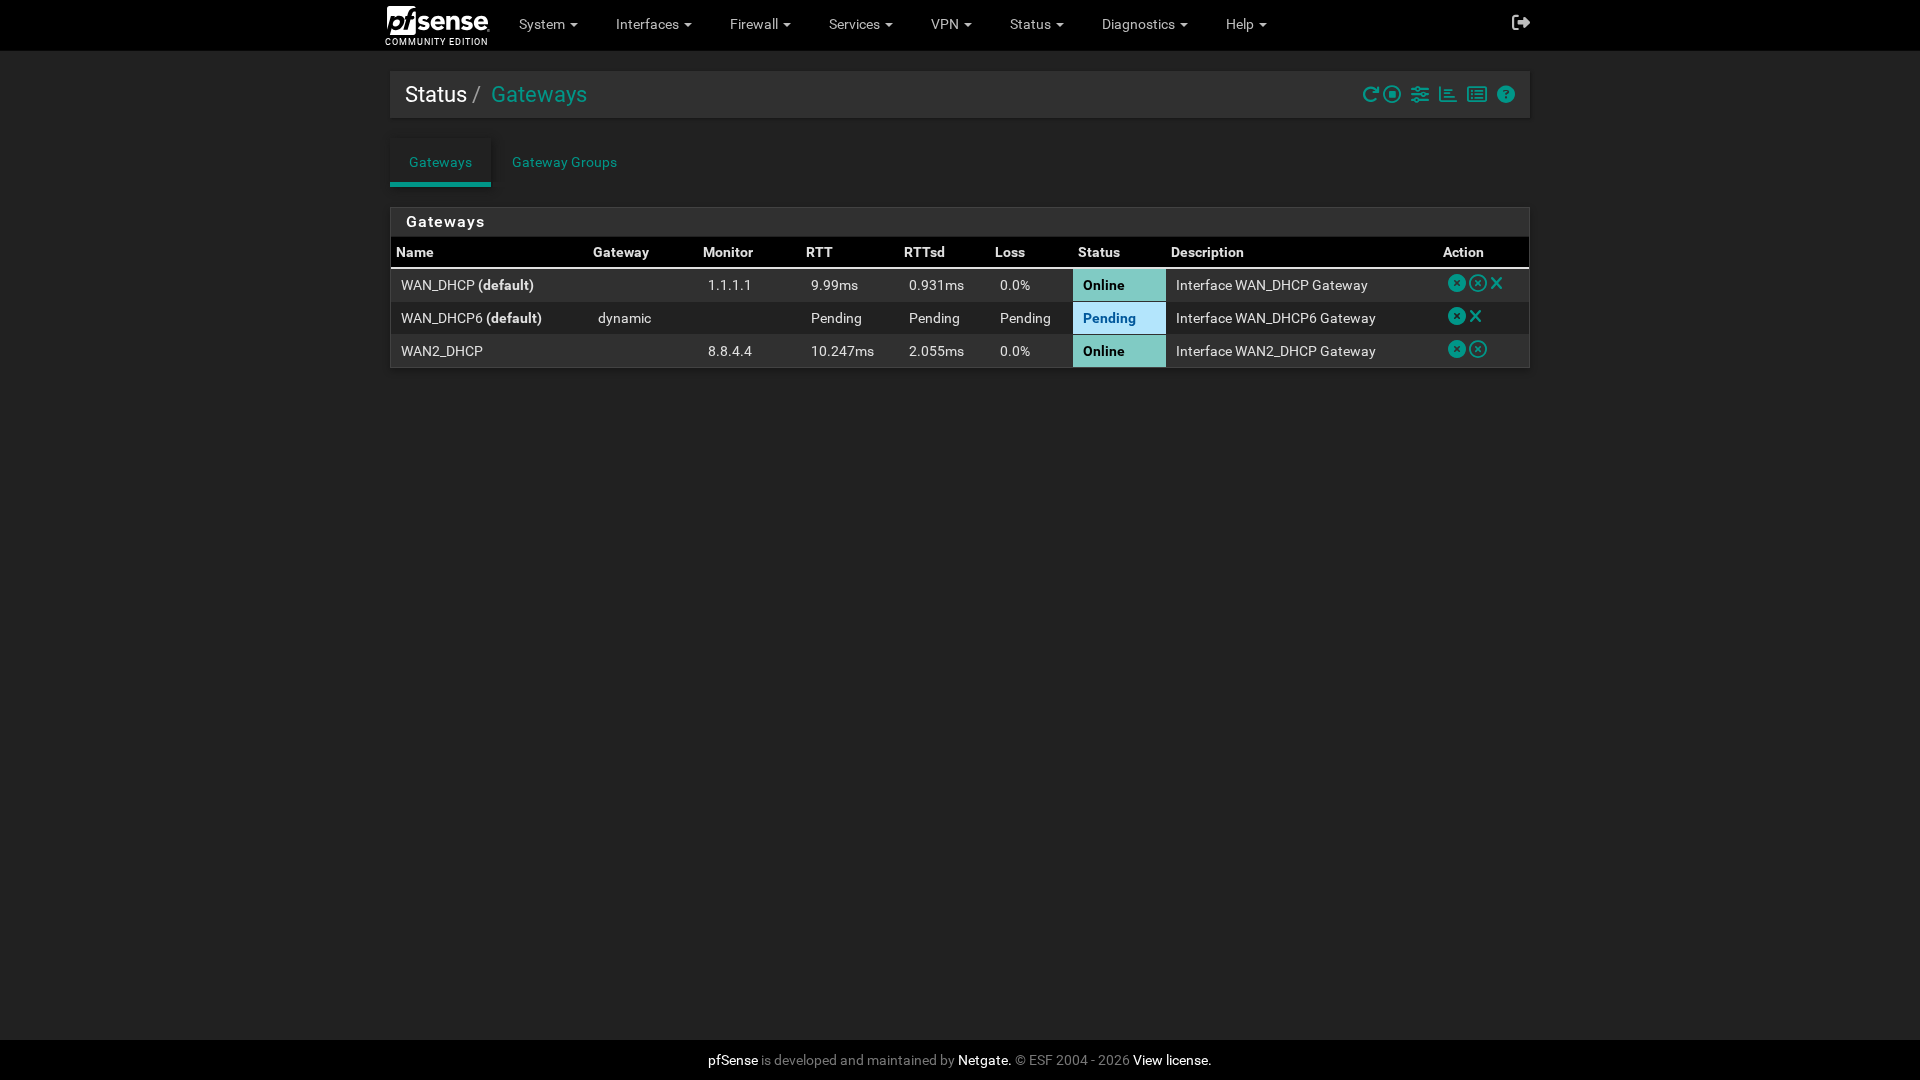
2. Unplug the primary WAN’s cable and refresh Status > Gateways. A DHCP WAN shows dynamic and Pending rather than Offline, because it loses its address. Then run this from a LAN client (in Windows PowerShell, type curl.exe); it should return WAN2’s public address.
curl -4 https://files00.netgate.com/ip3. Reconnect it and wait for Online, then repeat with the modem powered off, and again with only the coax or phone line pulled. That last test catches a monitor IP still pointed at the modem.
Open connections keep their state by default. Setting State Killing on Gateway Failure (under Gateway Monitoring on System > Advanced > Miscellaneous) to Kill states for all gateways which are down, then Save, clears policy-routed ones so VoIP can re-register, though pfSense warns it may not act on a DHCP gateway that lost link.
For a load-balancing group, run the curl command several times (from a few LAN clients if Use sticky connections is on): the address should change at least a few times.
Defaults like these change between releases and nothing is guaranteed, so run the failover test again after every update.