Tailscale on pfSense is a package you install from the Package Manager, and once it’s set up, you can reach your whole home network from anywhere. On pfSense CE 2.9.0 (as of November 2026), the package is Tailscale 0.1.10 with tailscale 1.98.5. The pfSense Tailscale setup comes down to five steps: install the package, connect it with an auth key, advertise your LAN, approve that route in the Tailscale admin console, and, if you’d like, turn pfSense into an exit node.
I set this up on a test pfSense box for a video in October 2022. The step that decides whether you can reach your LAN happens outside pfSense: approving the subnet route in the Tailscale admin console.
I’ve never port forwarded to reach my own network, and Tailscale, which I described in 2022 as a zero configuration VPN, doesn’t need a port forward either. If you’d rather run a traditional VPN, OpenVPN on pfSense and WireGuard on pfSense both work, but both need a port opened on the WAN. Tailscale vs WireGuard covers how to choose, and if you’re on OPNsense, there’s a separate guide for Tailscale on OPNsense.
Install the Tailscale Package
The Tailscale pfSense package is in the regular package list, and Netgate’s Tailscale on pfSense post lists it for both Plus and Community Edition users.
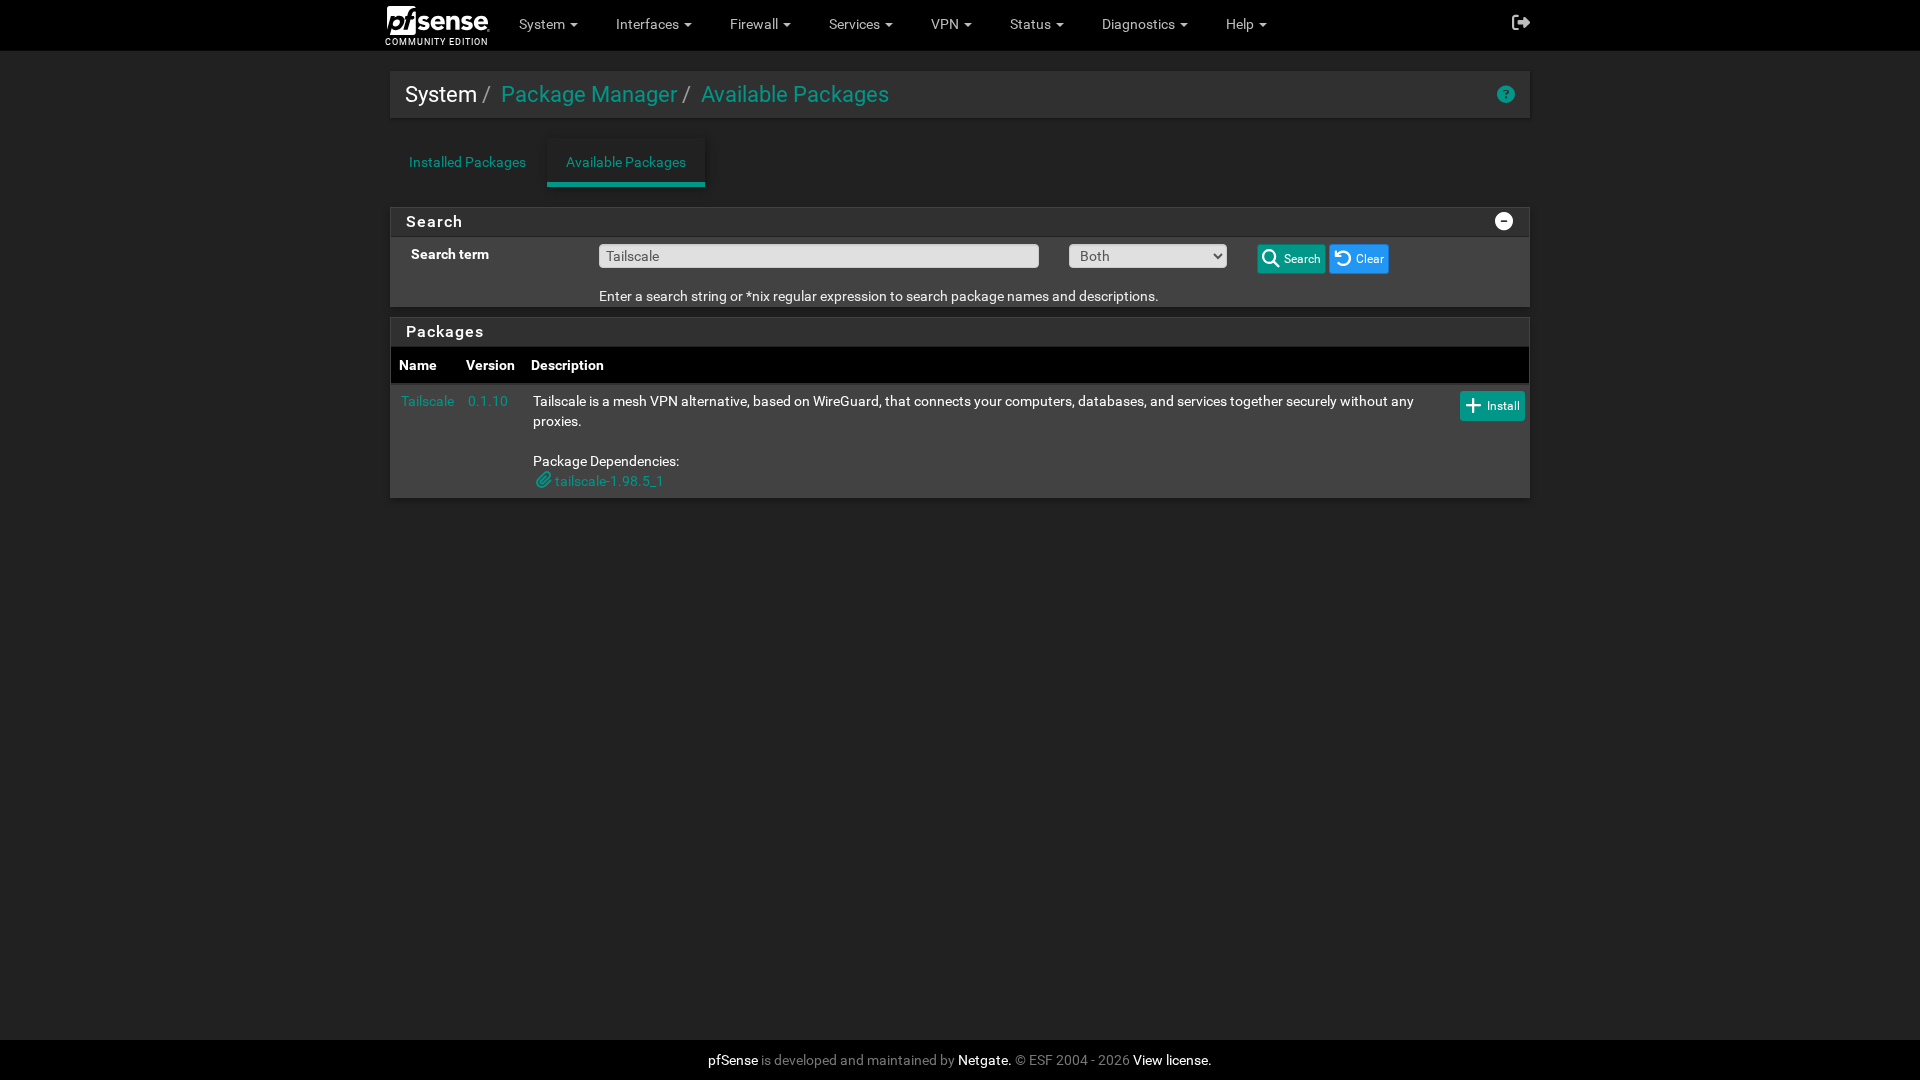
1. Open System, select Package Manager, and finally, Available Packages.
2. Search for Tailscale and select Install on the Tailscale row (version 0.1.10, which pulls in tailscale-1.98.5_1 as its dependency).
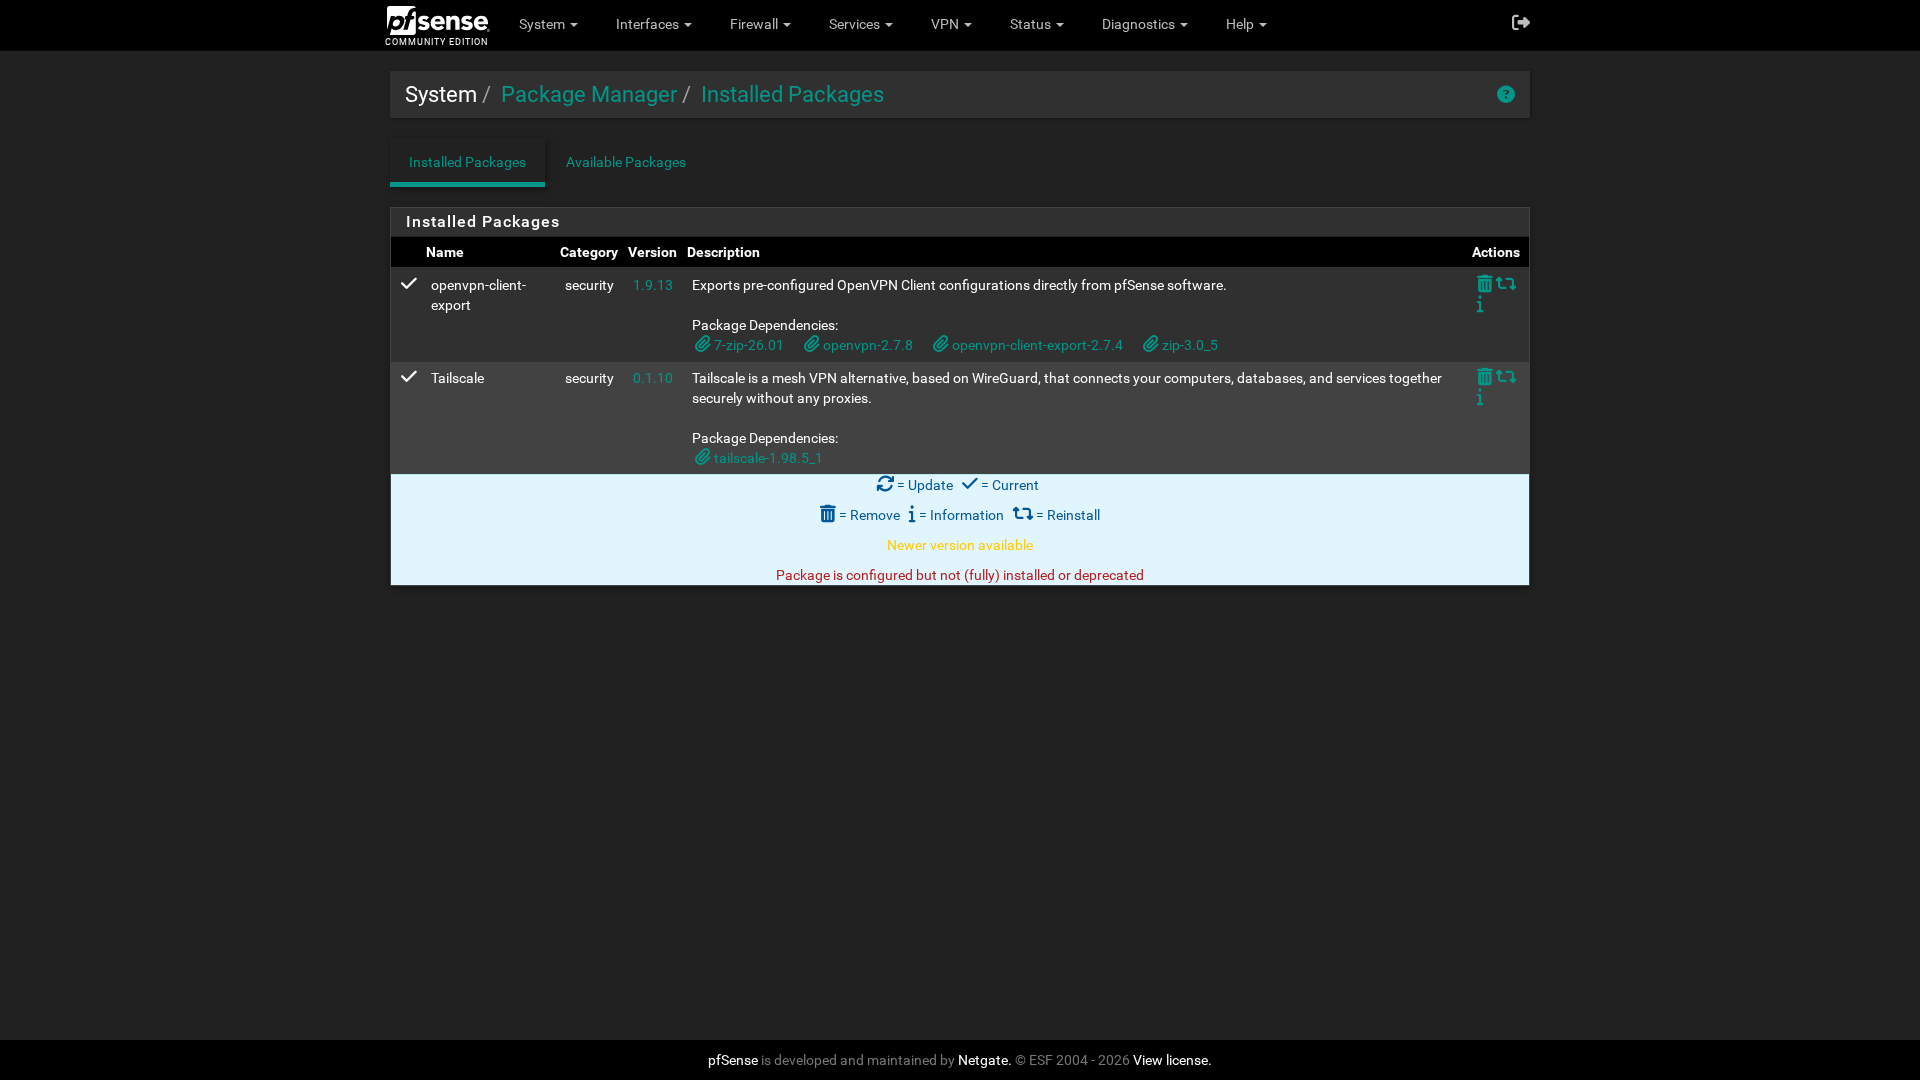
3. Select Confirm. When it finishes, you’ll see “pfSense-pkg-Tailscale installation successfully completed.” and Tailscale is listed under Installed Packages.
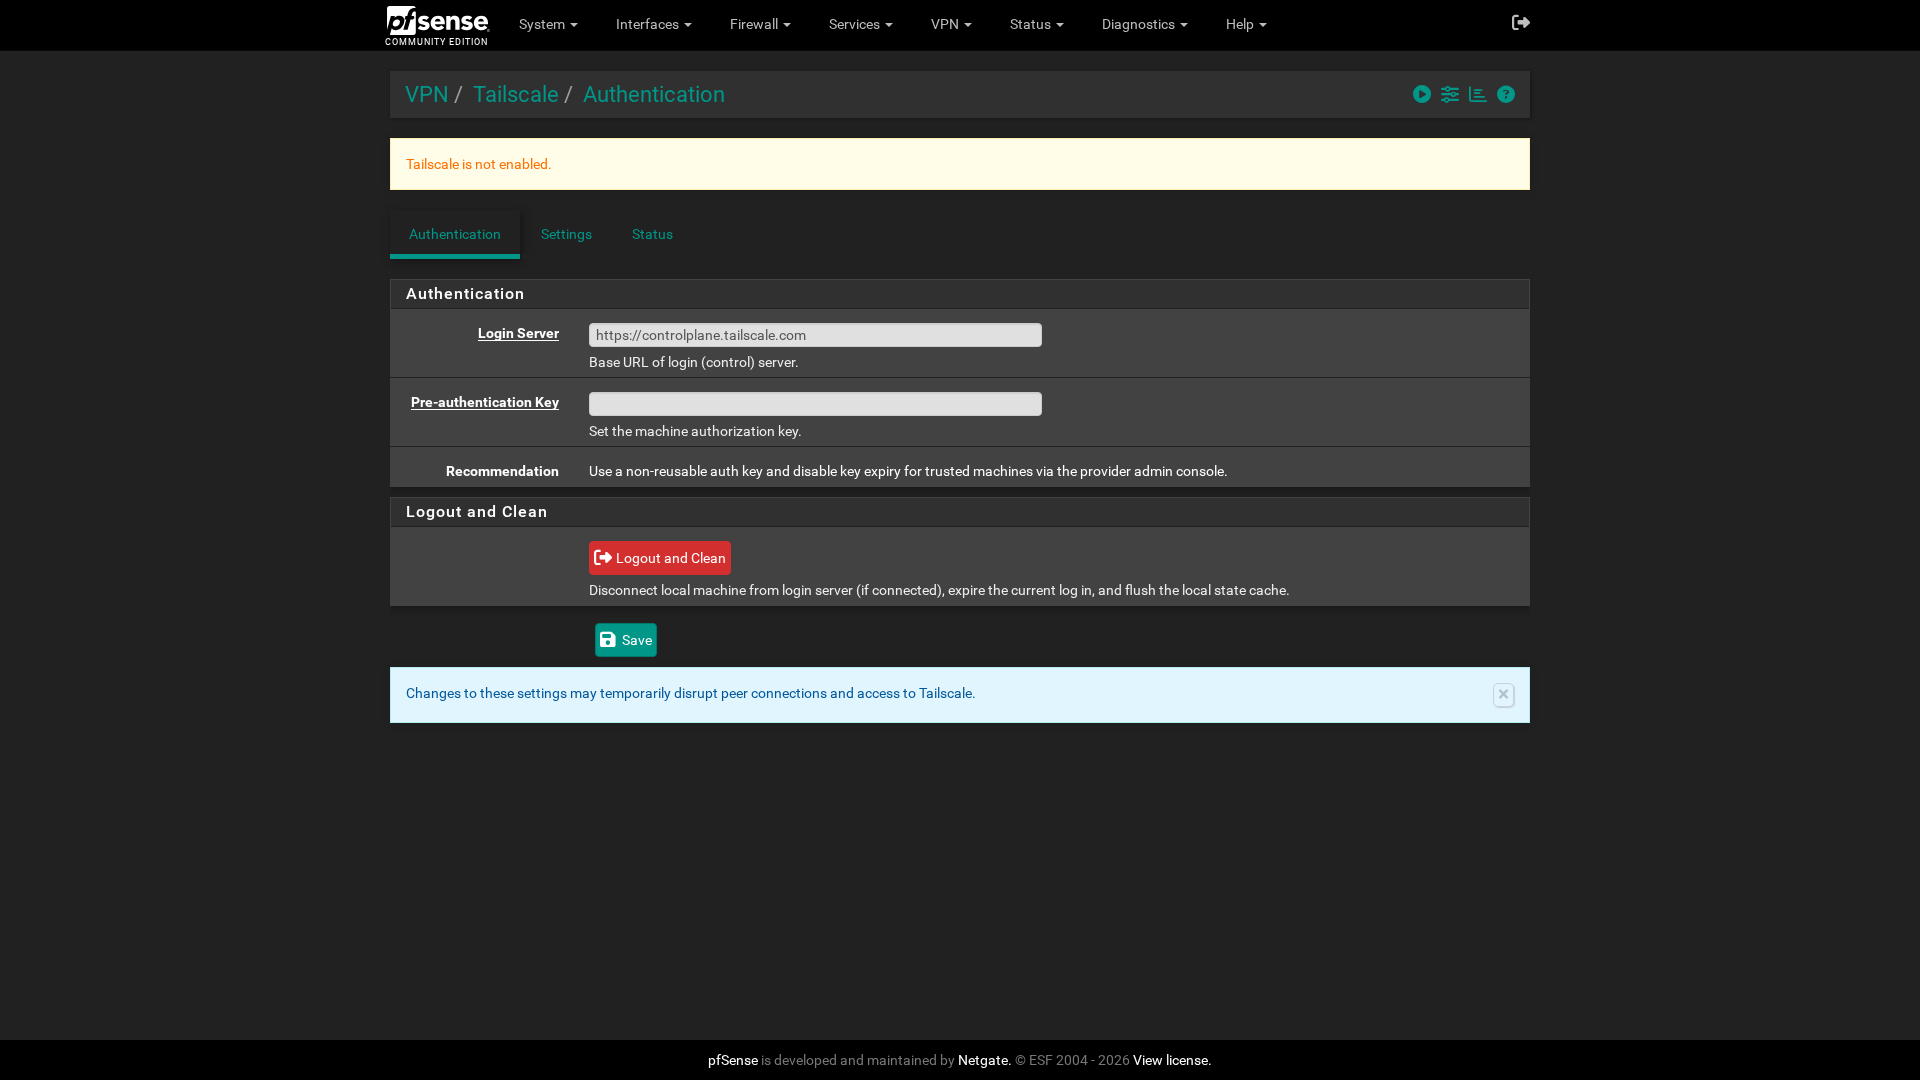
The package adds VPN > Tailscale to the menu with Authentication, Settings and Status tabs, and each one shows “Tailscale is not enabled.” until you turn the service on. It also creates an interface group named Tailscale and a matching Tailscale tab under Firewall > Rules. You don’t need to assign an interface for it the way you would for WireGuard.
Generate a Tailscale Auth Key
pfSense logs in to Tailscale with an auth key, which you create in the Tailscale admin console. If you don’t have an account yet, create one on the Tailscale website first.
1. In the admin console, open Settings, select Keys, and select Generate auth key.
2. Leave Reusable and Ephemeral off, pick an expiry (anything from 1 to 90 days, and 90 if you don’t set one), and select Generate key.
3. Copy the key, since you’ll paste it into pfSense in the next section.
The package’s own Authentication page recommends a non-reusable key, and Tailscale’s auth keys docs say “Be very careful with reusable keys!” because they can be very dangerous if stolen. Ephemeral is the wrong choice for a firewall, as Tailscale removes ephemeral devices once they go inactive. The key’s own expiry only matters until you use it, since a device it authorized stays authorized until its node key expires, and that’s the expiry you turn off next.
Connect pfSense to Your Tailnet
Now that you have the key, the pfSense side lives under VPN > Tailscale: the Authentication tab holds the key and the Settings tab turns the service on.
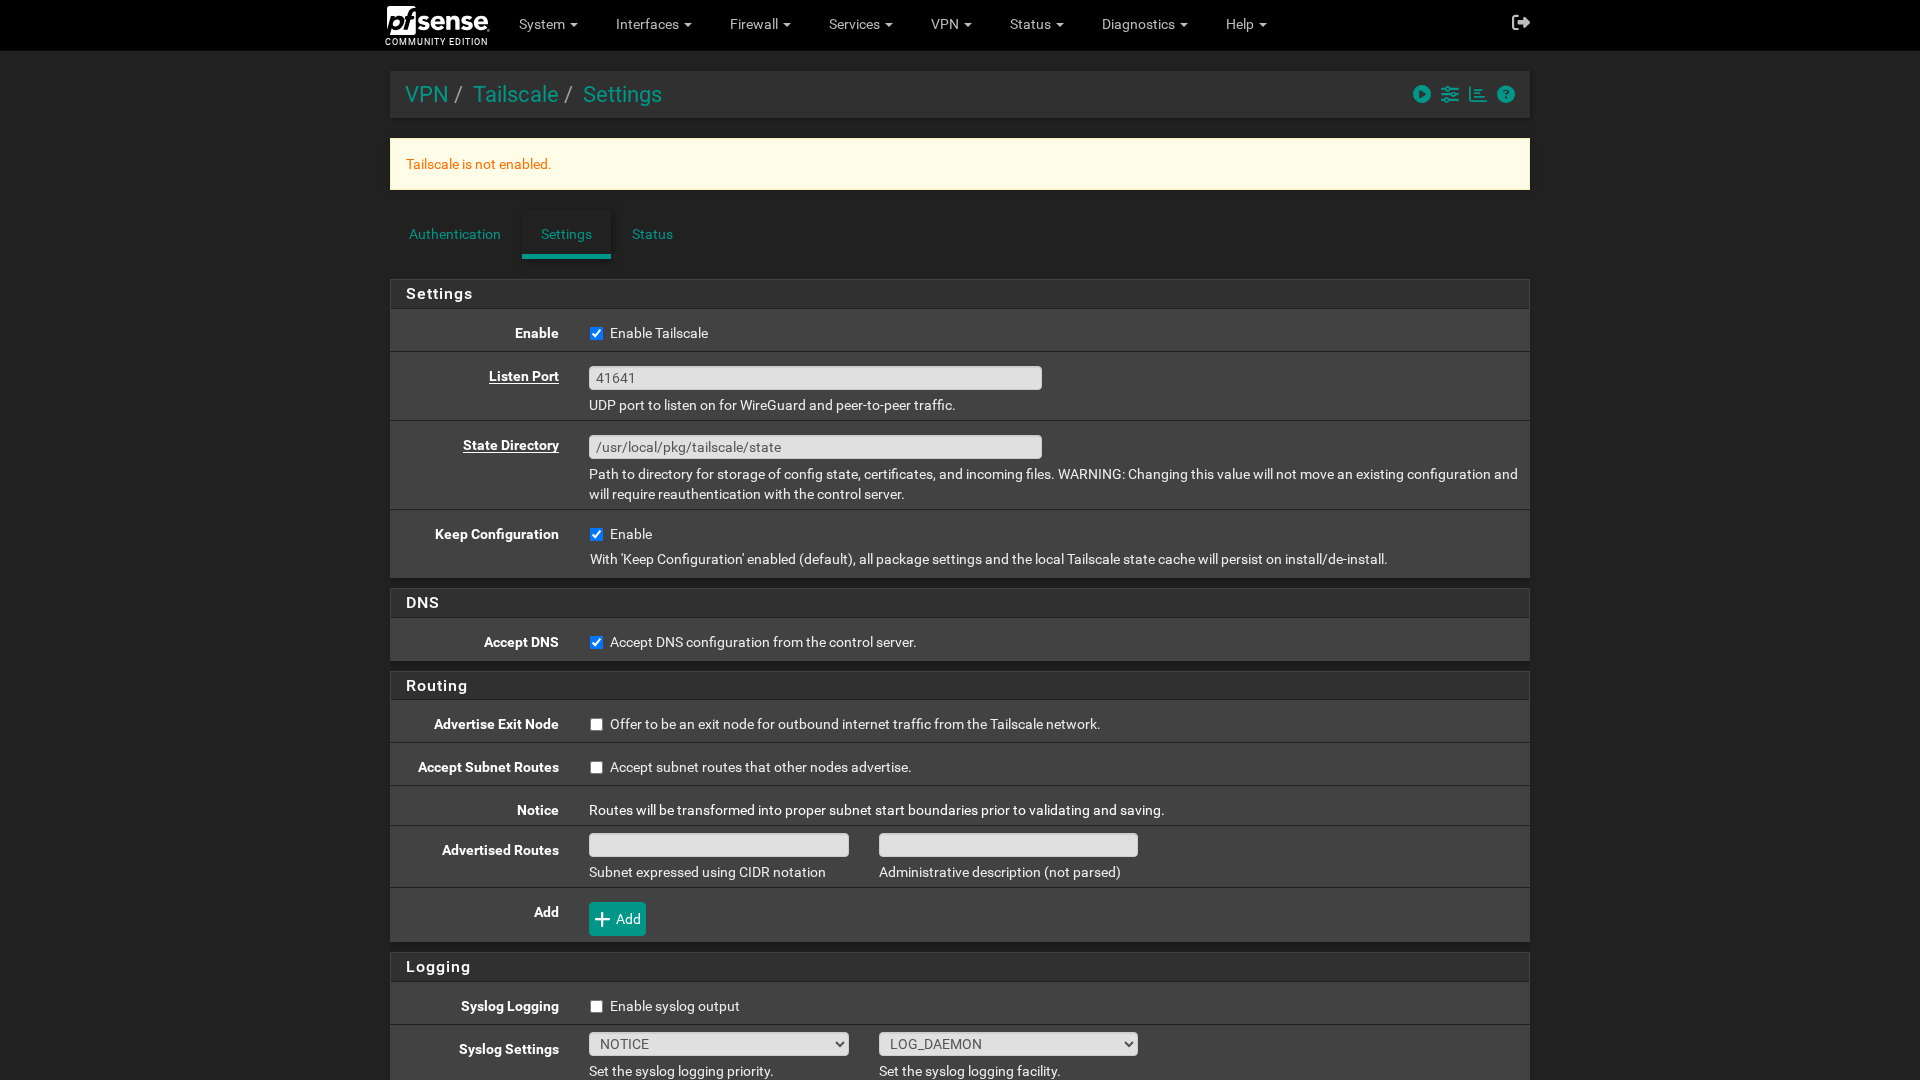
1. Open VPN, select Tailscale, and finally, the Authentication tab. Leave Login Server at https://controlplane.tailscale.com, paste the key into Pre-authentication Key, and select Save.
2. Select the Settings tab, tick Enable (“Enable Tailscale”), leave Listen Port at 41641, and select Save. The Status tab shows the firewall’s Tailscale status once it’s running.
3. Once pfSense shows up on the admin console’s Machines page, select the menu at the far right of its row, and select Disable Key Expiry.
Node keys expire every 180 days by default, and Tailscale’s key expiry docs name subnet routers as one of the devices to turn it off for.
If pfSense drops off because its node key expired, select Temporarily extend key in its Machines menu, then Disable Key Expiry within the 30 minutes. If it’s still off, remove it from Machines, select Logout and Clean on the Authentication tab, paste a fresh non-reusable key, select Save, and start the service with the Start Service (play) icon at the top of the page. It comes back as a new machine, so disable key expiry and approve its routes again.
Advertise Your LAN as a Subnet Route
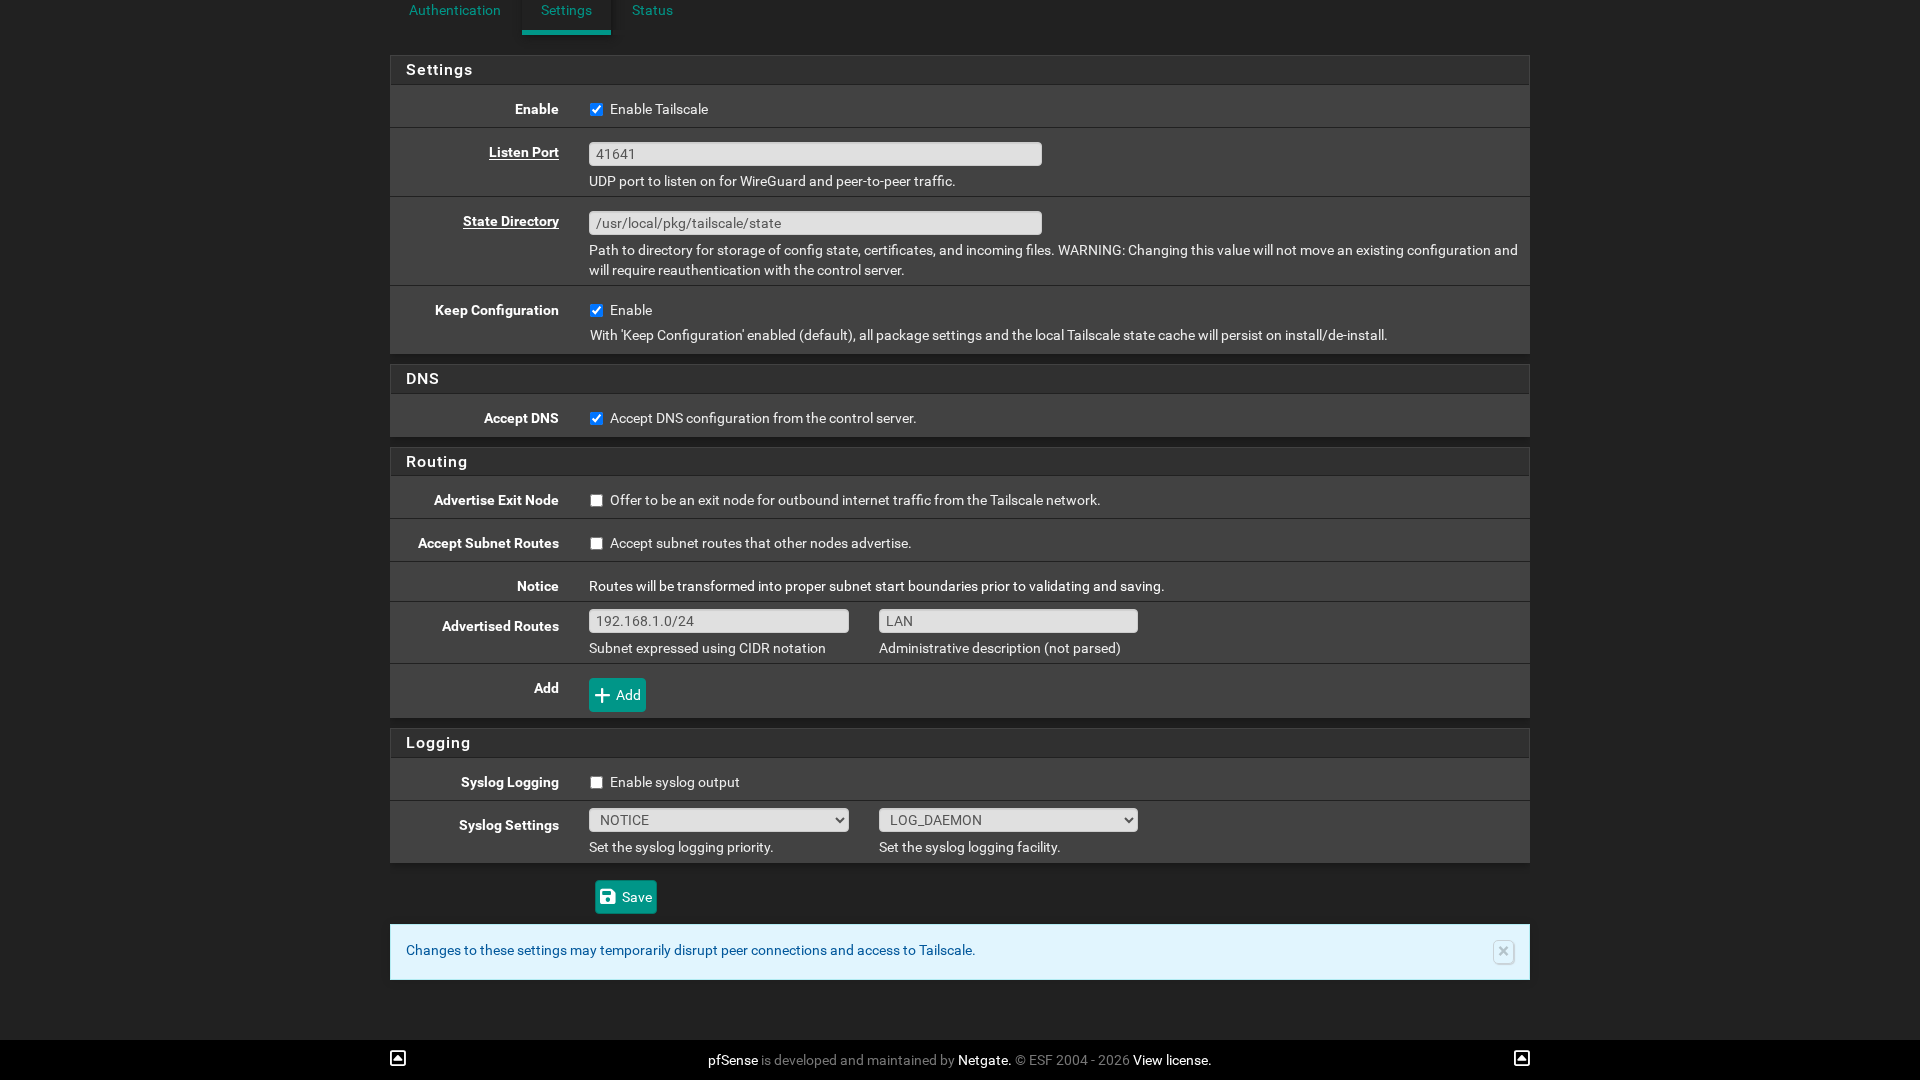
Advertised routes are just the local subnets you want to reach over Tailscale. You add them under VPN > Tailscale > Settings > Routing, then approve them on the admin console’s Machines page. When I set this up in 2022, it was my 192.168.100 subnet, but yours is going to be something different depending on what you have at home. If you set up VLANs in pfSense, each one gets its own row.
1. On VPN > Tailscale > Settings, scroll to Routing, enter your LAN in CIDR notation under Advertised Routes (for example, 192.168.1.0/24), and give it a description. Select Add for each extra subnet.
2. Select Save.
3. In the admin console, open Machines and find pfSense (it carries a Subnets badge, or filter by property:subnet). Select it, select the routes in its Subnets section, and Save.
Until that approval is done, nothing reaches your LAN. If you’d rather not approve routes by hand, Tailscale’s subnet routers docs cover autoApprovers in the policy file. Android, iOS, macOS, tvOS and Windows clients pick up the route automatically, while Linux clients need --accept-routes. Leave Accept Subnet Routes unticked, since that’s for pfSense using routes other nodes advertise.
Use pfSense as a Tailscale Exit Node
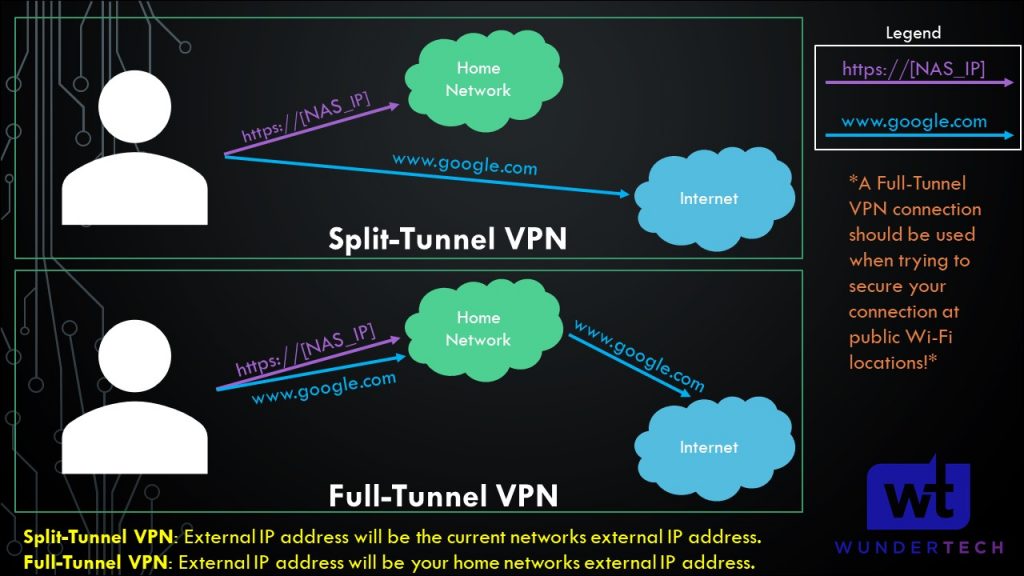
A pfSense Tailscale exit node is how you get a full tunnel VPN out of this. As I explained it in 2022, when you use the exit node, all traffic routes through it. When a device’s exit node is set to None, it’s a split tunnel, and only your tailnet and advertised subnets go over Tailscale. You don’t have to use pfSense as an exit node, but it’s useful on public Wi-Fi.
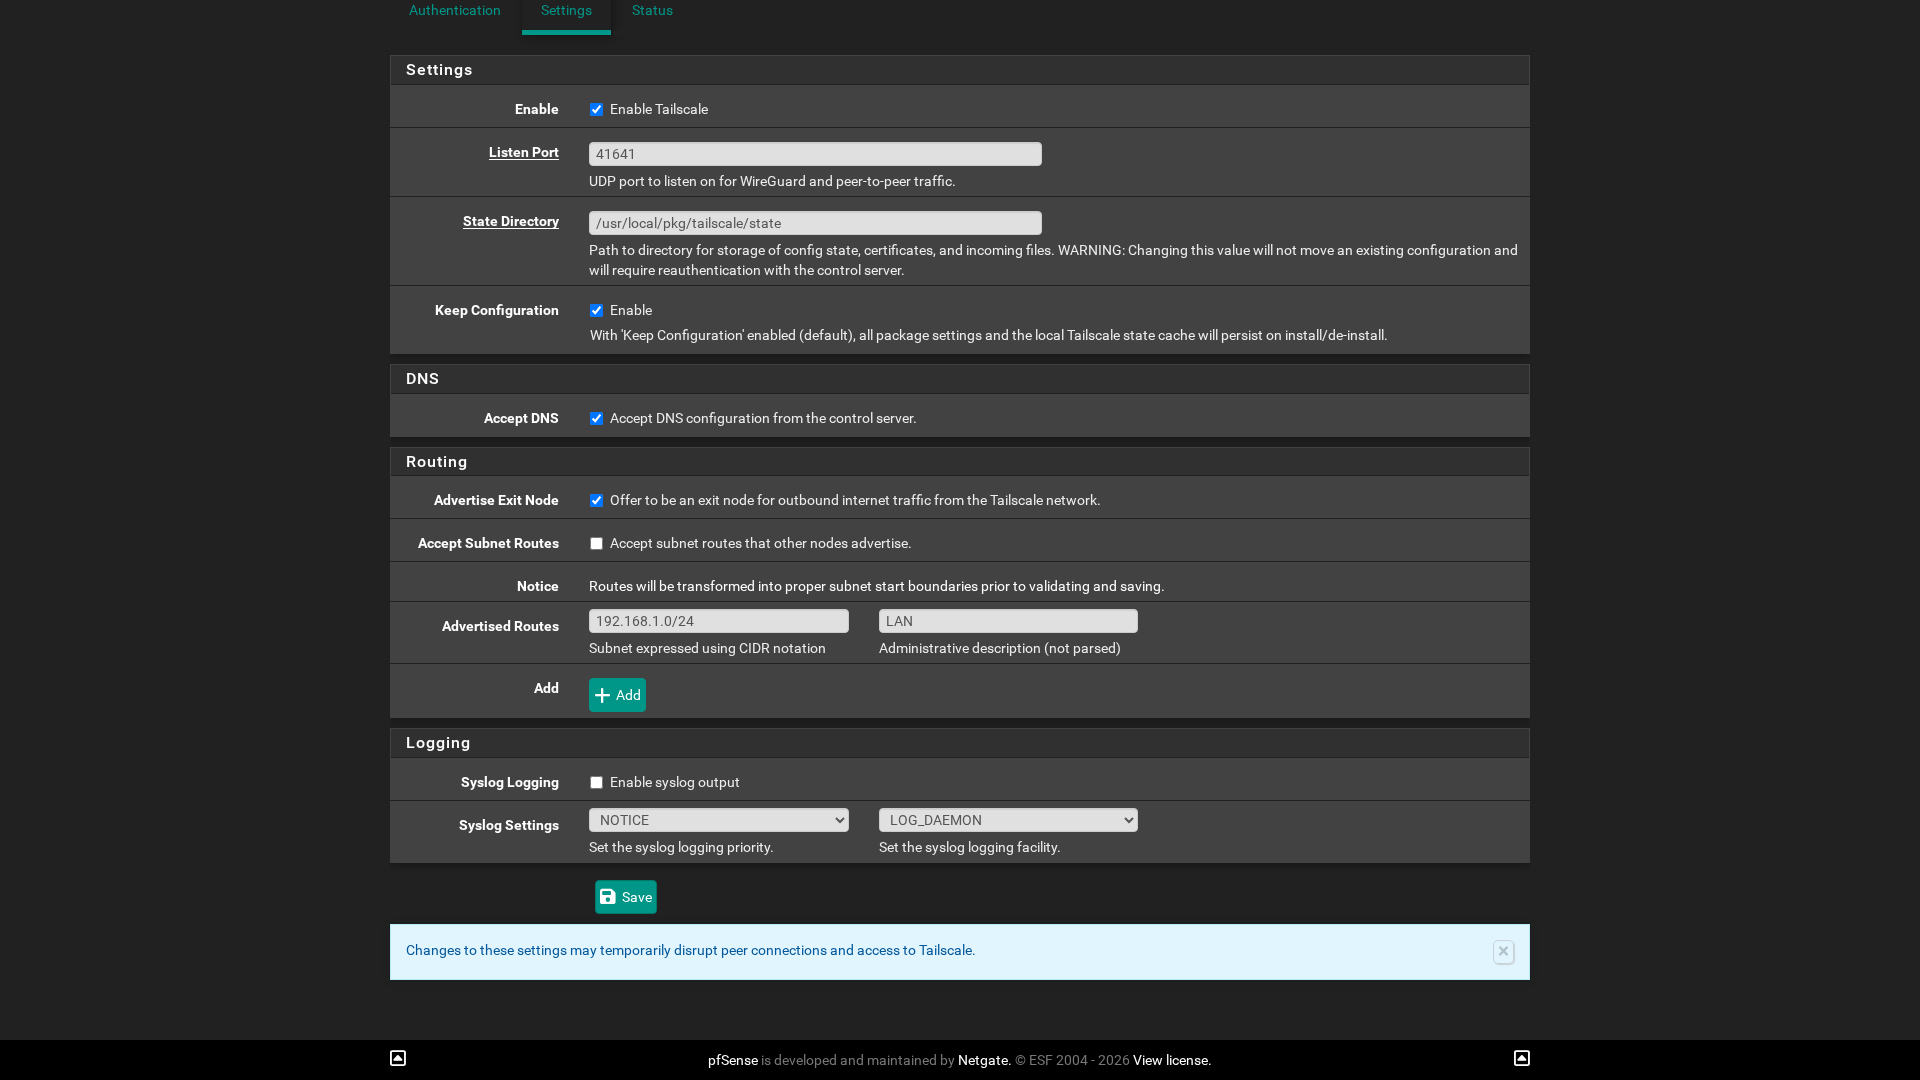
1. On VPN > Tailscale > Settings, tick Advertise Exit Node (“Offer to be an exit node for outbound internet traffic from the Tailscale network.”) under Routing, and select Save.
2. In the admin console, open Machines and find pfSense (it carries an Exit Node badge). Open its menu, select Edit route settings, then Use as exit node.
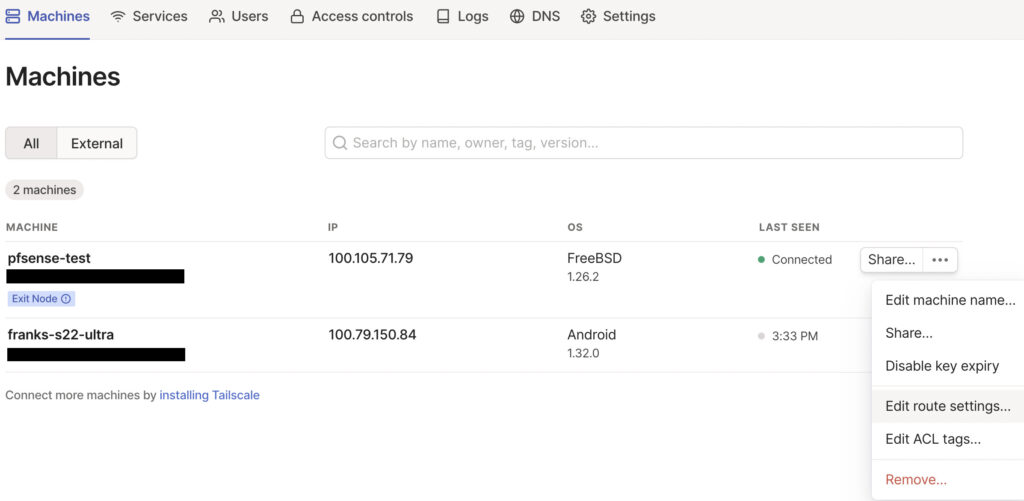
3. On each client, choose pfSense as the exit node and turn on Allow LAN access (Android), Allow Local Network Access (macOS) or Allow local network access (Windows), which keeps your local network reachable.
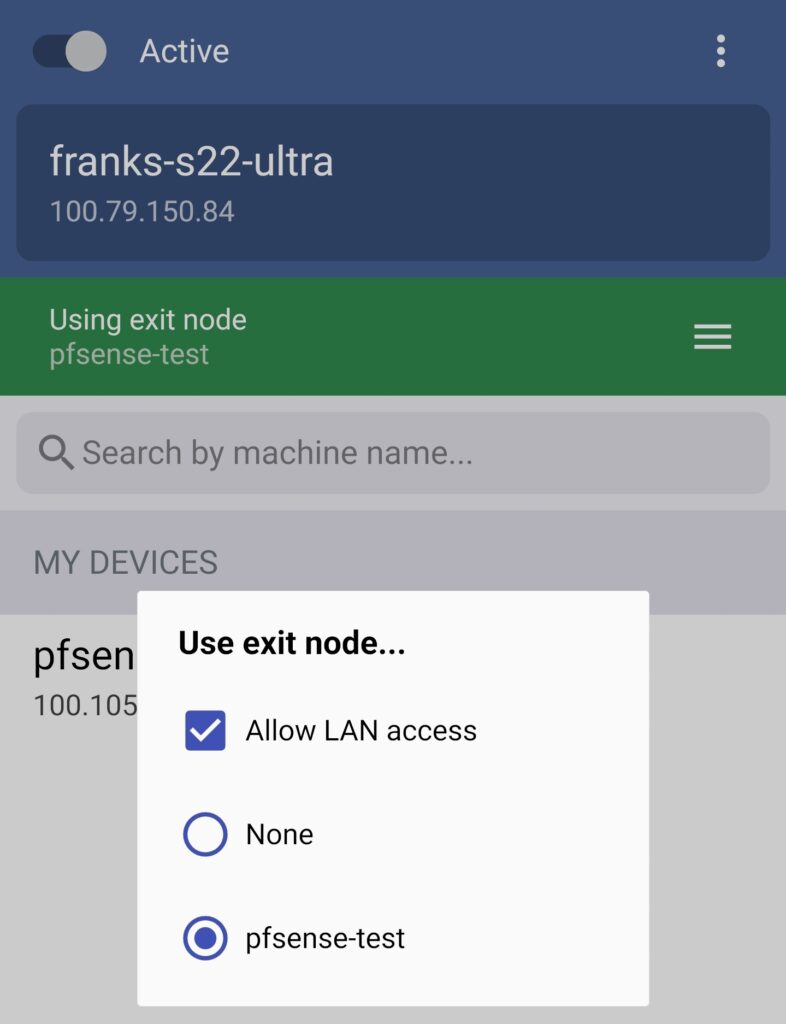
Every client has to opt in before its traffic goes through pfSense. If you narrow your access controls, add a grant with autogroup:internet as its destination, or clients can’t use the exit node. FreeBSD isn’t on the platform list in Tailscale’s exit nodes docs, so this is the package offering it, though it worked on my test box in 2022.
Do You Need a pfSense Firewall Rule for Tailscale?
Not for your LAN or the exit node. Any pfSense Tailscale firewall rules would go on the Tailscale tab under Firewall > Rules, which is empty after install, and it can stay that way. On the current package, Tailscale’s FreeBSD client handles subnet route and exit node traffic in its own network stack and opens those connections from the firewall’s own addresses, so that traffic never reaches the Tailscale tab. Which tailnet devices can reach your LAN is set on the Access controls page of the Tailscale admin console, not in pfSense.
To open the pfSense web GUI over Tailscale, use the firewall’s LAN IP once the route is approved. Its Tailscale IP is the exception, since traffic to that address does go through pfSense’s rules, and the empty Tailscale tab blocks it until you add a pass rule there.
Get Direct Connections Through pfSense NAT
Nothing above needs a port forward (pfSense port forwarding is a separate topic), but there’s one NAT caveat for LAN devices that run their own Tailscale client. Tailscale’s pfSense documentation calls pfSense’s NAT endpoint-dependent (“hard”) NAT, so those devices often can’t connect directly and fall back to Tailscale’s DERP relays.
1. Open Firewall > NAT, select the Outbound tab, choose Hybrid Outbound NAT rule generation, and select Save.
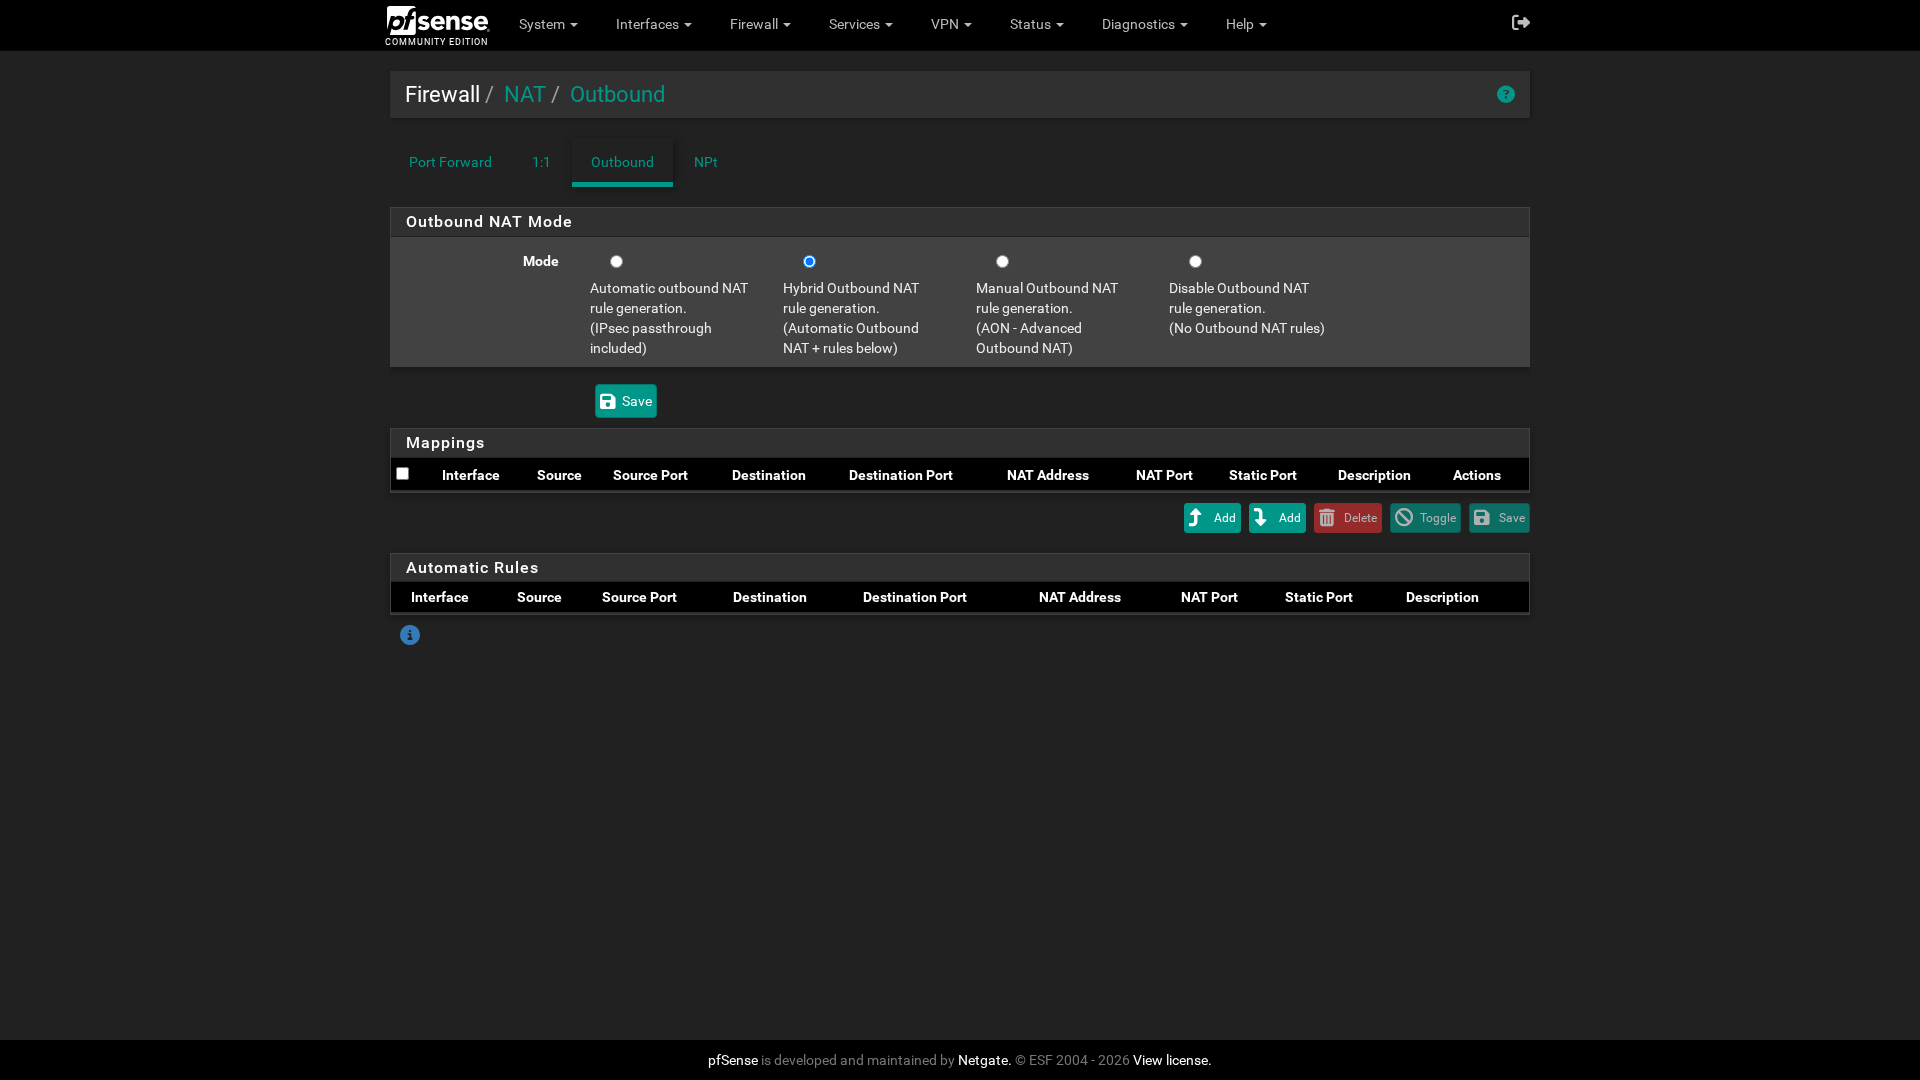
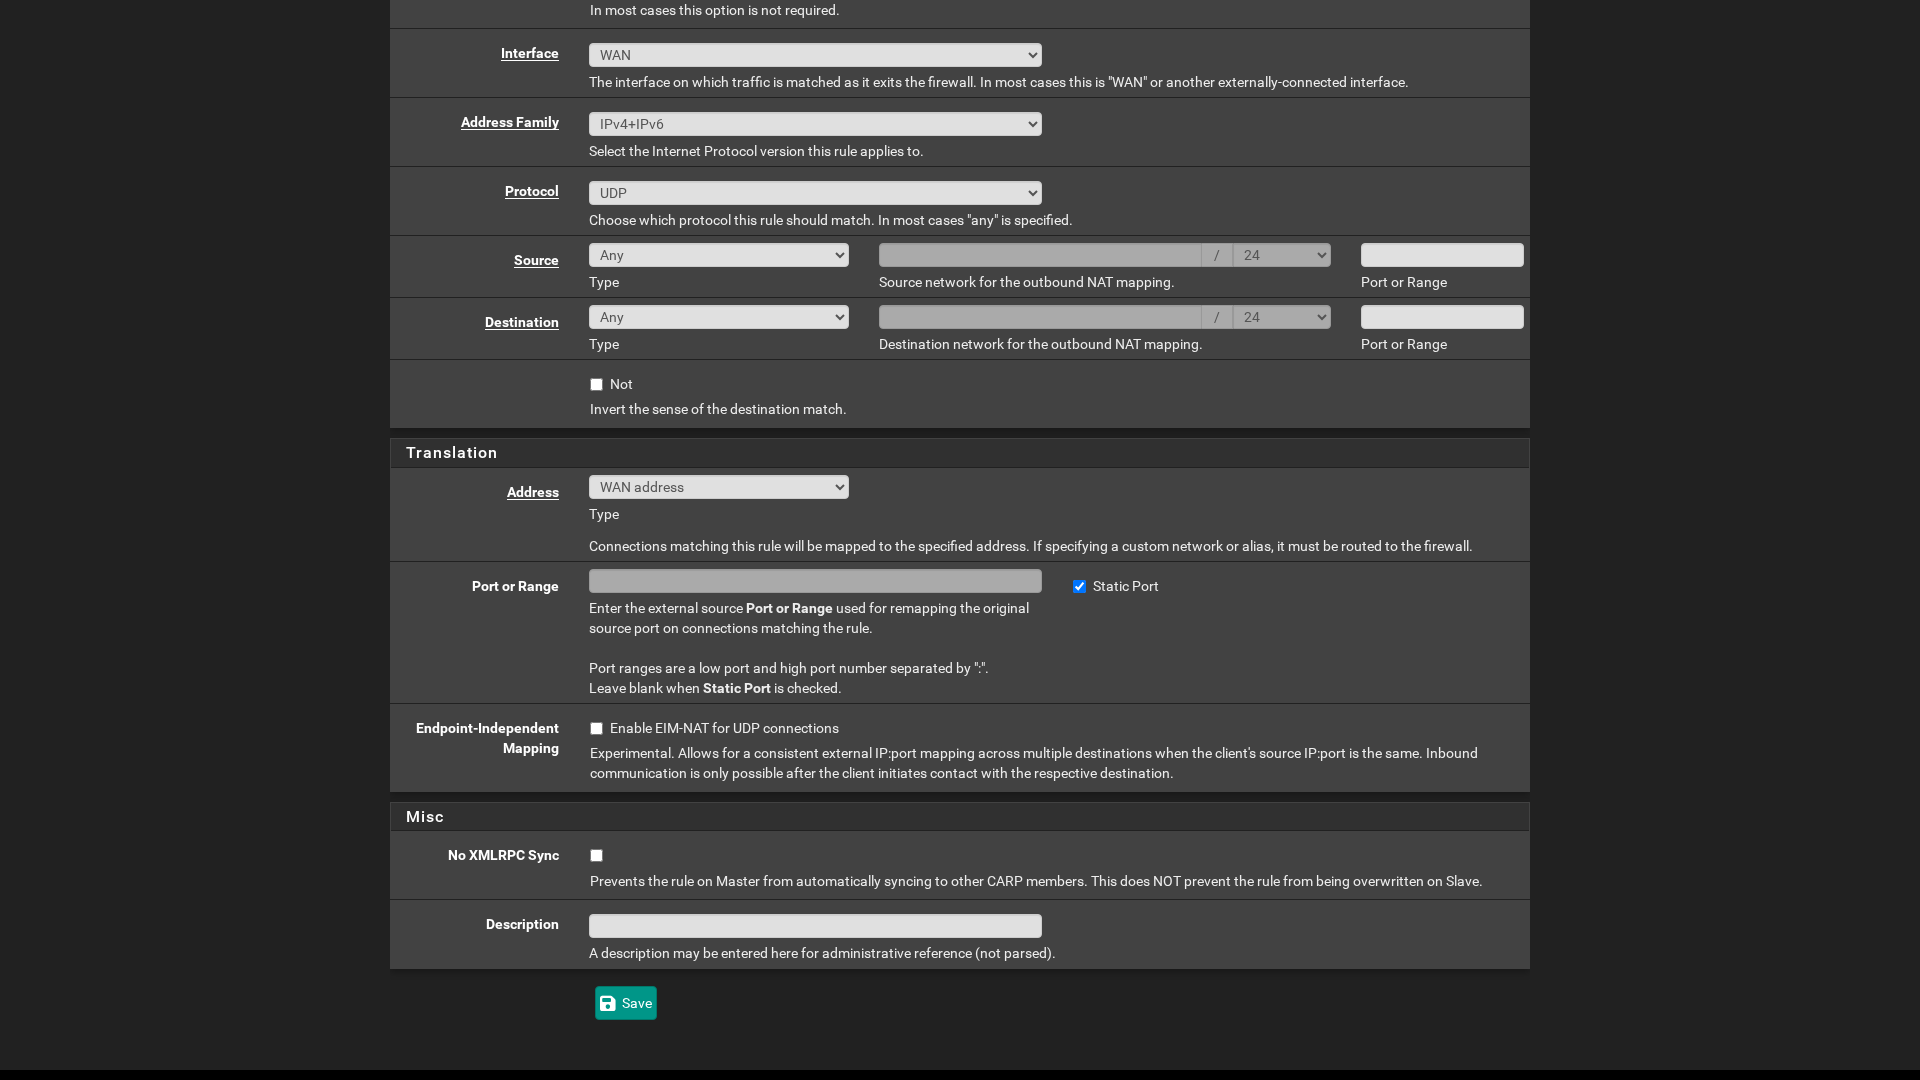
2. Select ↑ Add and set Interface to WAN (the list starts with Tailscale). Set the address family to IPv4+IPv6, Protocol to UDP and the source to Any, leave Translation Address at WAN address, and tick Static Port. Select Save and Apply Changes.
3. In the admin console, open Access controls, select the JSON editor tab, add this line inside the outer braces (with a comma if another entry follows), and select Save. It moves every device on your tailnet off the default port 41641.
"randomizeClientPort": trueOn CE 2.9.0, you can tick Endpoint-Independent Mapping, the experimental box below Static Port, in step 2 instead of Static Port and skip step 3 (pfSense CE 2.9.0 release notes). Tailscale says those mappings can replace randomizeClientPort, and Netgate says never to tick both.
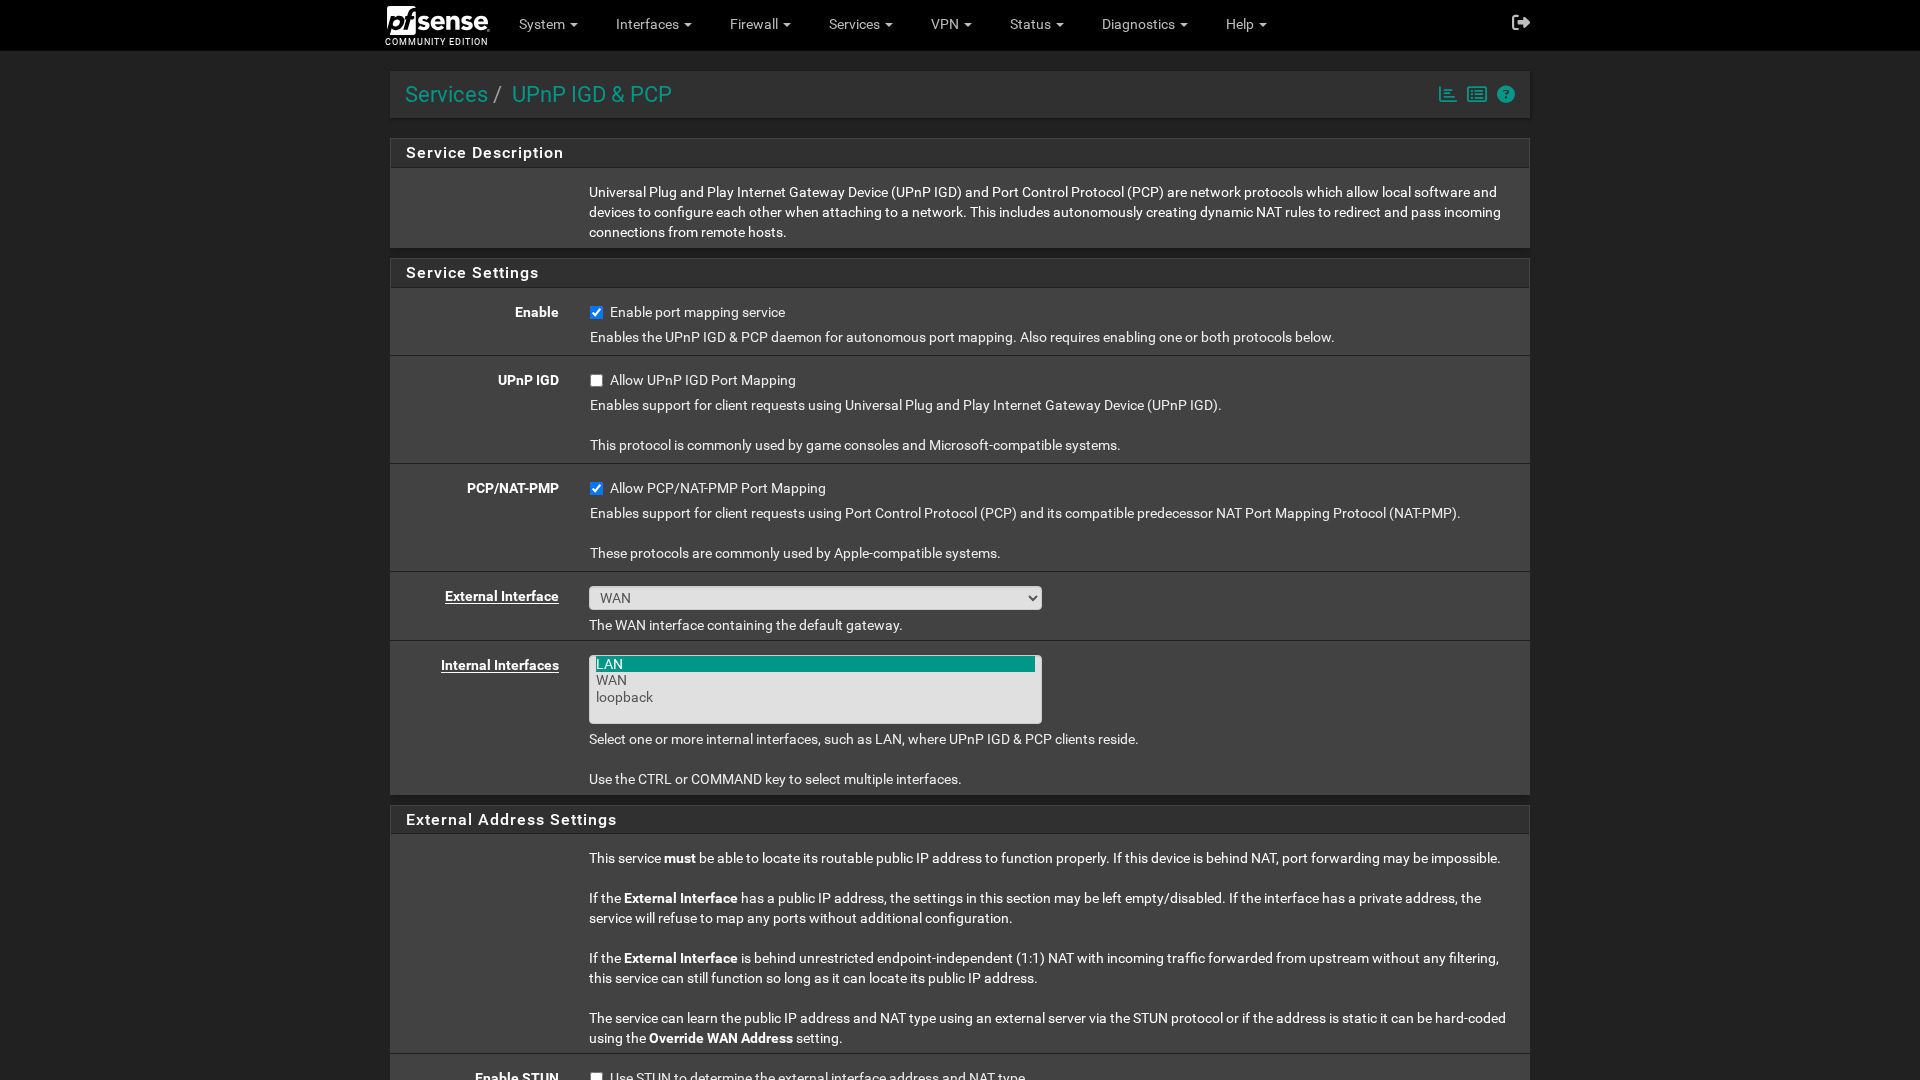
Instead of steps 1 to 3, you can use NAT-PMP. On CE 2.9.0, open Services > UPnP IGD & PCP, tick Enable port mapping service and Allow PCP/NAT-PMP Port Mapping, leave Allow UPnP IGD Port Mapping unticked, and select Save.
Security changes all the time and nothing here is guaranteed, so keep the Tailscale package updated with the rest of pfSense and keep your tailnet’s access controls as narrow as you can.