pfSense vs Ubiquiti comes down to how much time you want to spend on your firewall. For most home users, UniFi is going to win on usability, but for home lab users who want more control and don’t mind the maintenance, pfSense is going to win on flexibility.
I’ve run both at home. I ran pfSense on a Netgate 6100 for over three years with UniFi switches and access points behind it, and in late 2024, I made the switch to a UniFi Cloud Gateway (a UniFi Dream Machine Pro Max).
To keep it simple, pfSense is firewall and router software that you install on hardware of your choice, while UniFi is Ubiquiti’s hardware line (gateways, switches, and access points) that’s managed from one application called UniFi Network. Everything below is current as of October 2026.
Disclosure: Some links below are affiliate links, which means that I earn a percentage of each sale at no cost to you. Thank you for your support.
Hardware: Build Your Own or Buy a UniFi Gateway
pfSense Hardware
pfSense comes in two editions, pfSense CE (Community Edition) and pfSense Plus. CE is free, open source, and has everything that you need for home use, while pfSense Plus is included when you purchase a Netgate appliance and is a yearly subscription on any other hardware.
My Netgate 6100 worked extremely well, but you can bypass Netgate entirely and install pfSense CE on your own hardware, as long as it has at least two network ports (one for WAN and one for LAN). The Protectli Vault FW2B and Protectli Vault FW4B are both still sold, but they’re gigabit devices. Protectli now points buyers to the Protectli Vault V1210 (two 2.5GbE ports) and Protectli Vault V1410 (four).
A mini PC works as well, and for a video in July 2026, I installed pfSense CE on a Beelink EQ14 (Intel N150, in the version with two 2.5GbE ports) that was around 10W at idle in my testing. If you’re buying something specifically for pfSense, I’d at least look at the options with four 2.5GbE ports, which I cover in my guide to the best pfSense hardware.
A pfSense box is a router and firewall ONLY, so you will still need a managed switch and access points. You can get pfSense working with Wi-Fi, but Netgate’s own documentation says that many use cases behave better with an external access point.
UniFi Hardware
With Ubiquiti, the hardware and software come together. A UniFi Cloud Gateway is a router and firewall that also runs UniFi Network, so there’s nothing to install and the management software is license-free.
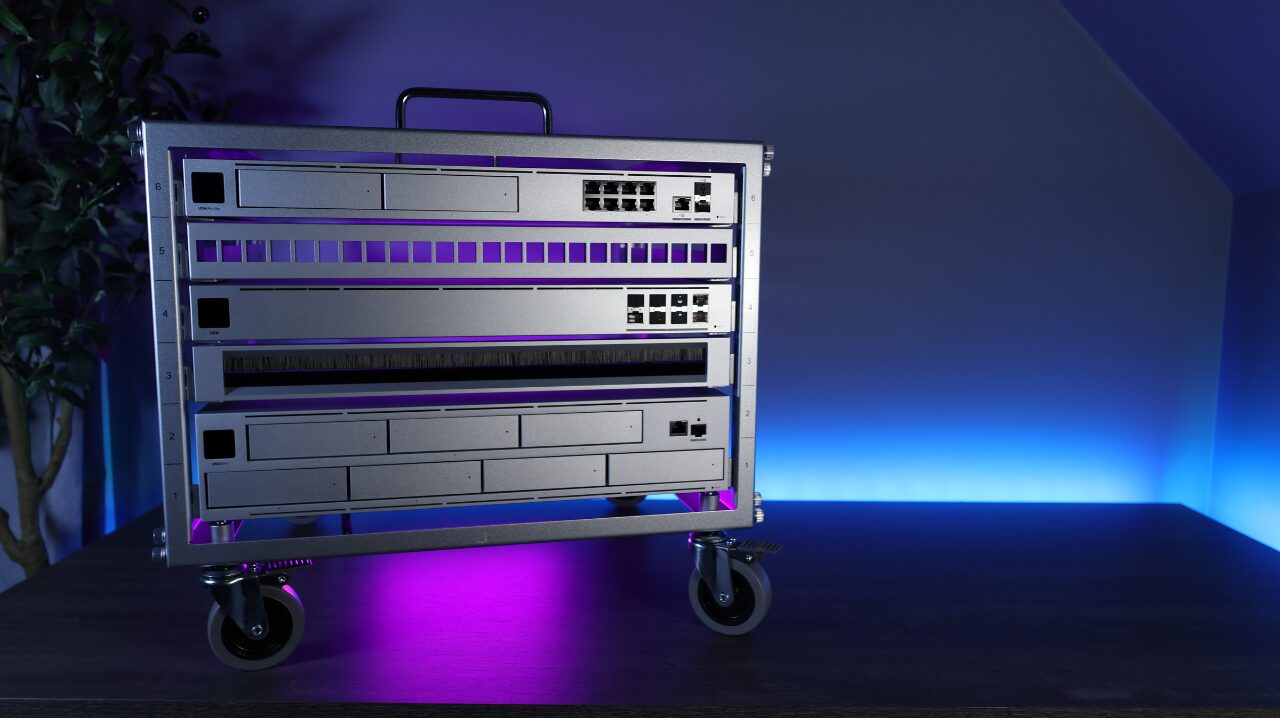
If you’d like an all-in-one device with Wi-Fi built in, look at the Dream Router 7 or UniFi Express 7. If you’re using separate access points, the UniFi Cloud Gateway Fiber is the one I’d tell most people to start with. For a rack, there’s the UniFi Dream Machine Pro Max that I use. I cover the lineup in my guide to the best UniFi router and firewall.
From a cost perspective, the two are actually a lot closer than they were in the past due to mini PC prices rising so much. Ubiquiti’s entry-level gateways (the Cloud Gateway Ultra and UniFi Express 7) list for less than any of the Protectli devices above. If you have a mini PC already, the cost doesn’t really matter since pfSense CE is free.
pfSense vs UniFi Firewall and Software
The software is where the two differ the most, as pfSense gives you more control and UniFi is easier to run. pfSense has a real learning curve and you can get lost very quickly, since you’re responsible for every single firewall rule, every update, and every configuration decision, but in return, you can customize just about anything.
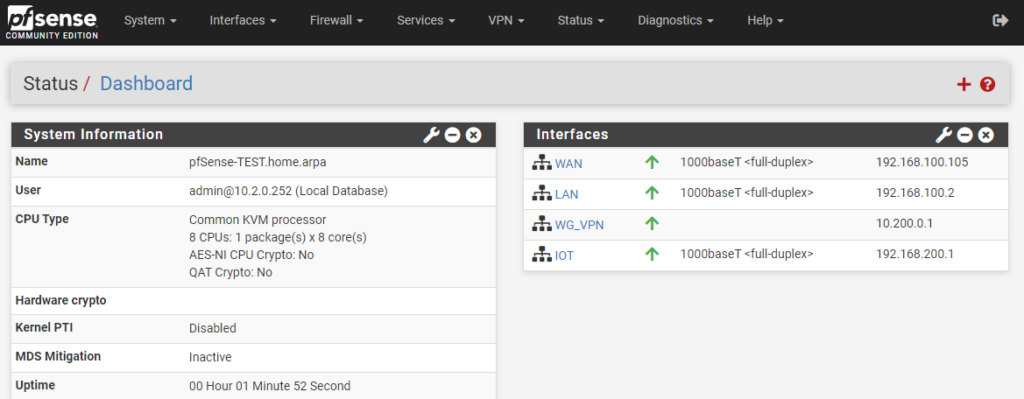
There’s also a full package ecosystem, so you can install things like pfBlockerNG, HAProxy, and ACME right from the Package Manager.
UniFi Network (officially the UniFi Network Application, and previously the UniFi Controller) is the opposite. You get one dashboard that covers everything from your switches and access points to your firewall, a faster initial setup, and potentially less maintenance, but you give up some of that control.
Firewall Rules
pfSense denies everything that isn’t explicitly allowed, evaluates rules from top to bottom, and has the deeper firewall controls of the two. With that said, it’s gotten a lot better on the Ubiquiti side. Since UniFi Network 9.0, there’s a zone-based firewall where your VLANs, WANs, and VPNs are grouped into zones, and you set the policies between those zones in a Zone Matrix. I have my VLANs and the zone-based firewall configured on my own gateway, and for a home network, it’s generally easier to manage.
IDS/IPS
This is the one that I think is a massive difference, and it’s ultimately what pushed me to Ubiquiti (but could be what pushes you to pfSense). On pfSense, IDS/IPS comes from packages like Snort or Suricata, and the configuration is very granular.
I wanted to implement IDS/IPS on pfSense and didn’t need a complicated setup, but as soon as I looked into Snort, I knew I had hours of work ahead of me. If you need that level of customization, pfSense is actually a benefit, but for me, it ended up being a downside.
With a UniFi Cloud Gateway, it’s built in and managed by a toggle and some basic controls. Open Settings, select CyberSecure, then Protection, turn on Intrusion Prevention, select your networks, and set the Detection Mode to Notify (IDS) or Notify and Block (IPS). There’s an optional paid subscription that expands the threat signature database, but it is not required. It’s not as powerful as what you can build on pfSense, but it’s literally one screen!
WireGuard, OpenVPN, and Site-to-Site VPNs
UniFi gateways have had a built-in WireGuard server since UniFi OS 3.0, which reached the Dream Machine and Dream Machine Pro in May 2023. An OpenVPN server followed in UniFi Network 7.4, and there’s also Teleport (a zero-configuration VPN powered by WireGuard) and a VPN client for connecting the gateway out to a VPN provider. An older version of this article said that UniFi devices couldn’t run WireGuard or OpenVPN.
On pfSense, WireGuard is a package that you install from the Package Manager, and OpenVPN and IPsec are there as well.
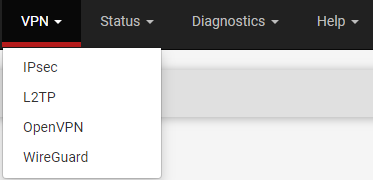
WireGuard was my primary VPN on pfSense for years and it was totally reliable, but even something like a WireGuard VPN took many steps to set up. When I switched, I moved it to my Dream Machine Pro Max, and WireGuard on UniFi devices has been extremely stable for me.
The main difference left is site-to-site. As of October 2026, a UniFi gateway’s site-to-site options are IPsec, OpenVPN, and Site Magic SD-WAN (which only connects UniFi gateways to each other). WireGuard isn’t on that list, and pfSense has a WireGuard site-to-site option. If you want maximum control over routing, firewall rules, peer management, or advanced VPN design, pfSense still gives you more flexibility.
As with anything security related, both platforms change with every update and nothing here is guaranteed.
Running pfSense With UniFi Switches and Access Points
You don’t have to pick one, as you can use pfSense with UniFi switches and access points behind it. I ran this exact setup for years and overall, it worked very well. You configure the VLANs in pfSense, then you pass those VLANs through to your managed switches and access points.
The catch is that without a UniFi gateway, you need somewhere to run UniFi Network, so you’ll have to either purchase a CloudKey+ or self-host UniFi Network. Ubiquiti’s current option for self-hosting is UniFi OS Server, which replaces the legacy UniFi Network Server. I self-hosted UniFi Network on Windows back in 2022, which is where the two screenshots below are from.
What you give up is everything that requires a UniFi gateway, meaning the zone-based firewall, IDS/IPS, the VPN servers, Teleport, and Site Magic. With pfSense in front, UniFi Network only manages your switches and access points, so you’re managing your network in two places.
Anytime I went to set something up in pfSense, it was an endeavor, and I’d have to spend half an hour or an hour reading documentation, and I got tired of that.
pfSense vs Ubiquiti: Which One Should You Use?
For most home users, UniFi is the right choice. Both now cover VLANs, firewall rules, IDS/IPS, WireGuard, and OpenVPN, so Ubiquiti vs pfSense isn’t the feature decision that it used to be.
- Buy a UniFi Cloud Gateway if you want a home network that’s fast to set up, managed from one dashboard, and generally easier to maintain.
- Go with pfSense if you’re a home lab user who wants granular firewall rules, Snort or Suricata configured exactly how you’d like, and flexible VPN options like WireGuard site-to-site, and you don’t mind the maintenance.
- Run pfSense with UniFi switches and access points if you want that control at the firewall, but still want UniFi for everything behind it.
If you decide to build your own, it’s worth looking at pfSense vs. OPNsense as well.
Switching from pfSense to UniFi was actually a very tough decision for me, because when something is working at the firewall level, you really don’t want to change it, but I was spending a lot of time maintaining it. If you’re using pfSense and still love it, I’m not suggesting that you change, but for my individual needs, UniFi was the right decision, and if you’re looking to simplify your network, it’s most likely the right decision for you too.